Meet Edera IRL

Heading to KubeCon + CloudNativeCon North America in Salt Lake City? So are we. Looking for a bit of fun? Come to the Edera Ski Mountain at Activation Zone 143 to test your mini golf skills.

Ready to warm up? Follow the trail to the Edera Chalet at Booth 226 for a look at what hardened runtime isolation actually looks like in production, plus limited-edition swag worth the trip up the mountain.

No shared kernel. No shared chair.

Every Workload rides alone

CYA for the Agentic Era: Contain Your Agents

Containing your architecture was step one. In a world of autonomous AI agents running code, calling tools, and touching production, you need to Contain Your Agents.

Follow the trail to Booth 226 and watch it run live: contained AI agents, scoped access, secure multi-tenancy, and GPU isolation that keeps tenant data where it belongs. This is isolation that stops an attack before your detection tool ever fires an alert.

Give agents access. Not credentials.

Axies in Action

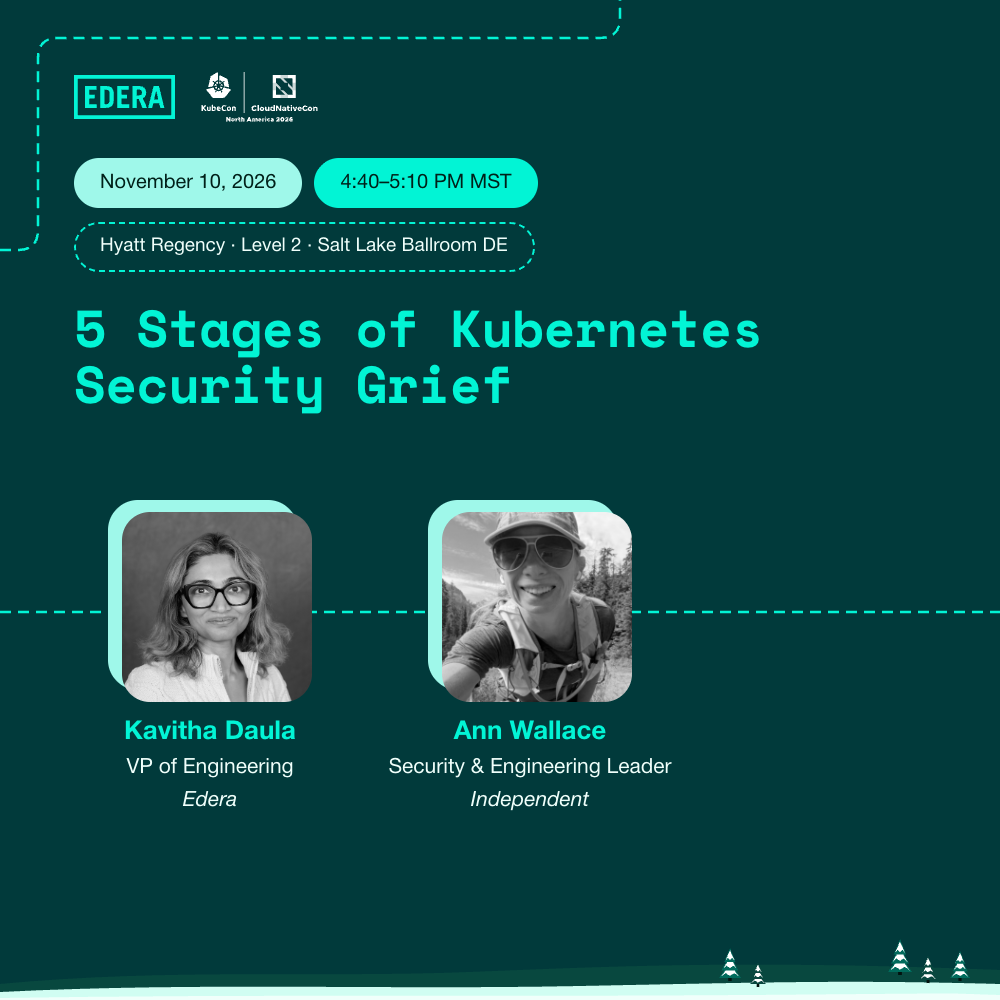
5 Stages of Kubernetes Security Grief

5 Stages of Kubernetes Security Grief

Denial: our namespace isolation is fine.

Anger: why does everything touch the kernel?

Kavitha Daula pairs the kernel-level reality, the shared surfaces and the failures that leave no CVE and no alert, with what teams actually say out loud, alongside Ann Wallace. It's structured as a comedy, but every stage maps to a real failure mode, and they land on the one that matters: you can't bolt on isolation, you have to build it in.

Learn more

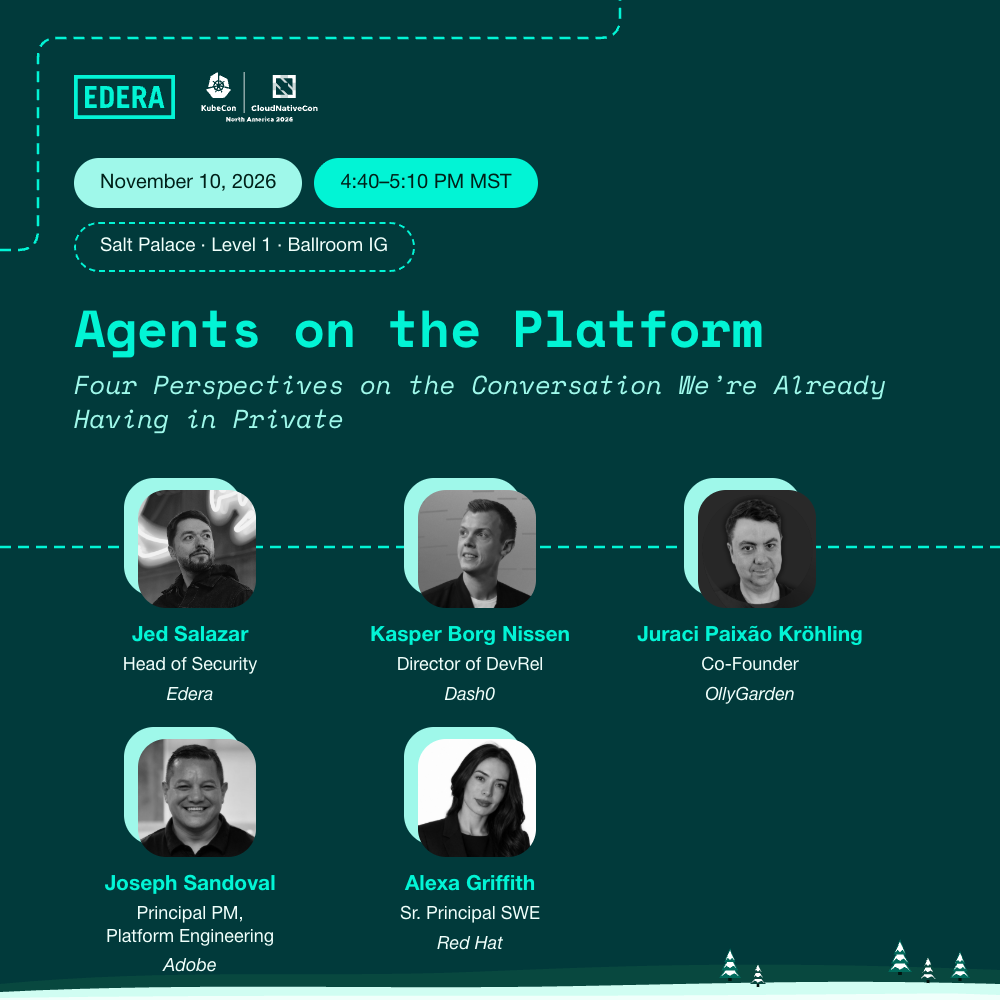
Agents on the Platform

Agents on the Platform

Four Perspectives on the Conversation We're Already Having in Private

AI and agentic systems are becoming production workloads on cloud-native platforms, and the hard questions land with platform teams: how agents identify themselves, what they can access, how fast they can act, what they cost, and what evidence the platform needs when something goes wrong.

The panel brings together four perspectives that usually get handled separately, examining what shared infrastructure must guarantee as AI systems become governable workloads, from identity for non-human callers to observability, policy and blast-radius controls, and accountability across application, model, and vendor.
Learn More

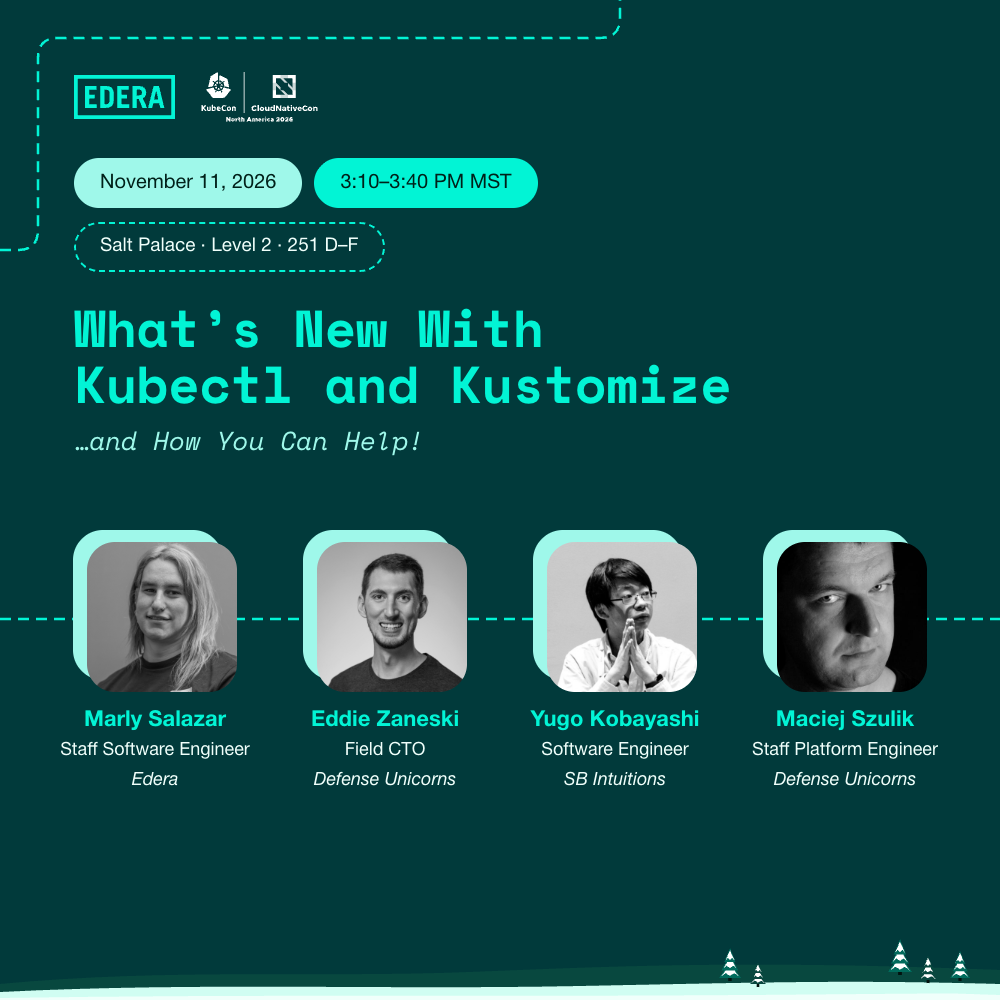
What's New With Kubectl and Kustomize

What's New With Kubectl and Kustomize

...and How You Can Help!

Ever wondered how kubectl and kustomize features actually get designed and built, or why that feature request of yours stalled?

The Kubernetes SIG CLI maintainers pull back the curtain: the breakthroughs shipped this past year, a sneak peek at the roadmap, and a live forum to help shape what comes next. Seasoned contributor or complete beginner, come ask your burning questions and make your first contribution.

Learn More

More Runs to Explore

Can't make a session, or want to go deeper? A few more trails from the Edera team.

Thinking Outside the Sandbox

Thinking Outside the Sandbox

Our white paper for platform and security architects running untrusted code, AI agents, or multi-tenant workloads.

It’s time for a new model: assume breach at the runtime layer and isolate every workload in hardware. No form, no email, just the PDF.

resource-idc-brief

IDC Analyst Brief

When Prevention Cannot Be Assumed

IDC on why prevention alone falls short for AI workloads, and what real containment looks like when you can't assume an attack gets stopped at the door.

Edera on AWS Graviton

Edera on AWS Graviton

Edera's hypervisor-backed isolation now runs on AWS Graviton bare metal, so untrusted, build, and AI-agent workloads can share arm64 hosts without sharing a kernel. Start with the overview, then the technical deep dive on getting Xen onto Arm SystemReady platforms

resource-agent-runtime

Freeze It, Fork It, Let It Run

AI agents start fast, carry state, and scale to thousands. Edera's Agent Runtime runs each in its own private-kernel microVM on Kubernetes you already own. Snapshot and restore on demand. Live-fork with copy-on-write to clone agents cheaply.

Take On the Edera CTF

Take On the Edera CTF

Get hands-on with the Edera runtime using kubectl and the protect cli in the gamified CTF challenge. You have audit-only access on a single Kubernetes node. Troubleshoot insecure configurations and find the 6 hidden flags to win prizes.

Book A Meeting

Frequently asked questions

What is Edera?

Edera is a container-native Type-1 hypervisor that eliminates the trade-off between container security and performance. It isolates every workload in its own lightweight “zone,” preventing container escapes by design while maintaining near-native speed and full Kubernetes compatibility.

How does Edera make containers more secure?

Traditional containers share the same Linux kernel, which creates risk of container escapes and lateral movement. Edera replaces that shared foundation with per-container micro-VMs, providing complete workload isolation. This design blocks privilege-escalation attacks and zero-days that exploit the kernel — without needing new tooling or specialized hardware.

Is Edera suitable for AI & GPU workloads?

Absolutely. Edera provides GPU workload isolation that prevents data leakage between tenants and protects against GPU driver vulnerabilities — critical for secure AI training and inference at scale.

Can Edera support confidential or regulated workloads?

Yes. Edera complements confidential computing models by providing strong software-based isolation that doesn’t depend on proprietary hardware. It helps organizations meet zero-trust and compliance requirements for sectors like finance, healthcare, and government.

What kind of companies use Edera?

Edera is built for platform engineering and security teams running large Kubernetes or AI infrastructures. Enterprises adopt it to enable secure multi-tenancy, reduce infrastructure costs, and achieve security without sacrifice — whether on-prem, in public cloud, or at the edge.