env zero enables platform teams to deliver infrastructure 10x faster without losing control, with standardized, governed workflows at the speed and scale of AI.
The Replit agent that deleted a production database during a code freeze wasn't compromised. Neither was the Gemini CLI run that turned a file reorg into data loss.
Both had permission to do what they did. Nobody had reviewed it.
OIDC credentials in env zero shared one audience claim across AWS, Azure, GCP and Vault, so a token minted for one was replayable against another.
v2 issues a provider-specific aud. Opt-in per credential, v1 untouched.
-auto-approve applies to terraform destroy exactly the way it applies to terraform apply.
It exists so pipelines don't wait on someone typing yes. Agents reach for it for the same reason.
Infrastructure risk models assume two actors: someone who makes a mistake, and an attacker who shouldn't have access.
An agent with a real credential, inside permissions you approved, reasoning its way to a destructive action, is neither.
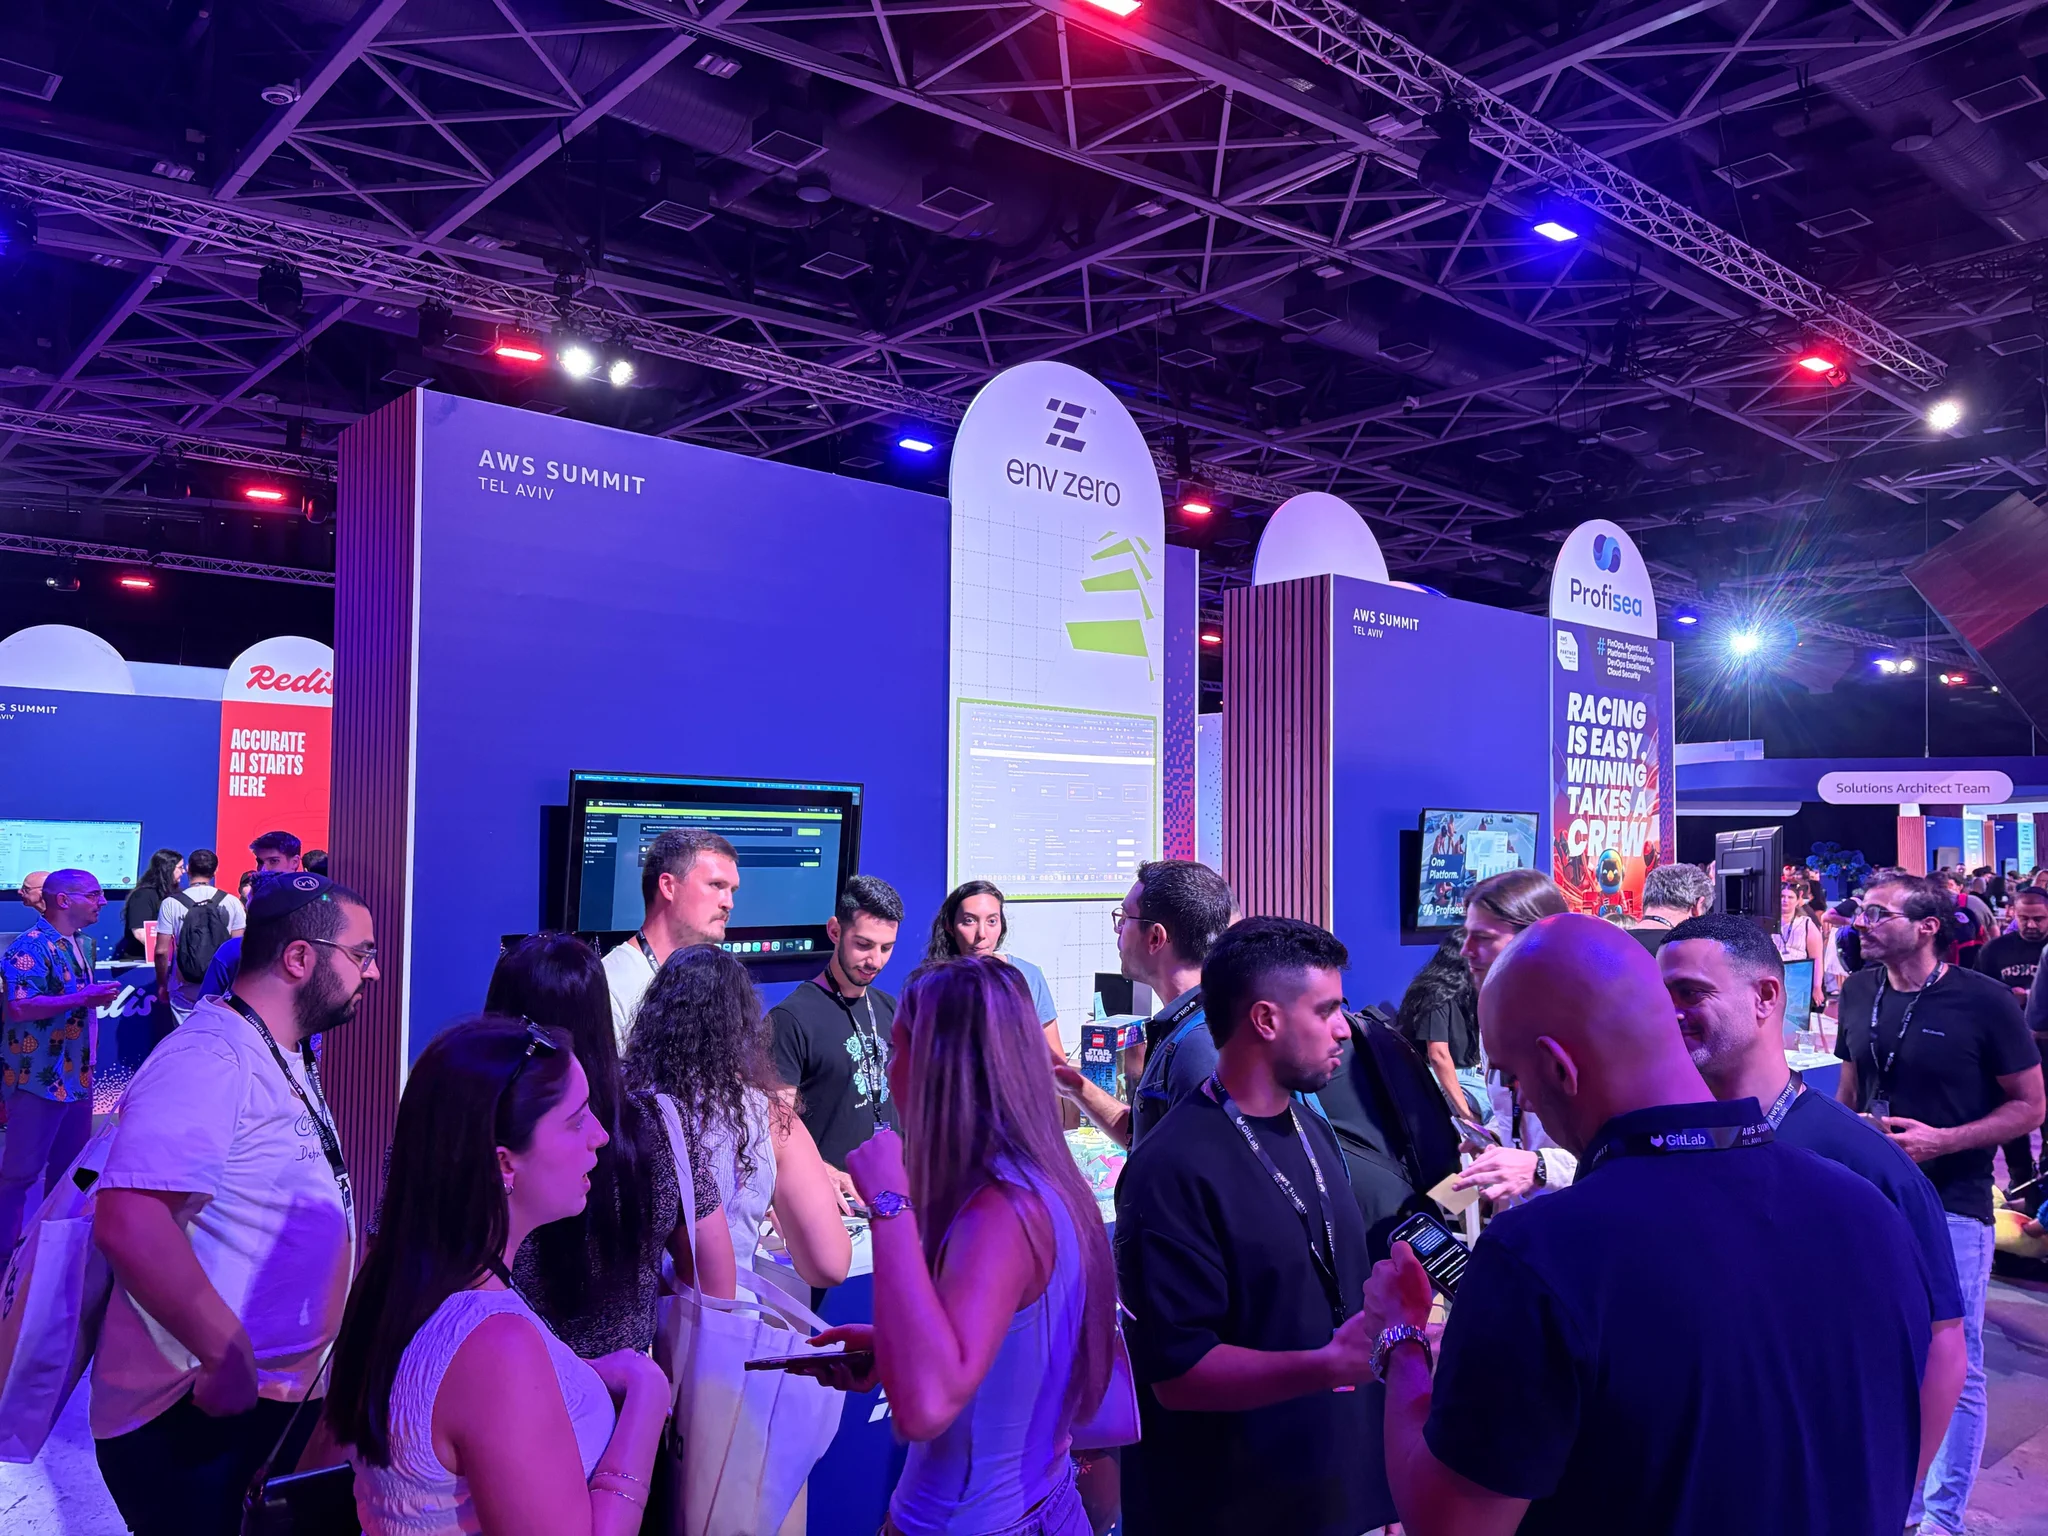
🏗️ Having an amazing show at AWS Summit Tel Aviv! Come visit the env zero engineers at Booth S15 for a sneak peek at what we're building, a limited edition t-shirt, and chance to win a LEGO Star Wars Grogu.
תערוכה מדהימה בכנס AWS Summit תל אביב! בואו לבקר את מהנדסי env zero