Driven by a “Liquid Software” vision, the JFrog Software Supply Chain Platform powers organizations to build, manage, and distribute software quickly & securely
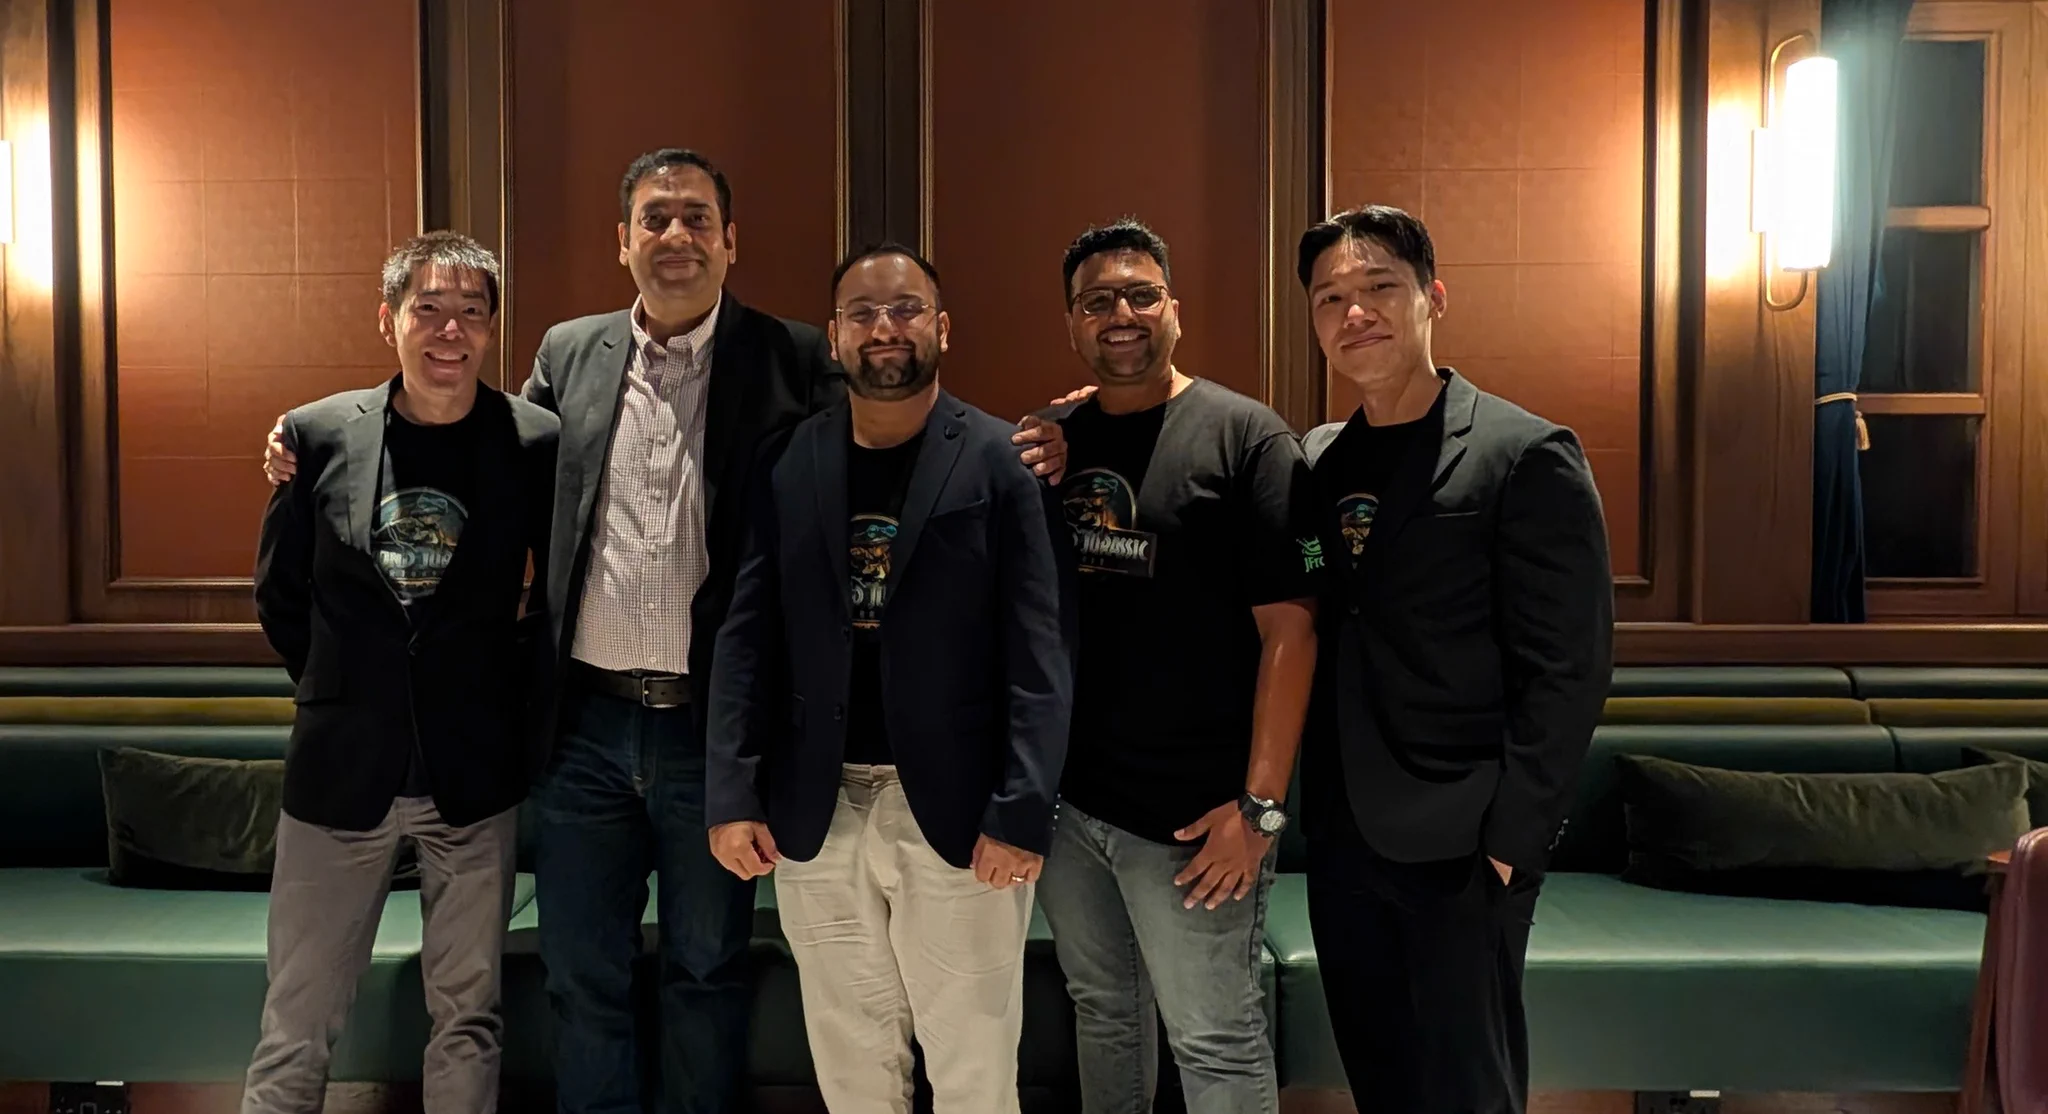
That is a wrap on our roundtable evening in Singapore! 🇸🇬 ✨
Security and technology leaders from across the region joined us for an evening of practical conversations about the future of software delivery in the age of AI. ⚡️
Here’s what stood out:
🔹 Blind spots in modern
🌟 JFrog has been named a Leader in the first Gartner® Magic Quadrant™ for Software Supply Chain Security; placed highest in Ability to Execute.
The industry is finally recognizing a hard truth:
You cannot secure the #SoftwareSupplyChain by securing one element alone or
📣 Attention self-managed JFrog users: Linux kernel vulnerability CVE-2026-98432 poses a critical risk to underlying host OS environments.
While JFrog products aren't vulnerable, some use MPTCP and could be affected by your host kernel vulnerability.
What to do:
🔍 Check your
Malicious packages and compromised build pipelines rarely announce themselves.
@nullcon Berlin on 5 to 6 November brings #softwaresupplychain research, from dependency compromise to CI/CD attacks, together with the people who uncover these threats.
Come meet the JFrog team to
#PHP2Shell. The #LiteLLM supply chain compromise. #Brotli2Shell.
Black October has given security leaders plenty of headlines—and one urgent question: “Are we exposed?”
How quickly could your team give a confident answer?
Knowing about an incident is only the beginning. You