

Avoiding Dynamic Sql Query Construction establishes a resilient baseline for enterprise database architectures. At Secure Coding Practices, engineering teams strictly separate executable logic from variable data streams.
Eliminating raw string concatenation neutralizes severe SQL injection threats across all endpoints. Pre-compiled execution plans optimize database server performance under heavy concurrent loads.
Implementing robust parameterization protocols secures sensitive enterprise data assets seamlessly. Consistent architectural patterns prevent unauthorized schema modifications and unauthorized data extraction.
Key Architectural Security Enhancements
Eliminating dynamic string concatenation stabilizes execution plans and enforces strict parameter boundaries.
- Avoiding Dynamic Sql Query Construction guarantees absolute separation of executable SQL commands from user inputs.
- Pre-compiled routines eliminate repetitive parsing overhead during high-volume database transaction spikes.
- Structured access controls leverage native database driver binary binding mechanisms effectively.
Why is Raw Concatenation a Critical Vulnerability?
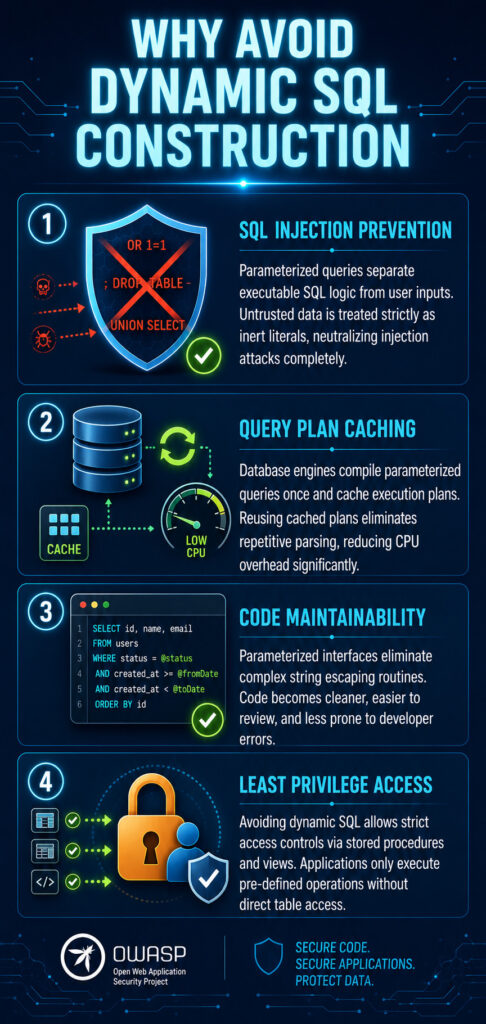
Dynamic query building merges untrusted input directly into executable SQL text. This fundamental flaw allows attackers to append arbitrary relational control characters. When database engines parse manipulated strings, they execute unintended relational commands.
Avoiding Dynamic Sql Query Construction prevents attackers from hijacking the query execution tree. Systems relying on raw text interpolation face constant risks of data exfiltration. Automated security scanners routinely flag these patterns as critical architectural defects.
Enterprise development standards mandate the complete removal of inline query building. Moving toward structured driver abstractions ensures consistent security across microservice environments.
How Do Pre-Compiled Plans Outperform Dynamic Queries?
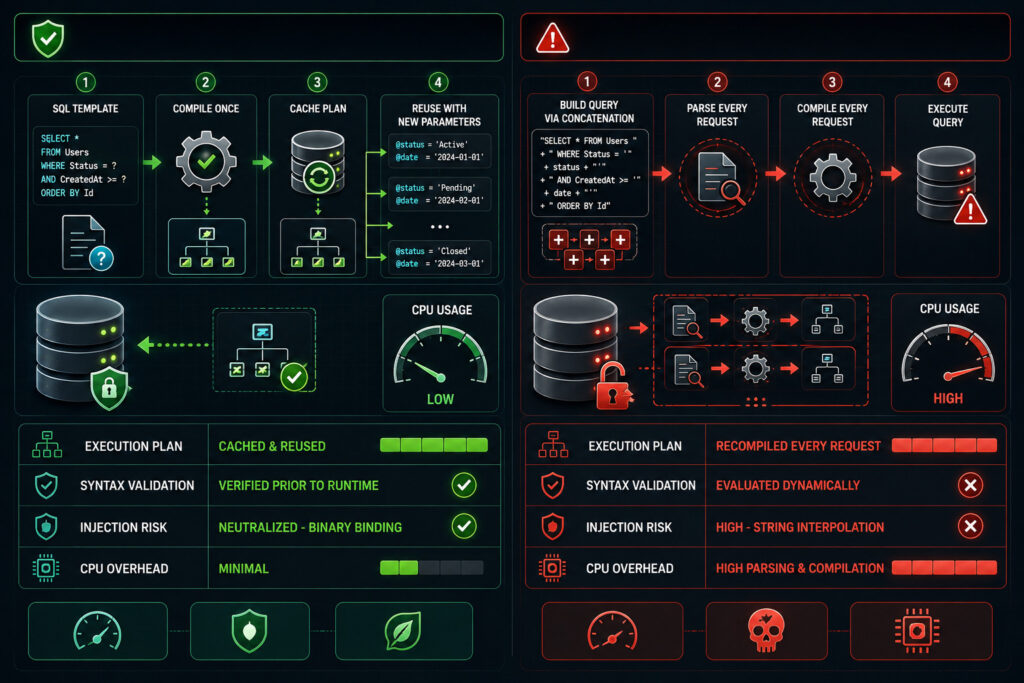
Database performance relies heavily on query parsing and execution plan generation. Dynamic SQL forces the engine to compile a new plan for every request, highlighting the urgent need for parameterized queries for db security in enterprise systems. This repetitive overhead severely degrades transaction throughput during peak usage periods.
Avoiding Dynamic Sql Query Construction allows databases to cache and reuse execution templates. The engine compiles structural logic once and maps variable parameters in memory. This reuse cuts CPU utilization and stabilizes backend latency metrics.
| Evaluation Metric | Parameterized Execution | Dynamic Query Construction |
| Execution Plan | Cached and reused efficiently | Recompiled for every incoming request |
| Syntax Validation | Verified prior to runtime execution | Evaluated dynamically during execution |
| Injection Risk | Neutralized via binary parameter binding | High risk from string interpolation |
| CPU Overhead | Minimal overhead during execution | High parsing and compilation overhead |
How Does Parameterization Neutralize Injection Vectors?
Parameter binding protocols transmit untrusted inputs separately from the command syntax. The database driver maps these inputs directly into pre-allocated memory slots. This binary separation prevents literal values from being evaluated as executable code.
Avoiding Dynamic Sql Query Construction shifts the security burden to native driver mechanisms. Developers define exact data types and lengths for each parameter placeholder. The database engine strictly enforces these type constraints during execution.
Microsoft engineers emphasize the architectural superiority of explicit parameterization strategies:
“Using parameterization gives you the advantage that you can clearly specify the data type and avoid pitfalls as well as the final T-SQL statement generated will reference the parameters as variables and not directly use the user defined input to generate the statement.” – Microsoft Dynamic SQL & SQL Injection Blog
How Can SQL Views Enhance Granular Access Controls?
Enforcing the principle of least privilege requires strict database boundary definitions. Applications should never possess direct read or write access to core tables. Abstracting data structures through database views minimizes exposure surfaces significantly.
Avoiding Dynamic Sql Query Construction aligns perfectly with restricted view-based access models. Views present specific row and column subsets based on caller context. This abstraction layer prevents compromised application credentials from extracting hidden schema data.
The OWASP foundation highlights views as a primary defense-in-depth mechanism:
“You can use SQL views to further increase the granularity of access by limiting the read access to specific fields of a table or joins of tables.” – OWASP SQL Injection Prevention Cheat Sheet
What Are The Challenges of Legacy Migration?
Refactoring legacy codebases requires systematic auditing of all database access layers. Legacy systems often rely heavily on complex string manipulation routines. Converting these modules requires rigorous testing to verify how parameterized queries prevent sql injection.
Avoiding Dynamic Sql Query Construction within monolithic applications requires phased deployment strategies. Teams must utilize Static Application Security Testing (SAST) to map vulnerabilities. DAST scanners then verify that parameterized endpoints handle boundary conditions properly.
Modern Object-Relational Mapping (ORM) frameworks automate much of this refactoring effort. However, developers must still audit custom native queries embedded within ORM configurations. Validating driver-level parameterization remains mandatory for compliance certifications.
How Do ORM Frameworks Prevent String Interpolation?
Avoiding Dynamic Sql Query Construction becomes a seamless byproduct of proper Object-Relational Mapping (ORM) usage. ORM frameworks abstract native SQL syntax through object-oriented APIs, allowing developers to interact securely with domain entities instead of raw database connection interfaces.
- Executing raw, unparameterized native queries through ORM bypass functions reintroduces critical string interpolation vulnerabilities immediately.
- Frameworks automatically generate parameterized database queries, handling type mapping and parameter binding natively to reduce manual coding errors.
- Security teams must enforce strict code review policies to prevent the use of native query bypass features within ORM configurations.
Securing Backend Microservices Architecture
Credits: Professor Messer
Microservices architectures demand decentralized database access patterns where isolated datastores prevent lateral movement. Avoiding Dynamic Sql Query Construction ensures every service boundary remains completely sealed and scales securely across enterprise environments.
- Automated deployment pipelines simplify security audits by rejecting pull requests containing raw SQL strings.
- Parameterized connections optimize memory usage within localized database connection pools.
- Pre-compiled efficiency prevents CPU starvation across distributed backend node clusters.
Handling Dynamic Sorting and Filtering Requirements
Applications frequently require dynamic ordering or complex filtering logic mechanisms. Parameterizing column names directly is impossible within standard relational database engines. Developers must implement strict allow-listing patterns for these specific dynamic requirements.
Avoiding Dynamic Sql Query Construction remains possible even with complex dynamic filtering. When using prepared statements java php, applications map user input to pre-defined static column identifiers internally. This exact mapping prevents arbitrary strings from reaching the database execution context.
Backend services reject any sorting parameters falling outside the authorized allow-list. This guarantees the database engine executes only thoroughly validated schema columns. Strict validation safeguards the structural integrity of dynamic interface queries.
Continuous Security Testing for Database Layers
Automated security testing pipelines validate parameter isolation across all deployment environments. Dynamic Application Security Testing evaluates runtime endpoints using fuzzed payload sequences. These tools ensure database drivers handle unexpected character encodings properly.
Avoiding Dynamic Sql Query Construction requires continuous validation against regression defects. Developers might inadvertently merge legacy query builder utility classes into production branches. Automated regression tests immediately flag these unparameterized database interface regressions.
Security operations teams monitor database query logs for anomalous syntax structures. Identifying raw text interpolation in logs indicates a bypassed validation layer. Proactive telemetry ensures rapid incident response and immediate architectural remediation.
FAQ
Why is Avoiding Dynamic Sql Query Construction critical for security?
Raw string concatenation allows attackers to alter the fundamental query logic. Using parameterized interfaces ensures inputs are treated strictly as inert data values. This isolation neutralizes injection vectors and stabilizes database query execution entirely.
How do execution plans optimize parameterized query performance?
Database engines compile parameterized queries once and cache the resulting execution plan. Subsequent requests reuse this plan by simply swapping memory variables. This eliminates repetitive parsing overhead and reduces overall server CPU consumption significantly.
Can Object-Relational Mapping frameworks completely prevent SQL injection?
ORM frameworks prevent injection when developers use standard object-oriented querying methods exclusively. Invoking native raw query functions within an ORM reintroduces severe security risks. Developers must enforce strict parameter binding even when utilizing advanced ORM features.
What role do SQL views play in database security architecture?
SQL views create restricted virtual tables exposing only necessary data subsets. They enforce the principle of least privilege by abstracting underlying core schemas. Compromised application accounts cannot query restricted data hidden behind authorized database views.
How do static analysis tools detect unparameterized database queries?
SAST scanners parse application source code to trace string variable concatenations. They flag instances where untrusted inputs flow directly into database execution functions. This automated scanning prevents insecure code from reaching production deployment pipelines.
Fortifying Database Architecture Against Injection Threats
Avoiding Dynamic Sql Query Construction provides the absolute foundation for secure enterprise database architectures. Encapsulating queries within parameterized interfaces completely neutralizes devastating injection vulnerabilities. Pre-compiled execution templates maximize transaction throughput and reduce computational overhead across server clusters.
Integrating advanced abstraction layers like SQL views further enforces strict least-privilege access models. Engineering teams must eliminate legacy string concatenation practices entirely to secure sensitive backend systems. Embracing modern parameterization protocols protects critical enterprise data against continuous automated exploitation.
To master secure database design and advanced backend threat mitigation techniques, join our secure coding bootcamp today.
References
- https://learn.microsoft.com/en-us/archive/blogs/raulga/dynamic-sql-sql-injection
- https://cheatsheetseries.owasp.org/cheatsheets/SQL_Injection_Prevention_Cheat_Sheet.html#enhancing-least-privilege-with-sql-views
