
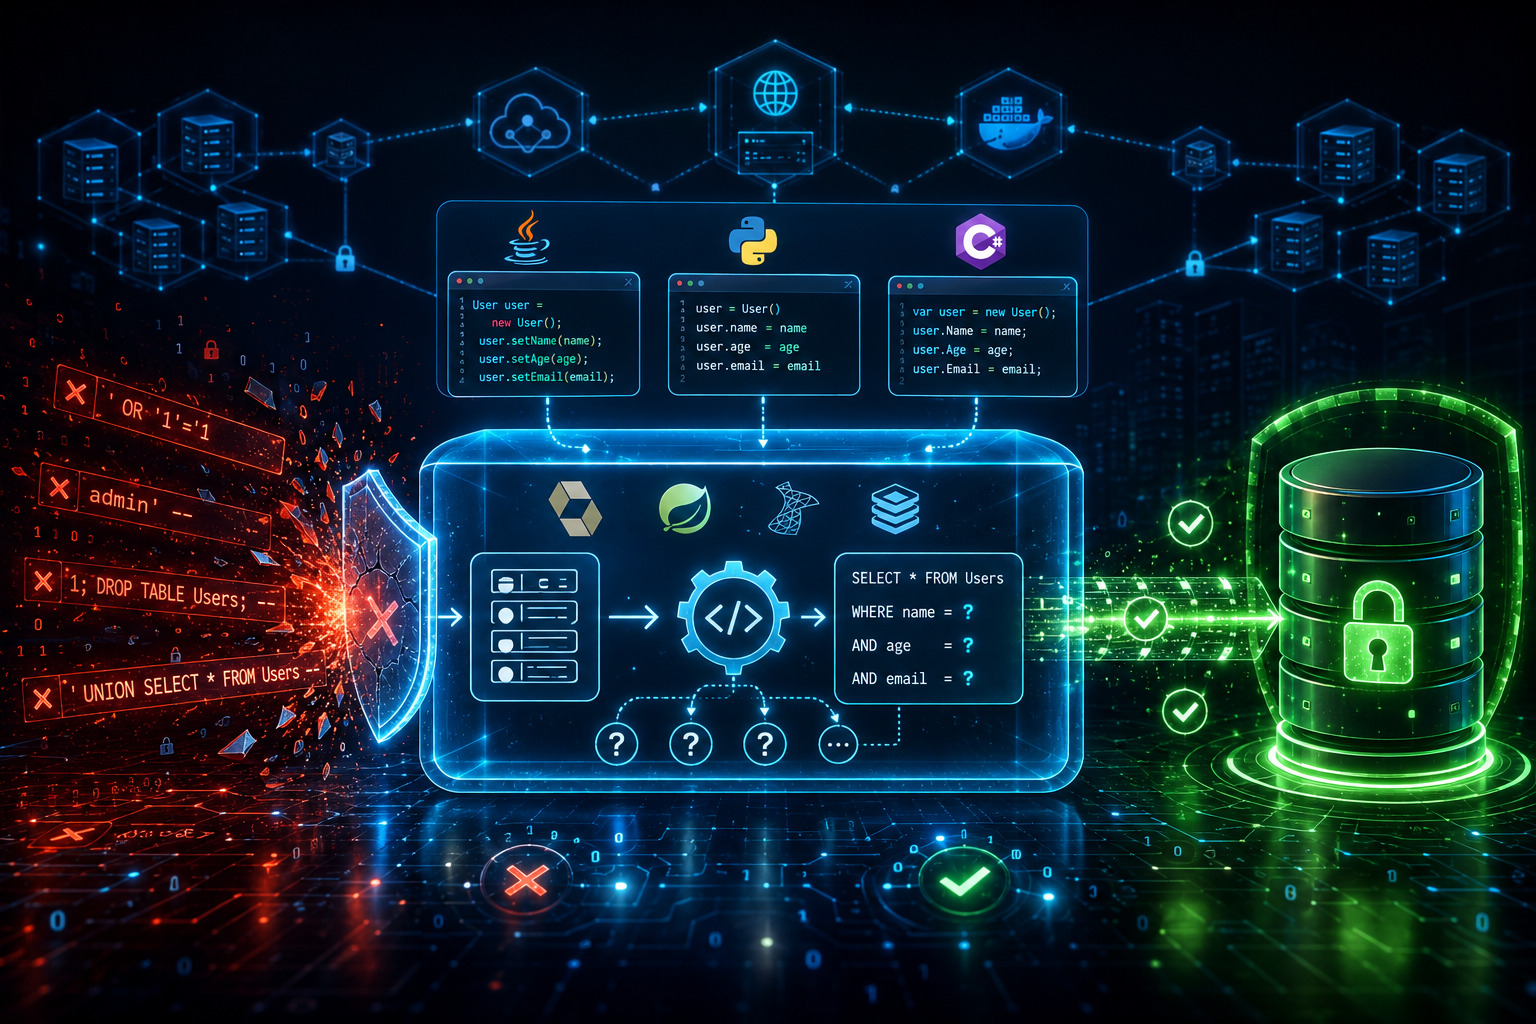

Implementing Parameterized Queries ORM Framework is essential for building resilient, high-throughput enterprise applications. At Secure Coding Practices, backend developers leverage modern Object-Relational Mapping tools to handle data abstraction without exposing database layers to SQL injection vulnerabilities.
ORM frameworks automatically convert literal input values into bound parameters, separating command logic from variable data. This structural isolation prevents malicious payload execution while enabling database engines to cache execution plans efficiently.
Adopting parameterized ORM patterns establishes an impenetrable security perimeter, simplifies database access code, and ensures long-term system maintainability across complex enterprise backend architectures.
ORM Abstraction Layers Enforce Automated Parameterization and Execution Speed
Automating database query construction through ORM parameter binding eliminates manual sanitization errors while optimizing server-side query processing.
- Implementing Parameterized Queries ORM Framework automatically separates SQL command structure from user variable inputs.
- Modern ORM engines bind literal values to database placeholders to prevent SQL injection vulnerabilities by default.
- Pre-compiled query structures generated by ORMs allow database servers to reuse cached execution plans for maximum throughput.
How Does Implementing Parameterized Queries ORM Framework Safeguard Enterprise Applications?
Implementing Parameterized Queries ORM Framework allows software development teams to abstract database interactions while maintaining strict security controls. Modern ORM libraries separate SQL query logic from incoming user data before sending statements to the database driver. This structural boundary guarantees that untrusted inputs are evaluated purely as data literals rather than executable commands.
Beyond robust defense against injection attacks, utilizing an ORM layer simplifies database management across complex codebases. Instead of writing custom string escaping algorithms, developers rely on built-in object relational mappings that parameterize inputs automatically. This minimizes human error during feature development and accelerates time-to-market for enterprise software products.
Furthermore, parameterized ORM operations allow database engines to optimize statement compilation through cached execution plans. When queries use standardized parameter placeholders, database servers avoid re-parsing SQL statements for every unique user request. The resulting performance stability ensures consistent response times even under heavy application workloads.
What Distinguishes Automated ORM Parameterization From Raw SQL Concatenation?
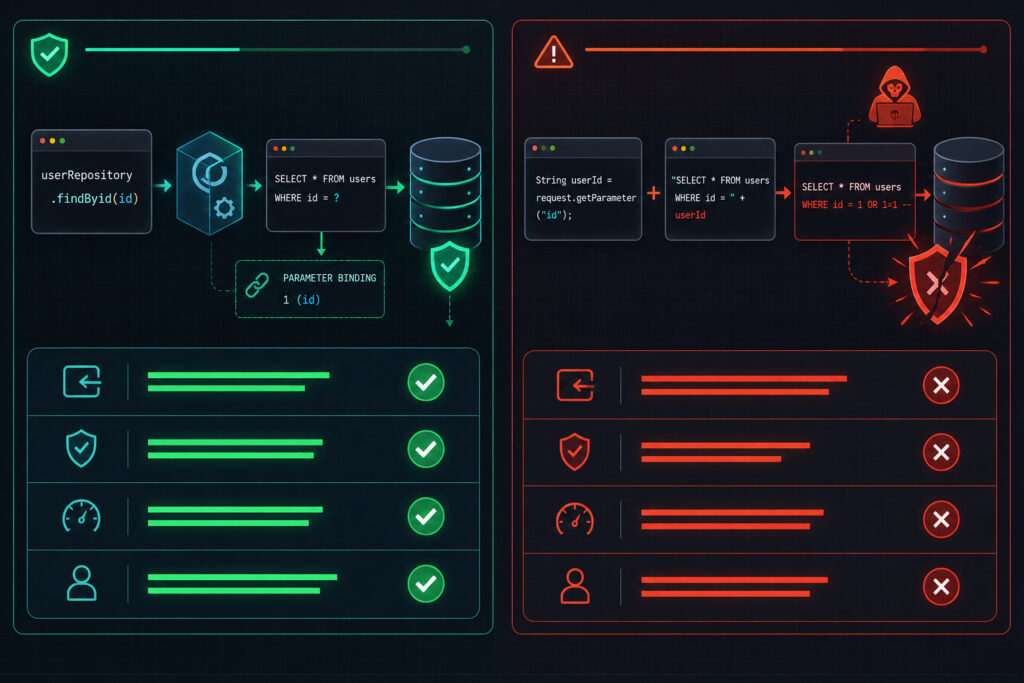
Implementing Parameterized Queries ORM Framework provides a structured abstraction layer that eliminates the security risks associated with manual query construction. When backend services build queries using raw string concatenation, database engines treat incoming user inputs as part of the executable command structure.
For a deeper analysis of how driver-level parameter binding protects enterprise data pipelines, read our guide on parameterized queries for db security across backend systems.
Modern ORMs automatically convert object-level queries into prepared statements before dispatching them to the database driver. This automated translation ensures that input parameters are isolated from structural SQL logic throughout the query execution life cycle.
| Operational Aspect | Automated ORM Parameterization | Legacy Raw String Concatenation |
| Input Handling | Binds literal values directly to isolated parameter placeholders | Injects raw user strings directly into executable SQL statements |
| SQL Injection Risk | Zero; untrusted inputs cannot modify internal query logic | High; malicious strings can alter database command structures |
| Query Compilation | Pre-compiles statement templates to maximize execution plan caching | Re-parses unique statement strings repeatedly on every request |
| Developer Overhead | Handles parameter binding automatically via framework methods | Requires manual string sanitization and fragile escaping routines |
How Does API Standardization Complement ORM Parameterization?
Implementing Parameterized Queries ORM Framework forms a critical defense layer within backend architectures, but comprehensive application security requires end-to-end data validation starting at the API boundary.
When enterprise applications accept incoming HTTP requests, standardizing API interface contracts ensures that parameter types are strictly validated before reaching database abstraction layers. Combining strict request schemas at the gateway with automated parameter binding in the ORM creates a defense-in-depth framework that prevents malformed data payloads from reaching persistent storage.
Standardizing external API definitions allows development teams to enforce strict type checking and input constraints across all application endpoints. By decoupling API interface contracts from specific programming languages, organizations maintain consistent validation rules across multi-service environments.
This structural consistency ensures that data inputs passed into ORM query builders conform to expected data types, further reducing edge-case vulnerabilities. Leading web interface standards emphasize the importance of language-agnostic API contract definitions across modern application stacks:
“The OpenAPI Specification defines a standard, programming language-agnostic interface description for HTTP APIs.” – OpenAPI Specification
How Do ORM Parameter Binding Mechanisms Isolate Untrusted Inputs?
Implementing Parameterized Queries ORM Framework relies on driver-level parameter binding to isolate untrusted user input from core database execution logic. When an application executes an ORM method, the underlying query builder constructs a parameterized SQL template with positional or named placeholders.
To understand how database drivers separate execution trees from variable parameter streams, explore our detailed breakdown on how parameterized queries prevent sql injection across enterprise backend systems. Transmitting query structures and variable values over distinct binary protocol streams guarantees that the database engine treats incoming inputs strictly as literal values.
Because the SQL template is compiled prior to parameter substitution, unexpected control characters or SQL keywords embedded in user payloads are rendered harmless. This structural boundary eliminates the risk of payload execution regardless of input complexity.
Automating this process through ORM libraries reduces developer workload and prevents security oversights during fast-paced software development cycles. Software engineering teams can enforce uniform database security rules without manually writing custom parameter binding logic for every unique endpoint.
- ORM query builders convert object parameters into bound database placeholders automatically.
- Binary transmission protocols isolate executable command syntax from untrusted variable streams.
- Pre-compiled query templates prevent malicious string inputs from modifying database execution logic.
How Does Controller Validation Prevent Malformed Data In ORM Mappings?
Credits: Pretty Printed
Implementing Parameterized Queries ORM Framework provides robust SQL protection at the data access tier, but enterprise applications must intercept invalid payloads before they reach persistence layers. Modern application frameworks validate incoming request bodies at the controller boundary, ensuring that malformed inputs are rejected prior to ORM entity binding.
Combining automated DTO validation with ORM parameter mapping builds a multi-layered defense that keeps invalid or malicious payloads out of backend data pipelines. Validating input structures at the controller entry point prevents unverified fields from triggering unexpected database mapping exceptions or resource-heavy transaction processing.
When an incoming JSON payload violates defined schema rules, the web framework intercepts the request and terminates execution immediately. This early rejection pattern reduces processing overhead and prevents invalid parameter values from reaching downstream ORM query builders.
Leading Java web framework specifications explicitly define how automated controller validation handles schema violations before executing business logic:
“By default, validation errors cause a MethodArgumentNotValidException, which is turned into a 400 (BAD_REQUEST) response.” – Spring MVC Request Body Validation Documentation
Can ORMs Optimize Query Performance?
Implementing Parameterized Queries ORM Framework enables database engines to optimize query execution by reusing cached statement handles across repetitive transactions. When ORMs construct parameterized queries, database parsers compile the template once and execute it multiple times with varying parameter inputs.
This process eliminates redundant statement parsing, minimizes database memory fragmentation, and stabilizes throughput during peak system traffic.
- Pre-compiled ORM templates allow database parsers to reuse cached execution plans automatically.
- Binding literal parameters to pre-compiled handles cuts CPU utilization across high-traffic API workloads.
How Do Enterprise Frameworks Automate Parameter Binding Across Languages?
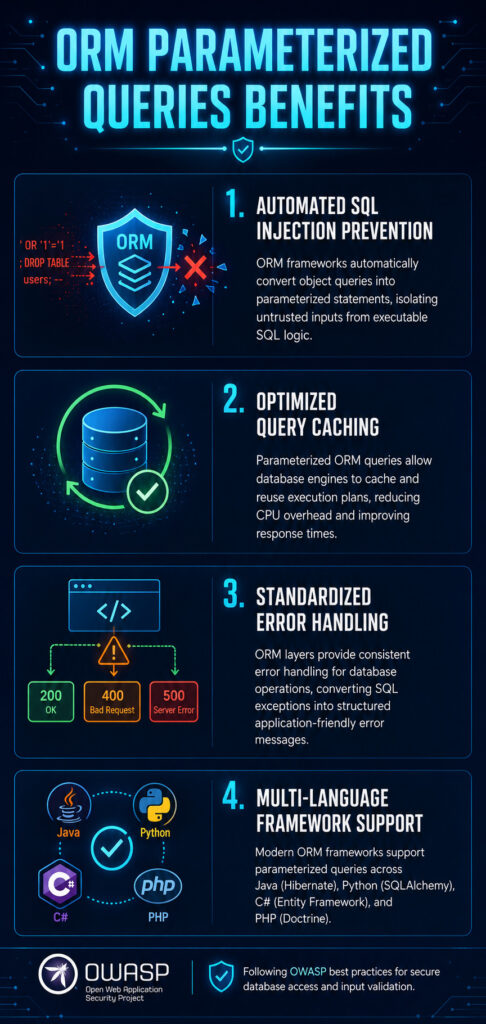
Implementing Parameterized Queries ORM Framework standardizes data protection mechanisms across diverse programming environments, including Java, C#, Python, and PHP. Modern ORM solutions abstract lower-level driver interfaces, ensuring that every database transaction automatically utilizes prepared statements instead of dynamic SQL strings.
For a step-by-step technical guide on setting up parameterized prepared statements in modern web stacks, refer to our tutorial on using prepared statements java php in enterprise environments. By integrating ORM abstraction layers into enterprise application architectures, engineering teams ensure that raw user inputs never interact directly with database command parsers.
The ORM framework binds variable parameters to pre-compiled statement handles at runtime, maintaining an unbreakable boundary between executable code and untrusted data streams. This uniform implementation reduces technical debt, minimizes configuration overhead, and guarantees consistent database security controls across microservices.
Establishing automated ORM parameterization policies ensures long-term backend security and maximum performance stability across growing development teams.
- Enterprise ORM frameworks replace manual SQL construction with standardized, driver-level parameter binding.
- Pre-compiled statement handles eliminate character encoding bypasses and injection vulnerabilities across multi-language runtimes.
- Automated parameterization streamlines code maintenance and enforces compliance standards across distributed enterprise architectures.
FAQ
What is the primary benefit of Implementing Parameterized Queries ORM Framework?
The main advantage is automated SQL injection prevention combined with optimized database execution. ORM frameworks separate SQL command structures from untrusted variable inputs, ensuring that user data is evaluated strictly as literal values while enabling database servers to reuse cached query execution plans.
Does using an ORM completely eliminate SQL injection risks?
While ORM frameworks parameterize standard model methods automatically, vulnerabilities can still occur if developers execute raw SQL queries or concatenate strings inside native query methods. Engineering teams must avoid manual string formatting within ORM raw query functions to maintain complete parameter isolation.
How does ORM parameter binding improve database server performance?
Parameterized ORM queries allow database parsers to compile SQL templates once and reuse the compiled execution paths for subsequent requests. This reduces server CPU consumption, decreases memory fragmentation, and accelerates response times across high-concurrency API endpoints.
Do all modern ORM frameworks support parameter binding by default?
Yes, leading ORM frameworks such as Hibernate, Entity Framework, SQLAlchemy, and Prisma enforce parameter binding by default across standard data access operations. They convert object-level queries into parameterized statements before sending data packets over the network to the database driver.
Should controller input validation still be used if an ORM is implemented?
Yes, controller-level validation is essential for defense-in-depth architecture. Validating request payloads at the API entry point rejects malformed or invalid inputs early, preventing unnecessary transaction processing and reducing load on the underlying ORM and database layers.
Securing Data Access Layers With Automated ORM Parameterization
Implementing Parameterized Queries ORM Framework is essential for building secure, scalable backend systems. Dynamic query concatenation invites critical SQL injection vulnerabilities while placing unnecessary compilation loads on primary database engines.
Modern ORMs resolve these architectural challenges by separating structural SQL logic from variable user data, guaranteeing that untrusted inputs are evaluated solely as inert parameters. This structural isolation neutralizes injection attacks while drastically reducing server CPU overhead through cached query plan reuse.
Software development teams must enforce mandatory ORM parameter binding across all application services. To master enterprise-grade database protection and modern backend security, join our secure coding bootcamp today.
References
- https://spec.openapis.org/oas/
- https://docs.spring.io/spring-framework/reference/web/webmvc/mvc-controller/ann-methods/requestbody.html
