Prevent AI attacks with trusted open source
Eliminate malware and vulnerability risk across your containers, dependencies, CI/CD actions, and AI agent skills so your developers can just ship.
The services the world relies on run on Chainguard

 4.7 Stars on G2


 Case study


 Case study

 Case study


 Case study





 Case study

 Case study
Protect your open source infrastructure. Stop firefighting vulnerabilities and malware, and build a resilient supply chain with Chainguard.
There are 242 new CVEs published every day, up 80%+ from 2025.
Chainguard lets you step off the CVE remediation treadmill to focus on building
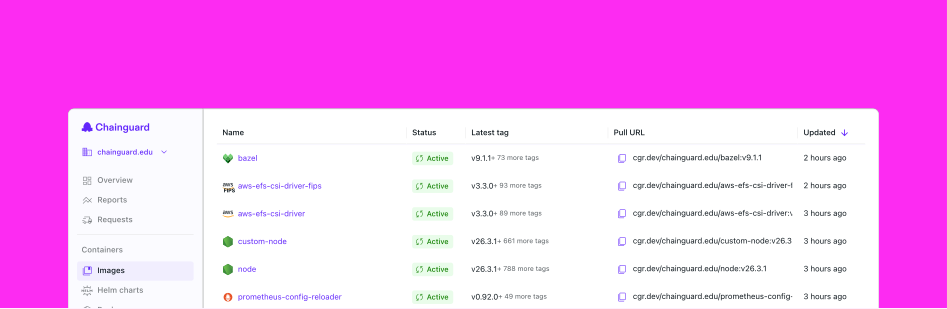
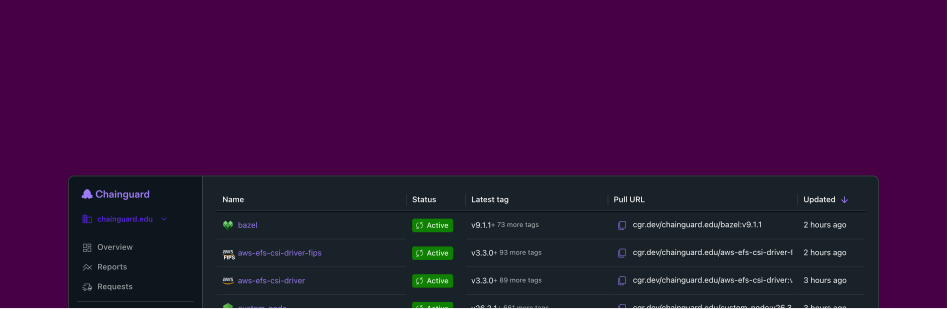
3,000+ images with 97.6% fewer CVEs than public alternatives
Secure every application with container images that are rebuilt from source daily and sport best-in-class SLAs.
CVE backports for hard-to-upgrade Python and Java library versions
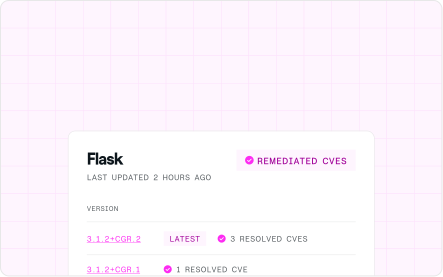
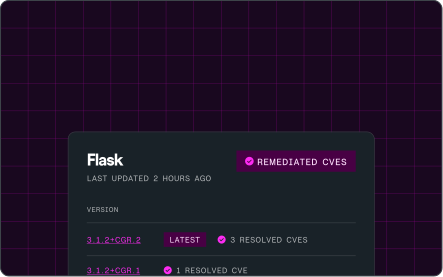
Remediations that quiet your scanners

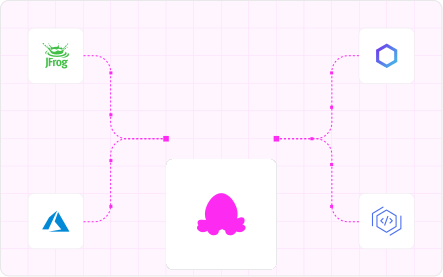
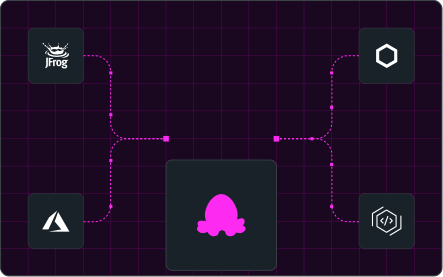
Compatible with your artifact manager

Shift5
Shift5 saved 2.5 months of engineering time per person on CVE remediation.
A new piece of malware is published every minute.
Chainguard keeps your credentials out of attackers’ hands without any incident response
Malware-free dependencies
Access a trusted catalog of Python, JavaScript, and Java packages so you can turn off live access to public registries.
Multiple layers of defense that stop hundreds of daily supply chain attacks
Packages are detonated in a sandbox to identify suspicious behavior


Canva
Canva dodged hundreds of thousands of malware attacks on npm and PyPI.
Frontier AI models are uncovering thousands of zero-days.
Chainguard shrinks your attack surface to keep rogue agents out of your environment

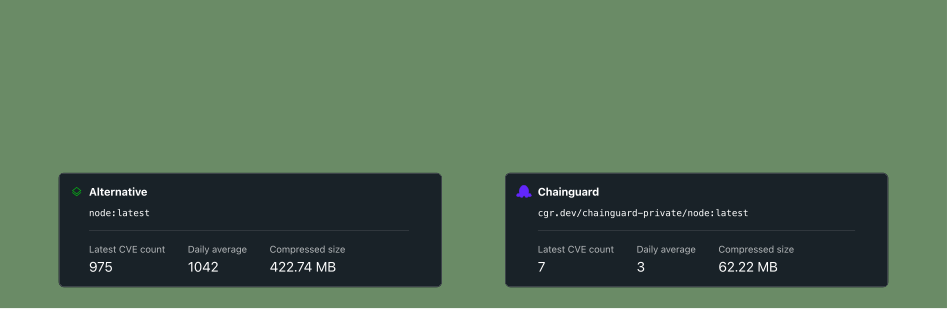
Smaller images means fewer attack paths
Chainguard Containers, on average, are 10% smaller than what you’d find on public registries, limiting the novel attack paths rogue agents can use to get into your environment.


Designed to fit securely within the rest of your stack
Chainguard hardens your open source before your developers start writing a single line of code. Our artifacts replace vulnerable or malicious versions you may find publicly, all before you scan your environment.
- Access Control
- Secrets Management
- Posture Management
- Runtime defense
- Detection & Triage
- Incident response
Switch to trusted open source with zero developer friction
Get your apps up and running with 200+ Helm charts

Use Guardener, Chainguard’s agent, to speed up adoption

Pull any artifact via CLI — or tell your agent to do it

Works with what already works
Integrate with your registries, cloud, CI/CD, and developer tools so trusted open source fits into existing workflows without adding friction or changing how your teams work.
 Cursor
 Google
 Azure
 Bytes
 Microsoft
 AWS
 Google Cloud
 Sysdig
 Upwind
 Wiz
 TigerData
 JFrog
 Ngnix
 Orca Security
 Second Front
 VulnCheck
 Crowdstrike
 Anchore
- Cursor
- Google
- Azure
- Bytes
- Microsoft
- AWS
- Google Cloud
- Sysdig
- Upwind
- Wiz
- TigerData
- JFrog
- Ngnix
- Orca Security
- Second Front
- VulnCheck
- Crowdstrike
- Anchore
Army Software Factory
Read their storyThe Army Software Factory freed up 40% of developer time for mission-enabling innovation.
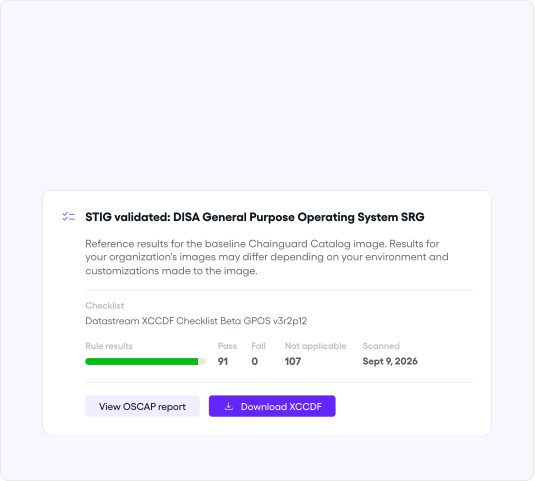
Enforce your organization’s compliance standards
Govern what open source your developers and agents can use while proving to auditors your third-party components hold ironclad integrity.
Set policies to block artifact consumption outside your org
Read Chainguard Repository documentationAccess provenance and SBOMs for Chainguard-built artifacts
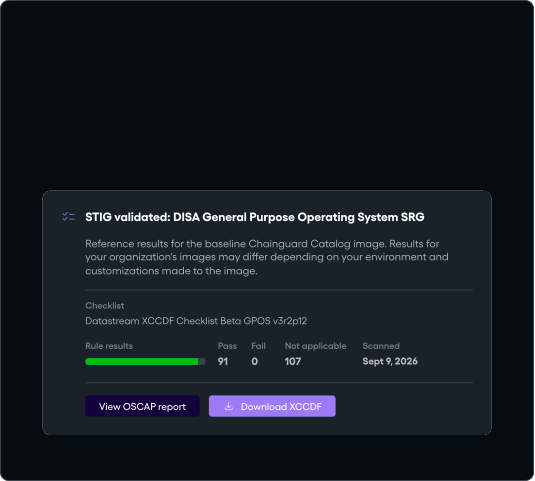
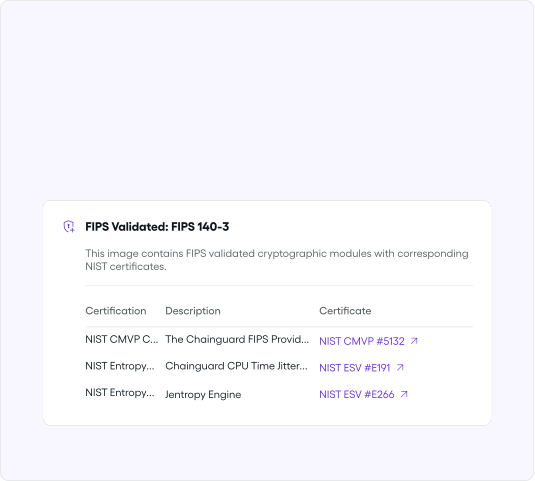
Read SLSA L3 documentationMeet FedRAMP requirements with FIPS images
Browse FIPS catalog


Learn more about trusted open source


The hardest fork
BlogBuild safely with AI: Securing your agentic engineering
CourseWhen AI builds faster than you can secure it: Tech Talks hosted by Chainguard
Webinar5 habits to operationalize AI in the SDLC for engineering leaders
GuideThis Shit is Hard: How AI keeps our code on standard
BlogAssemble 2026: Relive Chainguard’s event for engineering and security leaders
EventThis Shit is Hard: Inside the Chainguard Factory
Blog