Act controls access adaptively as your cloud changes,
as your organization evolves and as AI adoption grows.
Free your team from the endless remediation loop
Your backlog is growing faster than your team can clear it. When AI-driven attacks outpace vulnerability detection, simply patching faster is no longer a winning strategy.
It’s time to stop pushing the boulder up the hill and eliminate risk right at the source.
Act eliminates the
conditions that turn
risk into a breach
Scale AI adoption without sacrificing control.
Deploy AI production agents safely by enforcing tightly defined access boundaries around every AI workload, so agents only reach what they need.
Remove attack paths before
they can be exploited.
Achieve meaningful attack surface reduction by removing unnecessary access and unintended reachability into, through, and out of your cloud.
Keep security teams effective.
Eliminate access sprawl at the source and prevent it from returning by continuously validating violations before they reach production.
Achieve provable,
continuous compliance.
Enforce the access and data boundaries required by NIST 800-53, PCI DSS, HIPAA, and more.
Control in Action
Map your cloud boundaries
Map every cloud construct into boundaries that reflect how your business actually operates - by organization, environment, application, or data.
Model your reachability
Understand how access flows across your cloud by cross-analyzing identity, network, and AI access to reveal the gap between what is configured, what is used, and what should be allowed.
Run hardening campaigns
Use guided, structured campaigns to eliminate thousands of access paths and protect your crown jewels with a single policy change.
Simulate the change, enforce it safely
Simulate each policy change first to validate its impact before it reaches production, then apply it through your own cloud-native controls.
Sustain over time, with ease
Seamlessly manage exceptions and violations right in your own tools, with data-driven proof attached, so confidence holds without the manual overhead.
Watch Act in 3 Minutes
Join our founders for a quick look at why traditional security fails in the AI era - and how Act makes your cloud structurally secure before attacks unfold.
Why Act
See Act in their words
"Act is a great product because it breaks the cycle of recessive problems in the most fundamental areas and creates actual prevention and secure practices that enforce least privilege in the cloud.”
“With Act, we're able to add various controls that permanently eliminate attack paths and create a resilient form of security by constraining attacker optionality.”
“Traditional tools are great at finding risk and telling me about it. Now, the risk landscape is changing and forcing us to go back to the fundamentals and eliminate the root cause of the problem: the over-granting of access.”
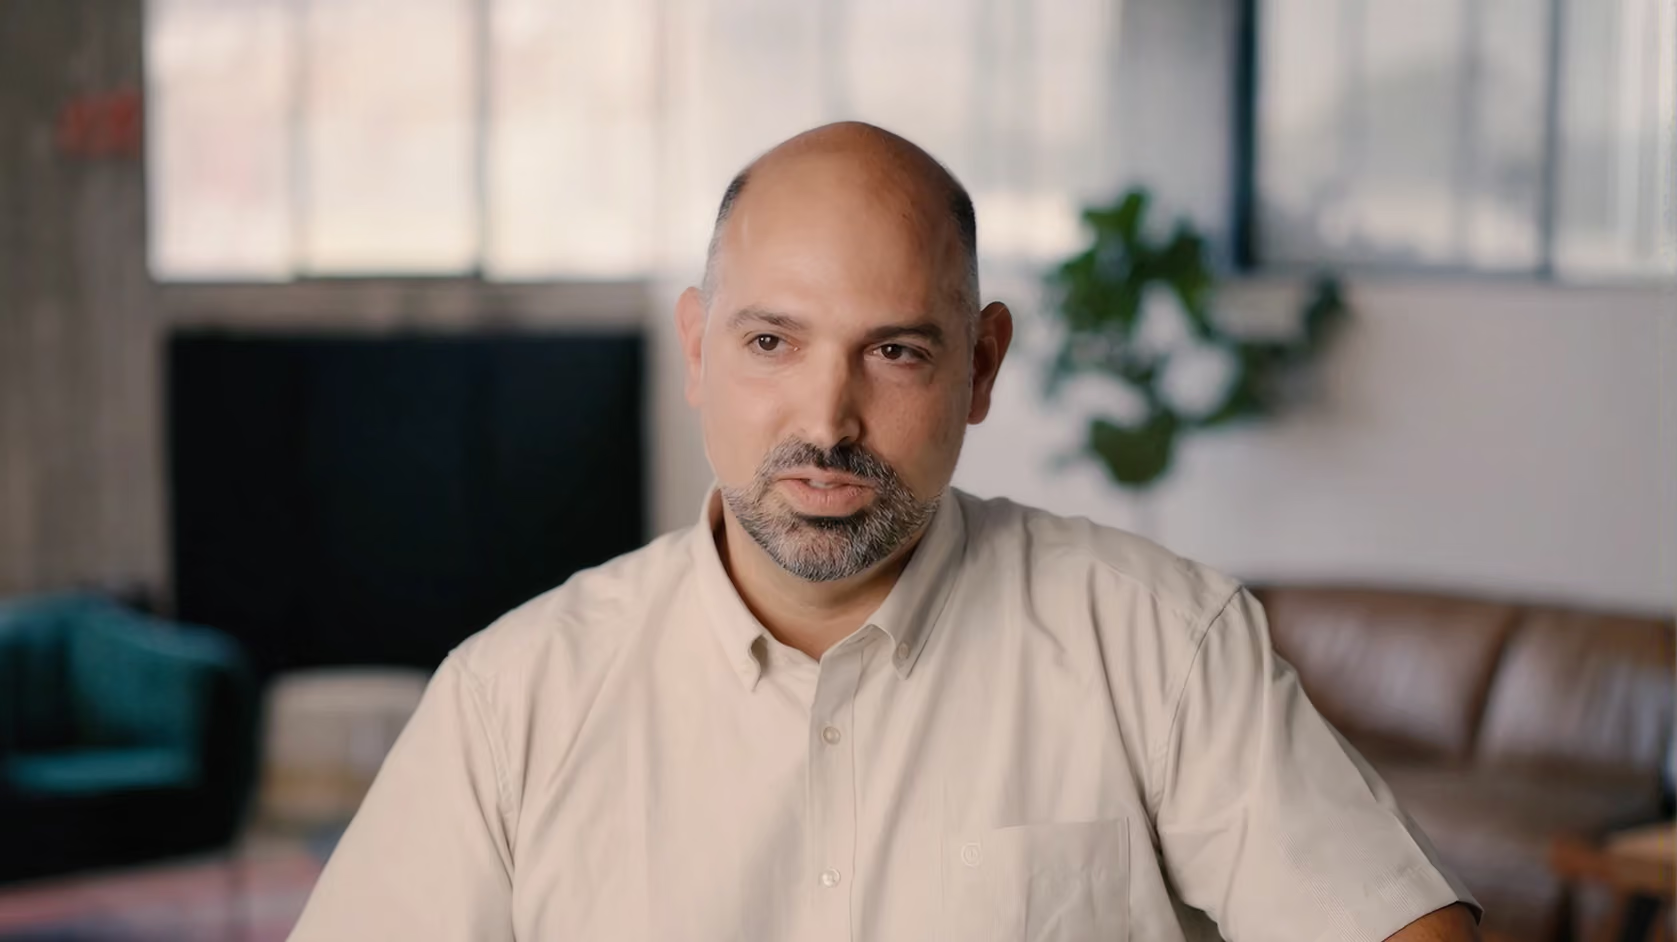
“Since I brought Act in, I can have real peace of mind from the remediation game. That’s the biggest change. I know my architecture is safe with Act.”
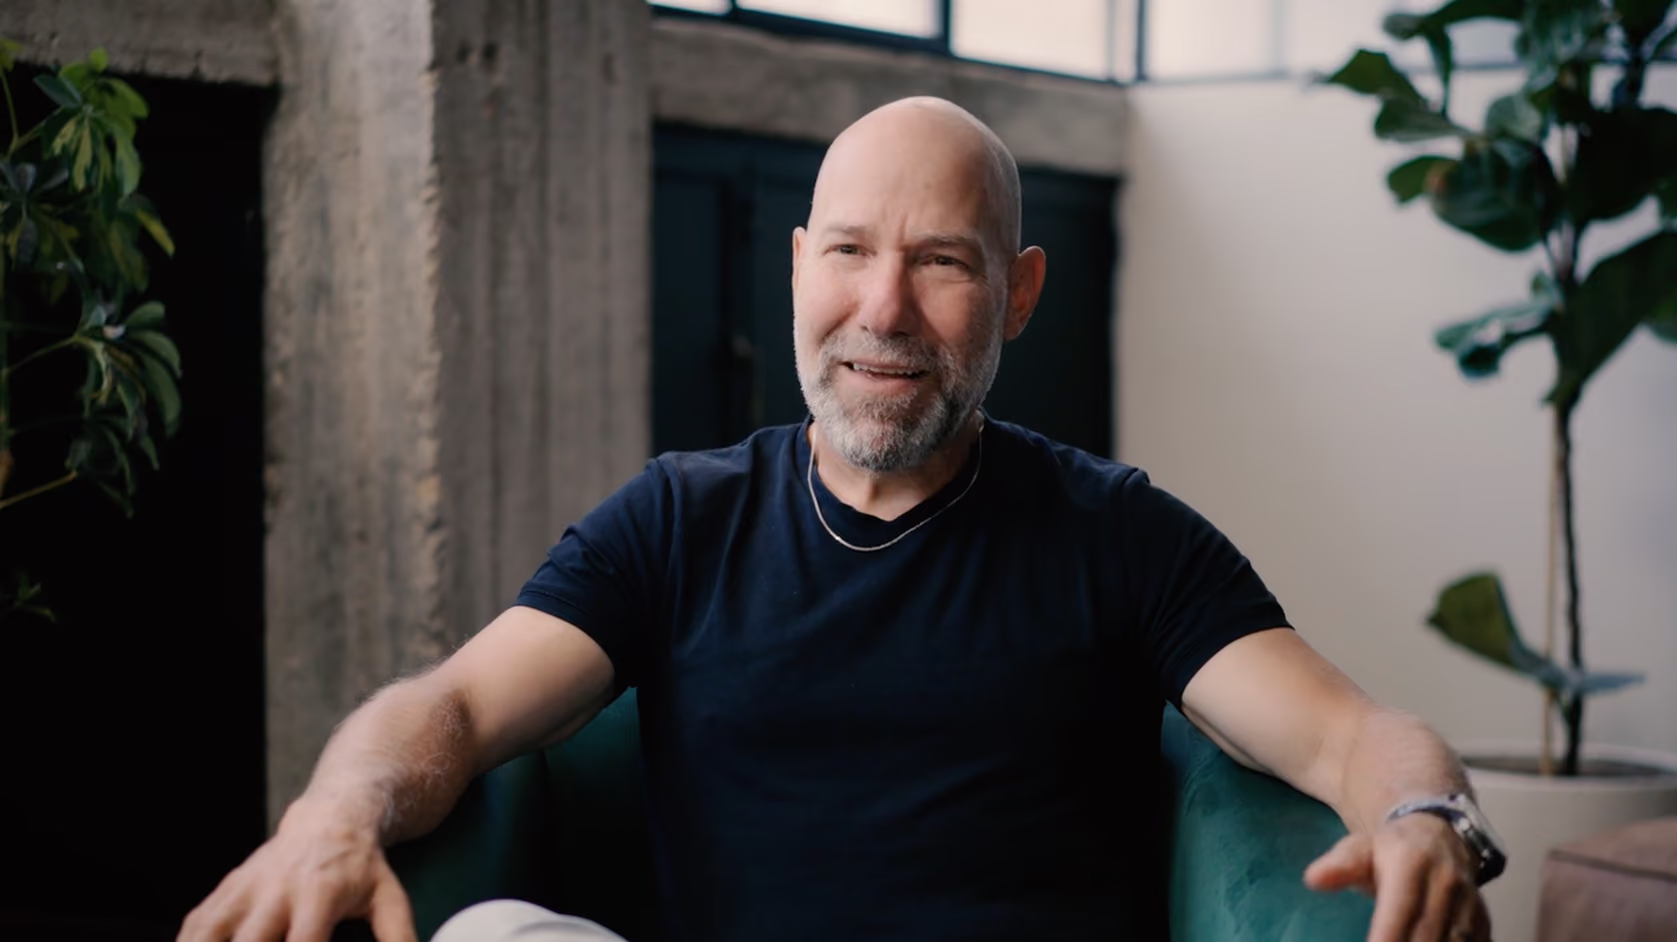
“Act’s proactive approach immediately caught my attention. As I went deeper into the technology, I saw a fresh approach that delivers real value to me as an enterprise CISO.”
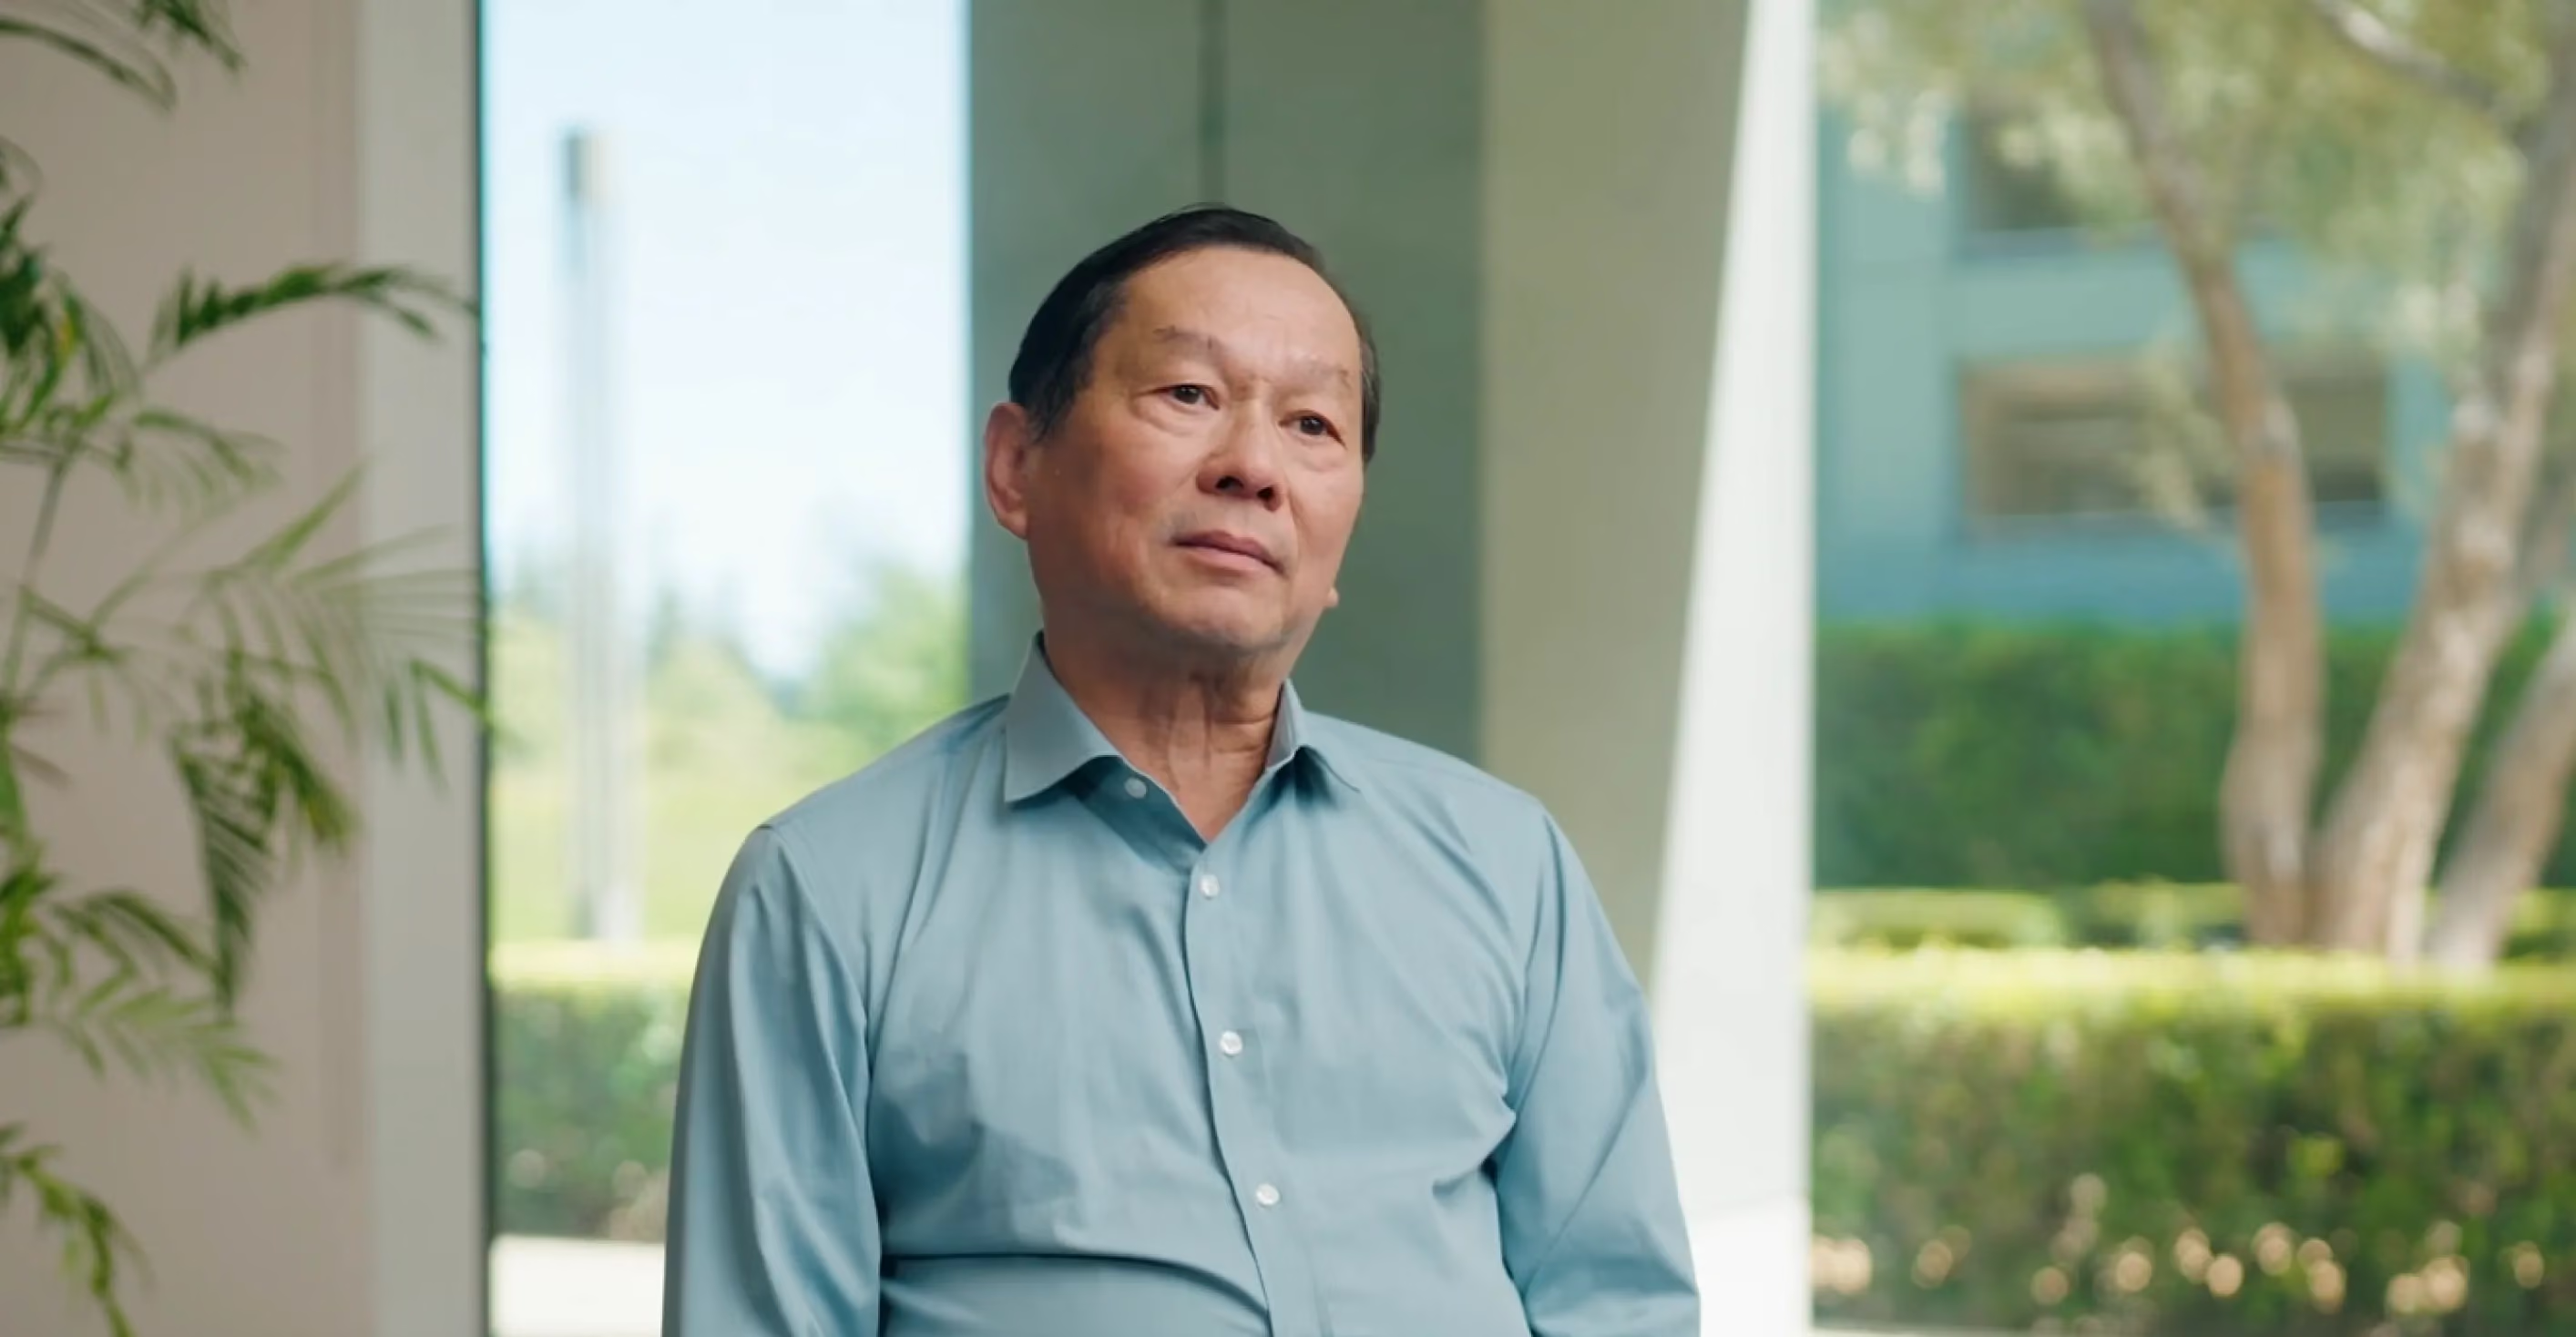
“If you want to be able to sleep at night and you want something that's simple to operate, talk to Act.”
More from those who Act
“Since I brought Act in, I can have real peace of mind from the remediation game. That’s the biggest change. I know my architecture is safe with Act.”

"To manage security at scale, you need a system that understands your context, maps relationships, and stops risk in its tracks. That's exactly what Act does: eliminating risk at the foundation so it never reaches you at runtime.”

“With Act, we're able to add various controls that permanently eliminate attack paths and create a resilient form of security by constraining attacker optionality.”
"Act is a great product because it breaks the cycle of recessive problems in the most fundamental areas and creates actual prevention and secure practices that enforce least privilege in the cloud.”

“Traditional tools are great at finding risk and telling me about it. Now, the risk landscape is changing and forcing us to go back to the fundamentals and eliminate the root cause of the problem: the over-granting of access.”
“An AI agent with excessive permissions isn't a hypothetical risk, it's a live one the moment you deploy it. Act scopes what agents can do down to what they should do.”

“CISOs have chased least privilege in the cloud for years, and it’s always been a mess nobody knew how to untangle. Act is the first solution that looks like it’s cracked the code.”
“You can’t secure the agent from inside the agent. You have to secure it at the infrastructure and access layer, which is exactly where Act operates.”

“Act’s proactive approach immediately caught my attention. As I went deeper into the technology, I saw a fresh approach that delivers real value to me as an enterprise CISO.”

"Organizations have always wanted least privilege. The challenge has never been intent, it's been knowing which permissions are actually needed and what can safely be removed. Act helps turn that uncertainty into actionable decisions.”

“If you want to be able to sleep at night and you want something that's simple to operate, talk to Act.”

PHP2Shell: exploitability changed overnight. Blast radius didn't have to.
Ten years of nothing, then two days with AI, and a quiet PHP bug became a way into your cloud. PHP2Shell is a pair of critical CVEs in core PHP that let an unauthenticated attacker run code on an exposed server or read credentials straight out of memory. The attacker lands as the PHP worker, with every cloud role and secret it holds. You can’t patch every runtime overnight, but you can remove the access an attacker would use in the first place.