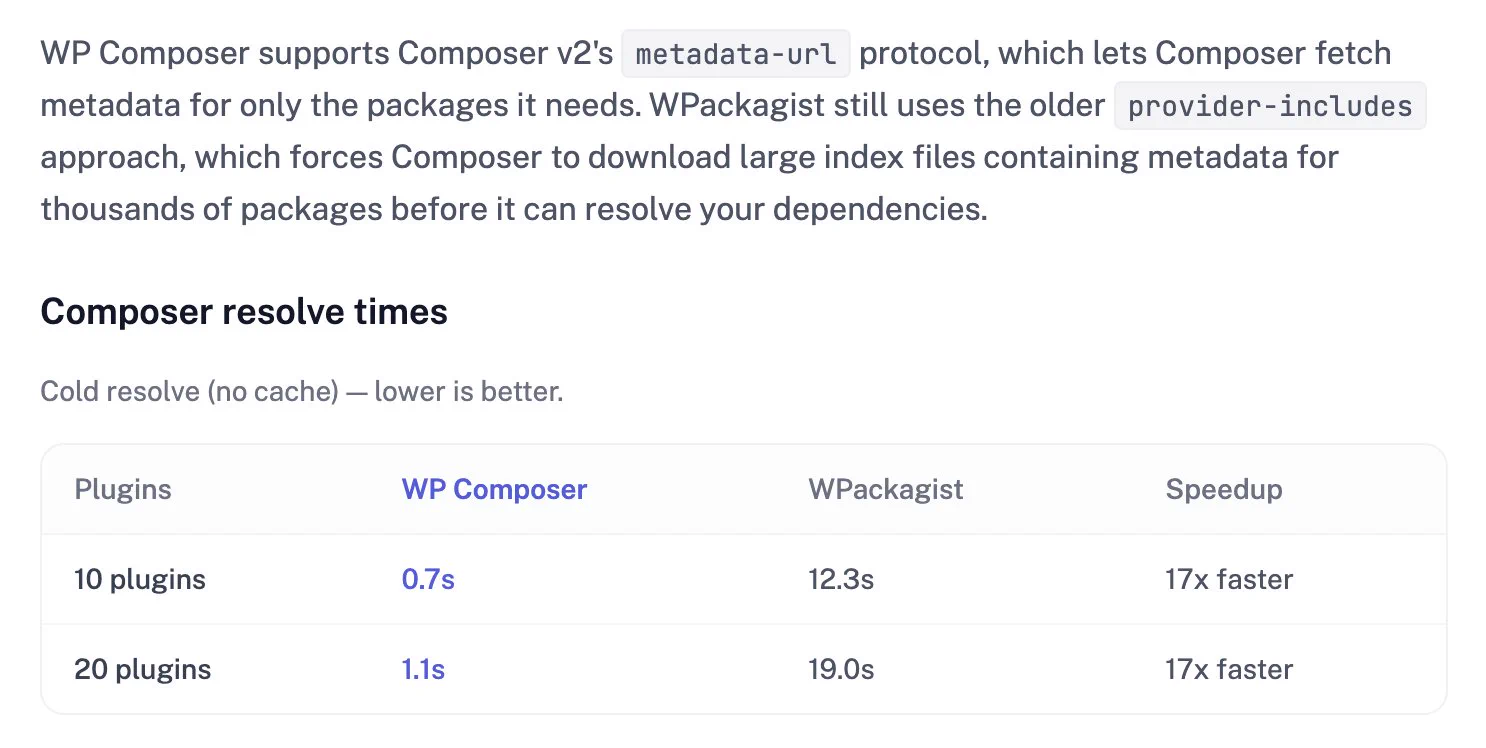
✨ We built WP Composer — an independent, open source Composer repository for WordPress plugins and themes, with 17x faster cold resolves than WPackagist
wp-composer.com
Cooldown now works for WordPress plugins and themes too! WP Packages records when it first serves each version, and resets the clock if a release is changed after the fact on WordPress.org
roots.io/wp-packages-no…
PHP now recommends keeping session upload progress disabled until the next PHP release (CVE-2026-115560):
Trellis v1.32.2 makes this the default
roots.io/php2shell-patc…
PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 are out with fixes for two critical RCE vulnerabilities.
Trellis v1.32.1 switches PHP to packages.sury.org, which had the patched builds first. Here's how to upgrade, or apply just the PHP change:
discourse.roots.io/t/upgrading-ph…
PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 are out with fixes for two critical RCE vulnerabilities.
Trellis v1.32.1 switches PHP to packages.sury.org, which had the patched builds first. Here's how to upgrade, or apply just the PHP change:
discourse.roots.io/t/upgrading-ph…
An unofficial stopgap is going around:
Set session.upload_progress.enabled = Off until you can upgrade
PHP hasn't confirmed it helps, but WordPress and Laravel don't use the feature
Trellis steps are in the thread along with Cloudflare rules
discourse.roots.io/t/upgrading-ph…
PHP is shipping a security release tomorrow (Oct 21, 14:00 UTC) for two critical vulnerabilities
Re-provisioning Trellis won't upgrade PHP on its own. Here's how to upgrade once the PPA build is out:
discourse.roots.io/t/upgrading-ph…
PHP's announcement: php.net/archive/2026.p…