HITRUST Certification | A-LIGN
  • Services
        • SOC Assessments 

        • SOC 1
        • SOC 2
        • ISO Certifications 

        • ISO 27001
        • ISO 27701
        • ISO 22301
        • ISO 42001
        • ISO 45001 
        • ISO 14001
        • ISO 9001
        • Federal Assessments 

        • All Government
        • FedRAMP
        • GovRAMP
        • FISMA
        • CMMC
        • NIST 800-171
        • Healthcare Assessments 

        • All Healthcare
        • HITRUST
        • HIPAA
        • Cybersecurity 

        • Penetration testing
        • Red team services
        • Ransomware preparedness assessment
        • Social engineering
        • Vulnerability assessment service
        • Privacy 

        • GDPR
        • CCPA/CPRA
        • PCI Assessments 

        • PCI DSS
        • PCI SSF
        • Additional Services 

        • International Services
        • Multi-Framework
        • AI Governance
        • AIUC-1
        • AS9100
        • Microsoft SSPA
        • NIS2
        • C5
        • SOX 404
        • CSA STAR
        • Business Continuity & Disaster Recovery
        • Limited Access Death Master File
        • All Services
  • Platform
  • Company
        • About Us
        • Partners
        • Meet our team
        • Board of Directors
        • Careers
        • Community
        • image

          Veteran-owned elite cybersecurity team expands A-LIGN’s ability to help organizations move beyond compliance and stay…

          Learn more
  • Customers
  • Resources
        • Quick links

        • Resource Center
        • Blogs
        • Case Studies 
        • Videos
        • Events
        • By service

        • SOC 2 
        • ISO 27001 
        • ISO 42001 
        • CMMC
        • FedRAMP
        • HITRUST 
        • PenTest
        • Featured Resources

          image
          image
          image
          image
  • A-SCEND Login
  • Careers
Image Image
CONTACT US
Image

HITRUST assessment by A-LIGN

Get to HITRUST certification faster 

A-LIGN is a HITRUST-authorized External Assessor Organization that has completed more than 1,400 HITRUST assessments. A-LIGN combines deep assessor expertise and a purpose-built audit platform to make HITRUST certification achievable.

Talk to an expert
Image
HITRUST certification rate

100%

HITRUST assessments completed

1.4k+

HITRUST clients certified

300+

client satisfaction rating

96%

WHy A-lign

Simplify your path to achieving HITRUST

Getting to HITRUST certification shouldn't mean choosing between speed and quality. A-LIGN pairs expert assessors and a rigorous methodology with audit management technology, so the process is easier and more efficient while maintaining the rigor HITRUST demands. 

Get started
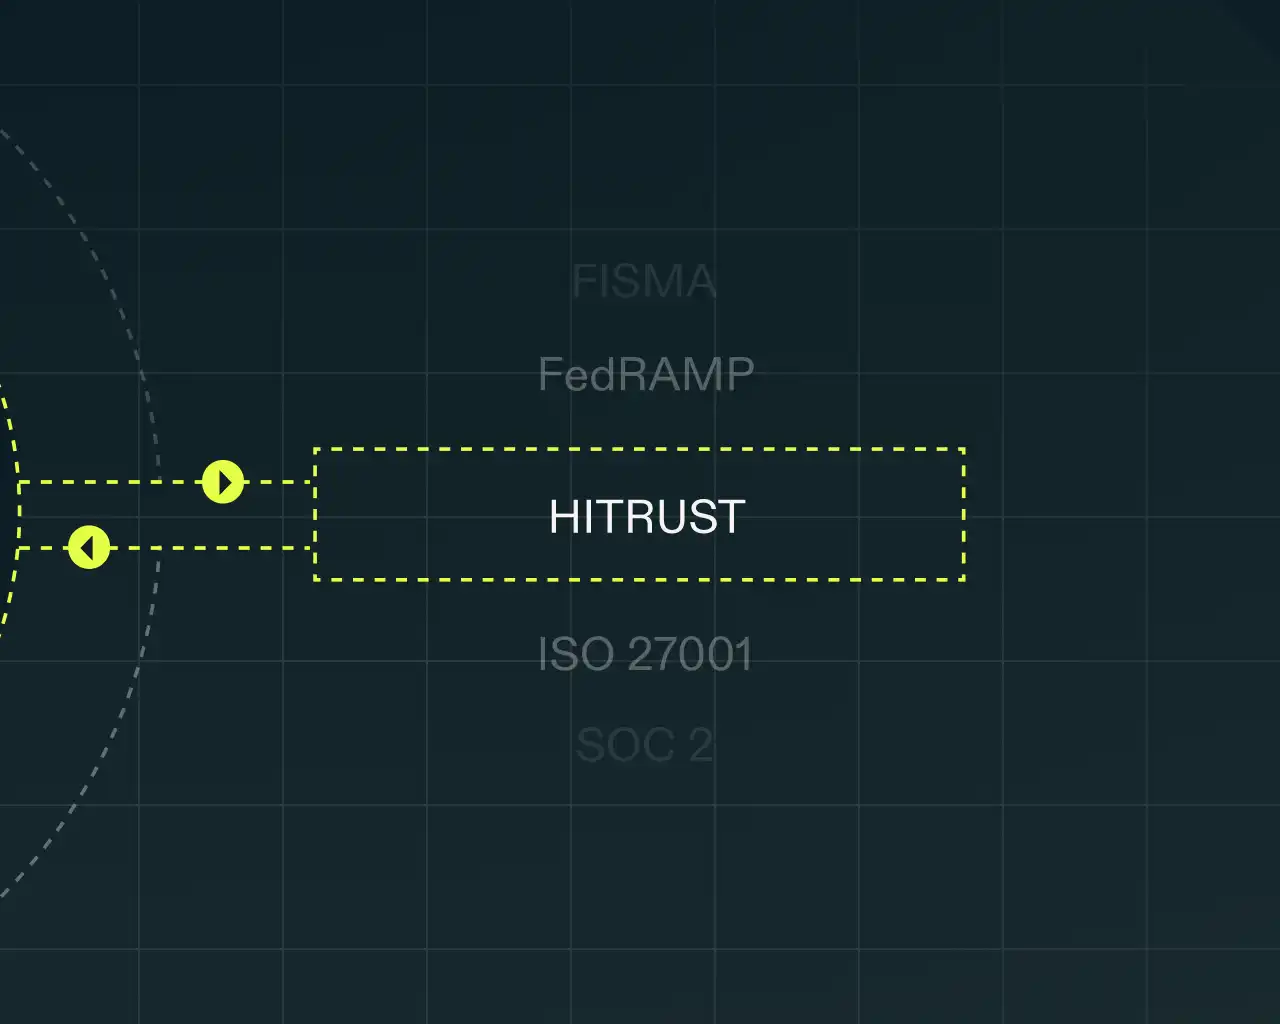
Illustration of A-SCEND mapping shared audit evidence across SOC 2, SOC 1, ISO 27001, and HITRUST

A faster path to HITRUST, powered by API integration

A-LIGN is one of the first assessors to bundle MyCSF, audit services, and a final report in a single engagement, powered by A-SCEND, our audit management platform. By enabling real-time data exchange with the HITRUST platform, it delivers faster assessment timelines, fewer errors, less back-and-forth, and one partner from kickoff to certification.

Tech-enabled, strategic audit harmonization

HITRUST shares significant overlap with other common frameworks like SOC 2 and ISO 27001. A-LIGN's A-SCEND platform allows clients to manage evidence, communications, and audits from one central location, reducing overall audit fatigue and demonstrating a higher level of security maturity.

Accelerate revenue and demonstrate security  

HITRUST empowers organizations in highly regulated industries to build and demonstrate a mature cybersecurity and compliance strategy. As one of the top assessors in the world, we’ve transformed the HITRUST audit process to help over three hundred clients successfully achieve HITRUST certification.

OUR SERVICES

End-to-end HITRUST expertise

HITRUST is the gold standard for organizations operating in healthcare and other regulated industries, helping organizations systematically manage risk, protect sensitive data, and meet regulatory requirements.

Contact us

Readiness Assessment

Examines the organization’s environment and flow of data between systems that are in-scope, identifies gaps for control, and provides recommendations for remediation.

e1 Assessment

The cybersecurity essentials assessment with 44 control requirements, meant for low-risk organizations that want to ensure they are maintaining good cybersecurity hygiene.

i1 Assessment

Suitable for moderate assurance and results in a 1-year certification if requirements are met. There are 219 static controls in an i1 Assessment and only the implemented maturity is tested.

r2 Assessment

A comprehensive risk-based specification of controls with a rigorous approach to evaluation, suitable for high assurance requirements. This certification is issued for two years with an Interim Assessment.

Interim Assessment Testing

Tests a subset of requirements and controls from the prior r2 and determines the progress of any Corrective Action Plans, ensuring ongoing effectiveness.

HITRUST AI Cybersecurity & Risk Management Assessments

Assessments to help organizations manage AI-related cybersecurity risks and establish responsible AI governance.

A-LIGN by the numbers

audits completed
36k+
customer satisfaction
96%
clients globally
6.4k+
auditors globally
400+
Platform Innovation

Modernized compliance makes rigor repeatable

A-SCEND combines human expertise and robust processes with powerful technology to help you achieve compliance, grow your business, and expand into new markets without sacrificing rigor.

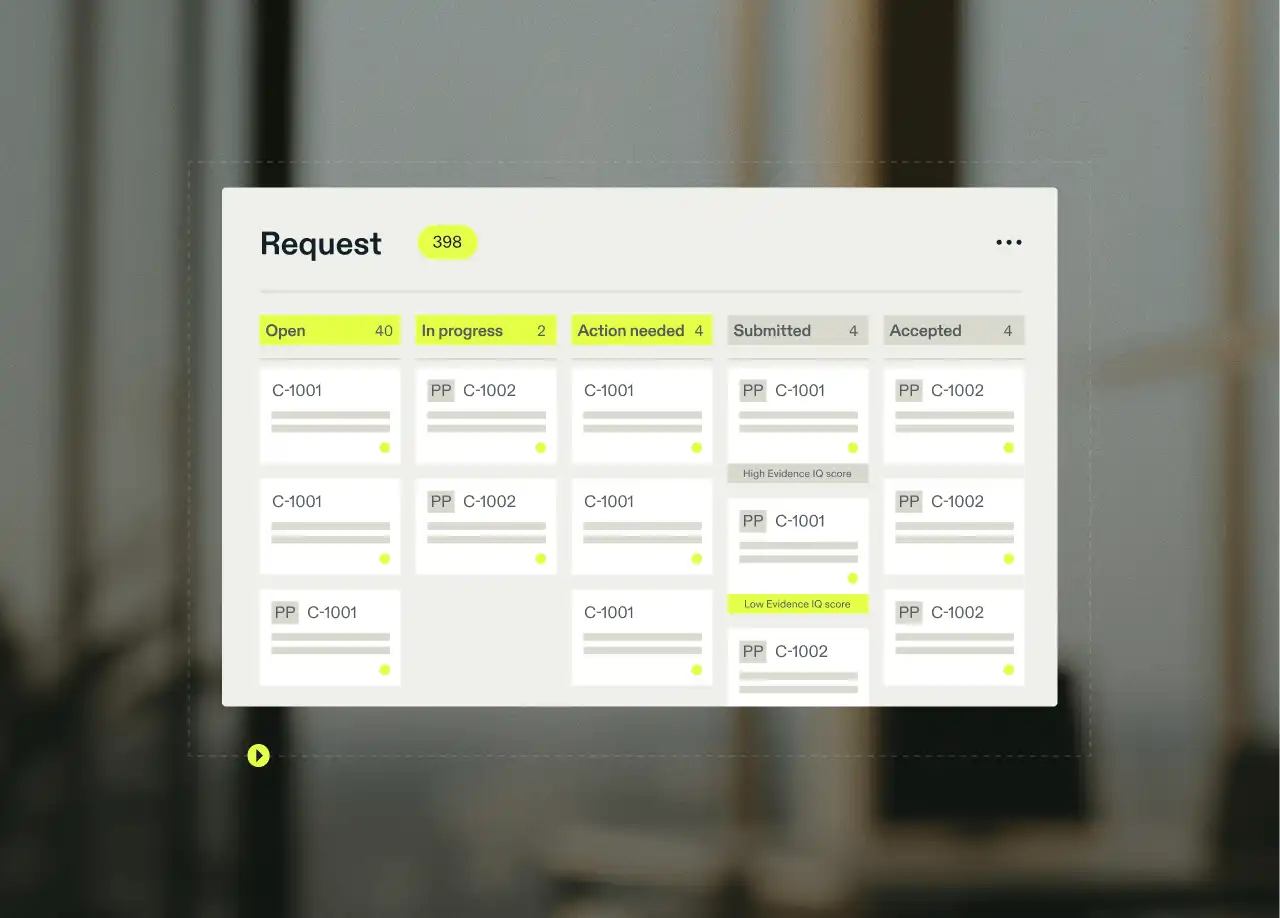
A-SCEND platform showing centralized audit requests
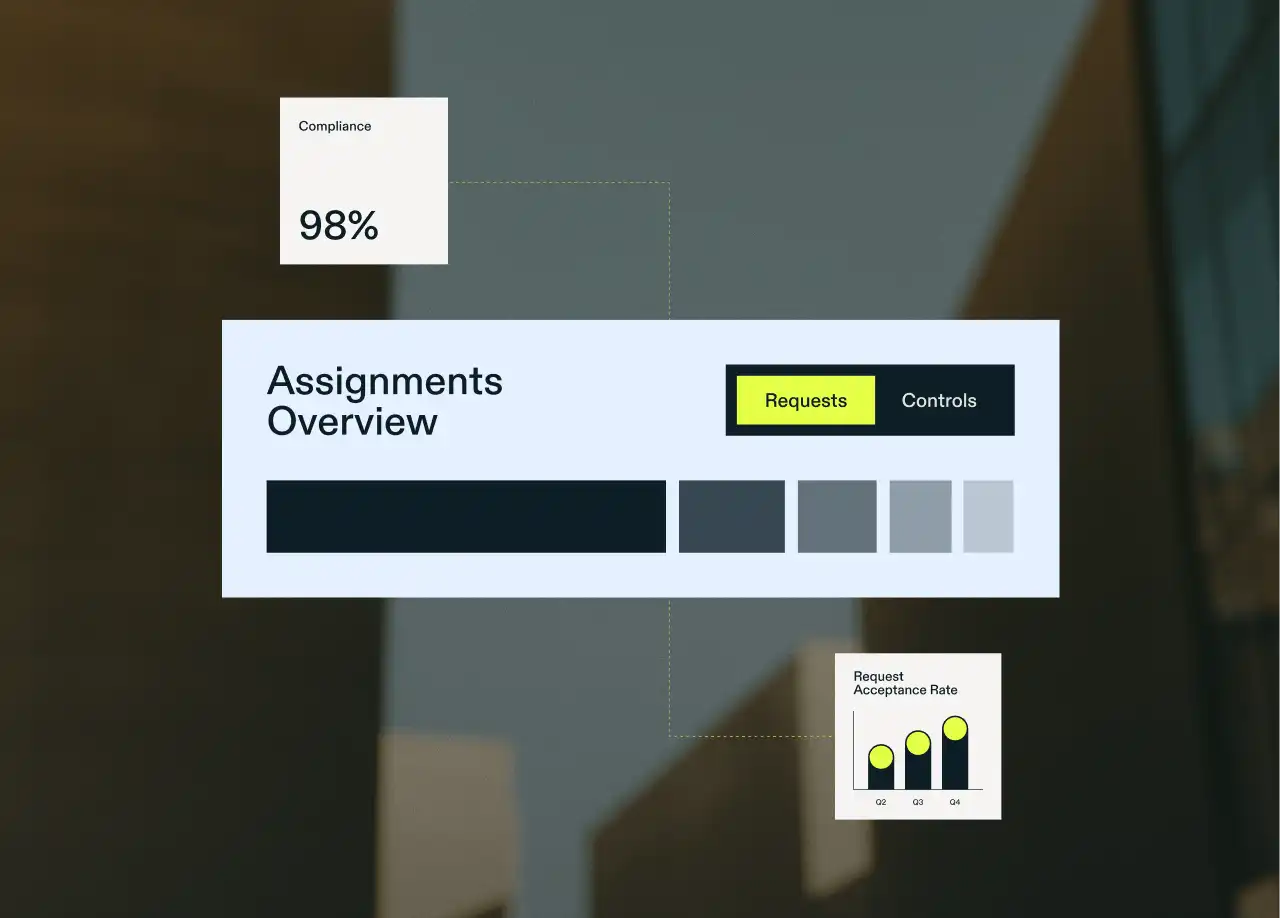
A-SCEND platform showing the guided audit workflow stages
EFFICIENT AUDIT PLATFORM

Tech-enabled audit management

A-LIGN is one of the first assessors to bundle MyCSF, audit services, and the final report in a single engagement. Behind it is A-SCEND, our audit management platform, with a unique API integration that exchanges data with the HITRUST platform in real time – no manual re-entry, fewer errors, less back-and-forth. Built from real-world audit practice, A-SCEND eliminates repetitive tasks, delivers real-time visibility, and enforces precision across every engagement – faster timelines and one partner from kickoff to certification.

Purpose-built technology enforces consistency, strengthens audit quality, and drives efficiency, every cycle, every framework, every year.


RIGOROUS METHODOLOGY 

Precision at every stage

Every A-SCEND engagement follows a disciplined methodology built to withstand scrutiny.

That rigor carries through every stage of our audit process, from precise scoping and a deep understanding of your business up front, with executive oversight and built-in quality checks, to expert review and fine-tuning for a polished, high-quality report.

That experience and discipline bring greater certainty and help prevent the leading causes of report rejection: incomplete scope and missing controls.

SUCCESS STORIES

Why regulated-industry leaders choose A-LIGN for HITRUST

From multi-framework harmonization to tight certification deadlines, see how organizations earned HITRUST with A-LIGN.

“A-LIGN has harmonized and consolidated our audits with a unified audit management process, aligning with frameworks like HITRUST r2 and SOC 2. This approach streamlines compliance, reduces redundant efforts, and saves time and resources, allowing for more efficient risk management and reporting across the agency.”

Director of Information Security

Rozealieth San Nicolas

Merge

Merge logo

“We work with A-LIGN due to the ease of use for multiple frameworks. Other competitors require submitting evidence for each framework, but A-LIGN's A-SCEND platform allows for the same evidence to be used for all evaluations. This is a HUGE time saver during the audit.”

Senior Network & Security Administrator

Dan Clark

MDaudit

MDaudit logo

“A-LIGN is truly interested in us and wanted us to succeed in our HITRUST Certification process. They did a demo with A-SCEND, and it was a great platform. It allowed us to link documents to controls and was super easy to get going. Our auditor team was fantastic — very friendly, knowledgeable, and always ready to help.”

Sr. Director – Information Security

Jason Patterson

Nasuni

Nasuni logo

“We needed to get HITRUST Certification in a short amount of time, and we needed a firm that would help us ramp up quickly. We were impressed with the responsiveness and competence of A-LIGN's team and contracted with the company for a multi-year engagement.” 

GRC Manager 

Heather Havens

Elixir Technologies

Elixir logo
Helpful Resources

Support for your compliance journey

From guides to whitepapers, we've got the resources to move your compliance program forward.

View resources
Image
Case study
HealthBridge Boosts Compliance Program with HITRUST Certification
Learn more
Image
Blog
HITRUST Checklist – Readiness for HITRUST Certification
Learn more
Image
Blog
The HITRUST AI Security Assessment: Explained
Learn more
Image
Blog
What is HITRUST? Complete Guide to HITRUST Certification
Learn more

Frequently asked questions

Contact us

What are the different types of HITRUST assessments?

HITRUST offers three validated assessment types. The e1 covers roughly 43 essential requirements and suits lower-risk organizations demonstrating baseline security hygiene. The i1 covers 182 threat-adaptive requirements and suits organizations needing moderate assurance, testing only “implemented” maturity rather than the full maturity model. The r2 is scoped to the organization's risk profile, industry, data volume, and regulatory footprint — most r2 assessments land somewhere between roughly 200 and 400+ requirements (commonly cited averages run around 300–385), though tailoring can push the ceiling into the thousands. The r2 is the benchmark for enterprise healthcare organizations, health plans, and health tech vendors. The e1 and i1 produce one-year certifications; the r2 produces a two-year certification with a mid-cycle Interim Assessment. A-LIGN also offers Readiness Assessments for organizations preparing for a first validated assessment, Interim Assessment Testing for r2 certificate holders, and HITRUST AI Security and Risk Management Assessments.

How long does a HITRUST certification take?

An e1 assessment typically takes 3 to 6 months from kickoff to certification. An i1 assessment generally takes 6 to 9 months. An r2 assessment, the most comprehensive, commonly takes 9 to 18 months, with a significant share of that time spent remediating controls before formal assessment begins. The primary variables are the assessment type, the maturity of the existing control environment, and the efficiency of the evidence-management process. A-LIGN offers readiness assessments to surface gaps early, and the A-SCEND platform exchanges data with MyCSF via API, which compresses the assessment phase by reducing evidence-submission delays and quality-review iterations.

How does HITRUST relate to SOC 2 and other frameworks?

HITRUST maps to dozens of frameworks beyond SOC 2, including ISO 27001, NIST 800-53, HIPAA, PCI DSS, and GDPR, consolidating them into a single certifiable control set. The key distinction is the form of assurance: SOC 2 is an attestation — an auditor's opinion against the flexible AICPA Trust Services Criteria — while HITRUST is a certification produced by scored, maturity-rated testing against prescribed requirements. Organizations already holding SOC 2 or ISO 27001 can reuse substantial existing evidence for HITRUST, and the assessments can be run concurrently. A-LIGN's A-SCEND platform lets clients manage evidence, communications, and audits for HITRUST, SOC 2, and ISO 27001 from one central location, reducing audit fatigue instead of repeating evidence collection for each framework.

Is HITRUST required for my organization?

HITRUST certification isn't mandated by any single federal regulation, but it's effectively required in several commercial contexts. Large health systems, health plans, and managed care organizations frequently list HITRUST r2 as a vendor-qualification requirement in their third-party risk programs. Organizations participating in health information exchange ecosystems often require it as a baseline trust anchor, and some federal health agency contracts specify it as an evaluation criterion. Cyber insurance underwriters in health tech and healthcare SaaS increasingly treat HITRUST certification as a risk-reduction signal affecting premium pricing. Many non-healthcare organizations also pursue HITRUST for its broad framework coverage and market recognition. If an organization handles protected health information and sells to enterprise healthcare customers, certification is likely already required by its largest accounts, or will be within the next contract cycle.

How much does a HITRUST certification cost?

Cost varies significantly based on the assessment type chosen (e1, i1, or r2), the complexity and size of the organization, and the number of in-scope systems and locations. Assessor fees are only part of the picture — the total investment also depends on the MyCSF subscription charged directly by HITRUST, any internal remediation work needed before the assessment, and the maturity of the organization's existing control environment. Organizations that already hold SOC 2 or ISO 27001 typically see lower overall costs, since much of the evidence infrastructure is already in place. Because pricing is so scope-dependent, the most reliable way to get an accurate figure is a scoping conversation with A-LIGN based on your specific environment.

What is the HITRUST CSF?

The HITRUST Common Security Framework (CSF) is a certifiable information security and privacy framework maintained by the HITRUST Alliance. It consolidates requirements from HIPAA, NIST 800-53, ISO 27001, PCI DSS, GDPR, and other authoritative sources into a single control set organized across 19 domains (grouped under 14 control categories), covering areas including access control, endpoint protection, incident management, risk management, data protection, and physical and environmental security. Every HITRUST validated assessment tests against CSF requirements calibrated to the organization's risk profile, industry, data volume, and geographic scope.

What is the passing score for HITRUST?

HITRUST uses a maturity-based scoring model rather than a simple pass/fail threshold. For r2 assessments, each control requirement is scored across five maturity levels — Policy, Procedure, Implemented, Measured, and Managed — on a 0 to 100 scale (e1 and i1 test only the Implemented level). To achieve certification, an organization must meet the minimum required average score in every in-scope domain — no single domain may fall below the threshold. Scoring is applied by the External Assessor Organization and then independently validated by HITRUST's own quality-review team before certification is issued.

What is the HITRUST AI Security Assessment?

The HITRUST AI Security Assessment evaluates security controls for organizations that develop, deploy, or operate AI systems in data-sensitive environments, addressing model integrity, data provenance, AI-specific threat vectors, and governance of AI system inputs and outputs. HITRUST also offers an AI Risk Management Assessment covering governance and risk-identification controls for AI systems. Both are add-ons layered onto an underlying e1, i1, or r2 assessment rather than standalone certifications, and are most relevant to health tech companies, SaaS platforms, and any organization whose AI products handle protected health information. A-LIGN delivers both through its HITRUST AI Security and Risk Management Assessments.

pre footer cta architecture 005 1 1 scaled

Ready to get started?

Contact us

A-LIGN is the leading cybersecurity compliance partner, trusted by over 6,400 organizations worldwide to navigate the complexities of compliance, audit, and risk. With a tech-enabled delivery model and deep domain expertise, A-LIGN delivers high-quality, efficient audits across frameworks including SOC 2, ISO 27001, FedRAMP, CMMC, ISO 42001, PCI, and HITRUST.

CONTACT US
  • Services
  • SOC 1
  • SOC 2
  • ISO 27001
  • ISO 42001
  • CMMC
  • HITRUST
  • FedRAMP
  • Penetration Testing
  • PCI DSS
  • HIPAA
  • International Services
  • Multi-Framework
  • AI Governance
  • All Services
  • Company 
  • About us
  • Partners
  • Platform
  • Careers
  • Our Team
  • Community
  • Trust Center
  • Contact Us
  • Customers 
  • Customer Stories 
  • Resources
  • Resource Center
  • Blogs
  • Case Studies
  • Videos
  • Events
  • Newsletter Sign-up
  • Guides
  • SOC 2 Compliance
  • ISO 27001 Certification
  • CMMC Compliance
  • ISO 42001 Compliance
  • HITRUST Certification
  • ISO Certificate Directory
  • Privacy Policy
  • Cookie Policy
  • Impartiality and Inquiries
  • Acceptable Use Policy
  • Sitemap
  • AI Information

Price and Associates CPAs, LLC dba A-LIGN ASSURANCE is a licensed certified public accounting firm registered with the Public Company Accounting Oversight Board (PCAOB). A-LIGN Compliance and Security, Inc. dba A-LIGN is a leading cybersecurity and compliance professional services firm.

A-LIGN 2026. All rights reserved.

  • Services
    • SOC Assessments
      • SOC 1
      • SOC 2
    • ISO Certifications 
      • ISO 27001
      • ISO 27701
      • ISO 22301
      • ISO 42001
      • ISO 45001 
      • ISO 14001
      • ISO 9001
    • Healthcare Assessments 
      • All Healthcare
      • HITRUST
      • HIPAA
    • Federal Assessments
      • All Government
      • FedRAMP
      • StateRAMP
      • FISMA
      • CMMC
      • NIST 800-171
    • PCI Assessments
      • PCI DSS
      • PCI SSF
    • Cybersecurity
      • Penetration testing
      • Red team services
      • Ransomware preparedness assessment
      • Social engineering
      • Vulnerability assessment service
    • Privacy
      • GDPR
      • CCPA/CPRA
    • Additional Services
      • International Services 
      • Multi-Framework 
      • AS9100
      • Microsoft SSPA
      • NIS2
      • C5
      • SOX 404
      • CSA STAR
      • Business Continuity & Disaster Recovery
      • Limited Access Death Master File
    • All Services
  • Platform
  • Company
    • About Us
    • Partners
    • Meet our team
    • Board of Directors
    • Careers
    • Community
  • Customers
  • Resources
    • Resource Center
    • Blogs
    • Case Studies 
    • Videos 
    • Events
    • By Service
      • SOC 2 
      • ISO 27001 
      • ISO 42001 
      • CMMC
      • FedRAMP
      • HITRUST
      • PenTest 
Image
  • A-SCEND Login
  • Careers
CONTACT US
Advertisement
Advertisement