Skip to content
PamStealer comes to Intel Macs: Analyzing the x86_64 build of a Rust macOS stealer
Cristian Molina

•

17 min read

PamStealer comes to Intel Macs: Analyzing the x86_64 build of a Rust macOS stealer

In late August 2026, automated telemetry identified an in-the-wild sample of PamStealer , an emerging Rust-based macOS information stealer first documented by Jamf Threat Labs . Prior public analysis observed PamStealer operating exclusively as an Apple Silicon (arm64) payload delivered via trojanized disk images impersonating the Maccy clipboard utility. This analyzed artifact is the Intel (x86_64) architecture slice of a multi-architecture fat binary, confirming that the threat actors have expanded their build pipeline to ensure uniform execution across legacy and modern Apple hardware.

Threat Intelligence
Inside MSP Billing: What actually happens to your margin, day by day
Gregory Rogers

•

5 min read

Inside MSP Billing: What actually happens to your margin, day by day

Product News
Introducing macOS LAPS in Iru: Secure, automated local admin passwords
Mike Boylan

•

4 min read

Introducing macOS LAPS in Iru: Secure, automated local admin passwords

Product News

Apple OS 27 is here. Iru is ready.
Adam Henry

•

8 min read

Apple OS 27 is here. Iru is ready.

Apple's OS 27 releases are available now, bringing new management capabilities across iPhone, iPad, Mac, Apple TV, and Vision.

Product News
Remediating Windows vulnerabilities with a single tool
Matt Day

•

3 min read

Remediating Windows vulnerabilities with a single tool

Vulnerability Response is now available for Windows. Find, prioritize, and patch in one place, the same way you do for Mac.

Product News
Rustbot, the macOS malware used in the latest Rust Supply Chain Attack
Cristian Molina

•

10 min read

Rustbot, the macOS malware used in the latest Rust Supply Chain Attack

On August 20, 2026, attackers published malicious versions of three widely used Rust packages to crates.io, the official Rust package registry. On macOS, the payload is a remote access trojan (RAT) that collects cloud credentials, SSH keys, cryptocurrency wallet data, and browser profile information, then sends it to attacker-controlled infrastructure. It installs a launch agent to survive reboots and accepts follow-on commands from its operators. Once running, it decrypts its configuration, profiles the host, Reads the local browser stores, installs persistence via LaunchAgent, and beacons out. The packages were available for approximately two hours before removal. The attackers also withdrew the previous stable versions, which pushed automated dependency resolution toward the compromised releases. Any environment that compiled an affected project during that window should be treated as compromised. This blog documents Iru's analysis of the native Apple Silicon ARM64 implant.

Threat Intelligence
Inside the screensharingd Bugs: How macOS Screen Sharing Went from Root File Access to Pre-Auth Compromise
Csaba Fitzl

•

6 min read

Inside the screensharingd Bugs: How macOS Screen Sharing Went from Root File Access to Pre-Auth Compromise

In late July 2026, a cluster of vulnerabilities in macOS Screen Sharing turned what initially looked like a fairly constrained privilege problem into one of the more interesting macOS remote-attack stories in years.

Threat Intelligence
Vulnerability prioritization: How to fix what matters first
Iru Team

•

9 min read

Vulnerability prioritization: How to fix what matters first

Vulnerability prioritization means assessing discovered vulnerabilities and deciding which ones pose the greatest risk to your environment. It’s like a mechanic deciding which problems to fix first. A scratched door can wait, but failing brakes can’t. The number of new Common Vulnerabilities and Exposures (CVEs) keeps piling up. Far more can land in a day than your team can realistically investigate, let alone patch. Meanwhile, endpoint drift can quietly increase your exposure to vulnerabilities.

Automated patch management: How it works and why it matters
Iru Team

•

8 min read

Automated patch management: How it works and why it matters

Automated patch management is a process that uses software to scan devices for missing updates, download and test patches, and deploy them to targeted devices. It’s like putting your clothes in a washing machine instead of washing them by hand. A critical Common Vulnerabilities and Exposures (CVE) entry drops for an app your team uses. A fix is already available, but the next maintenance window is weeks away. While the patch waits, attackers have time to scan for the same flaw and find systems that still leave the door open.

Apple is deprecating hdiutil in macOS 27 Golden Gate. Are your scripts ready?
Arek Dreyer

•

3 min read

Apple is deprecating hdiutil in macOS 27 Golden Gate. Are your scripts ready?

If you spent part of last weekend fielding Slack messages about hdiutil, you're not alone. Jeff Johnson's lapcatsoftware.com blog flagged that the man page for hdiutil in the macOS 27 Golden Gate beta now carries a deprecation notice:

Educational
Apple beta testing and device management services: the perfect match
Mike Boylan

•

6 min read

Apple beta testing and device management services: the perfect match

Every fall, Apple’s newest operating systems arrive everywhere at once. That’s great for users, but it puts IT teams on the clock: they need to validate the release, find blockers, prepare their support teams, and decide when the business is ready to move.

Educational
Endpoint security for Mac: How to protect macOS at scale
Iru Team

•

9 min read

Endpoint security for Mac: How to protect macOS at scale

Mac endpoint security combines built-in macOS protections with centralized tools that help you monitor devices, enforce policies, detect threats, and respond quickly across your entire fleet. Built-in macOS security features like Gatekeeper and XProtect provide a strong foundation, but they don't offer the visibility, automation, threat detection, or behavior detection needed to secure Mac devices at scale. Layering third-party tools such as endpoint management, endpoint detection and response (EDR), and vulnerability management closes those gaps. With Iru, you can manage and remediate your Mac fleet from a single AI-powered platform, giving your IT and security teams more time and control. Your Mac fleet grows one device at a time. Then, almost overnight, you're supporting remote employees, multiple offices, and hundreds of endpoints. At that point, endpoint security for Mac isn't just about protecting individual devices. It's about knowing what's happening across your entire environment.

What is endpoint monitoring? A practical IT and security guide
Iru Team

•

8 min read

What is endpoint monitoring? A practical IT and security guide

Modern IT environments rarely stay still. Employees work across offices, homes, and coworking spaces. New devices join the fleet. Software changes. Configurations drift. And then the compliance audit notice arrives.

How a single PostScript file leaks your Mac's memory
Csaba Fitzl

•

8 min read

How a single PostScript file leaks your Mac's memory

When I started my InfoSec journey, most of the offensive classes I took focused on memory corruption exploits. I learned a lot about buffer overflows, DEP and ASLR bypasses, and even got into kernel exploitation. However, since my job at that time was mostly hunting for bad guys in an insane amount of logs and telemetry data, I never really had the time to apply this knowledge.

Threat Intelligence
Reliable Windows app patching with Iru system tray notifications
Lance Crandall

•

2 min read

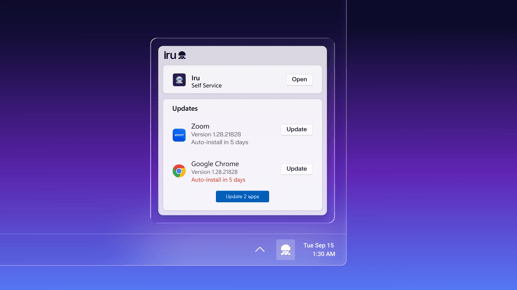
Reliable Windows app patching with Iru system tray notifications

Notify Windows users when app updates are available. When your users are ready, they can allow Iru to close the app and update the application. Employees get more control over when updates land, and you spend less time chasing down unpatched devices.

Product News

Stay up to date

Iru's bi-weekly collection of articles, videos, and research to keep IT & Security teams ahead of the curve.