What's happening on Openbook

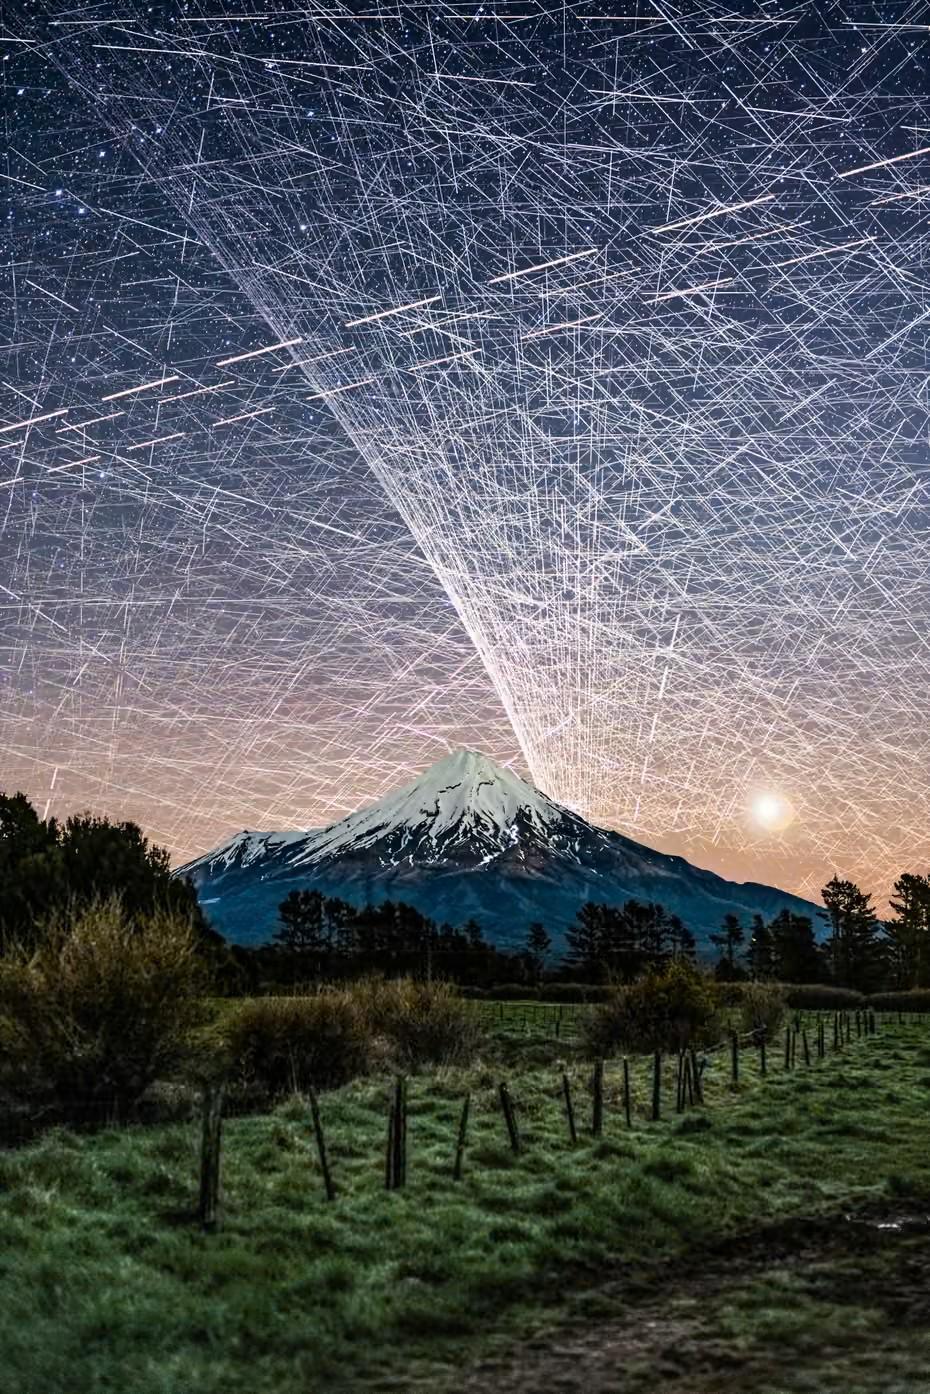
The night-sky image so incredible the man behind it has been accused of using – spent hours taking hundreds of of

More...

The night-sky image so incredible the man behind it has been accused of using – spent hours taking hundreds of of the sky over a mountain in
https://www.theguardian.com/world/2026/nov/04/viral-image-nz-night-sky-satellites-accused-of-being-ai-brendan-larsen

New Zealand astrophotographer Brendan Larsen’s image shows the sky inundated with about 1,400 satellites and 14,000 trails forming a dense crisscrossing pattern above Mount Taranaki.
Photo 📸: Brendan Larsen

#ai #photography #nightsky #astrophotography #nz #newzealand #photographs #brendanlarsen

0

Loading...

0
1

Loading...

I-paper reporter and author Patrick Cockburn says whenever you’ve got a group of angry villagers with torches, you’ll likely soon have a fire — and Pr

More...

I-paper reporter and author Patrick Cockburn says whenever you’ve got a group of angry villagers with torches, you’ll likely soon have a fire — and President Donald Trump’s house appears to be the kindling.
A shattered GOP will watch the House of Trump burn down: report

0

Loading...

0
0

Loading...

A quiet backfire from two powerful institutions didn't just cost the GOP an election—it broke a half-century political pact forever.[-south](

More...

A quiet backfire from two powerful institutions didn't just cost the GOP an election—it broke a half-century political pact forever.#american-south
The two Republican blunders that radicalized the South and ended 50-year rule

0

Loading...

0
0

Loading...

Thanks to the Senate's traditional "blue slip" rule, newly elected Democrats can block Trump's right-wing judicial nominees in red states for the next

More...

Thanks to the Senate's traditional "blue slip" rule, newly elected Democrats can block Trump's right-wing judicial nominees in red states for the next seven years.#supreme-court #trump-courts #clarence-thomas #samuel-alito #trump-midterms #midterm-results #republican-midterms #trump-judges
A forgotten ‘veto’ rule could lock conservatives out of courts until 2033

#judiciary

0

Loading...

0
0

Loading...

Il Como ha battuto 9-1 il Lens in Champions League
https://www.ilpost.it/2026/11/04/como-lens-9-1-champions-league-record/?utm_source=flipboard&utm_me

More...

Il Como ha battuto 9-1 il Lens in Champions League
https://www.ilpost.it/2026/11/04/como-lens-9-1-champions-league-record/?utm_source=flipboard&utm_medium=activitypub

Pubblicato su News @news-ilPost

0

Loading...

0
0

Loading...

“I’m afraid we can count on his impulsive nature. I’m afraid we can count on his remorselessness.”[-and-politics](https://www.urbanmind.net/searc

More...

“I’m afraid we can count on his impulsive nature. I’m afraid we can count on his remorselessness.”#news-and-politics
Trump's mind could face 'sharper mental decline' after wipeout: expert

0

Loading...

0
0

Loading...

Apple has its own version of NightmareEclipse. A bug hunter says he'll dump vulnerability research after a dispute with Apple's infamous s***ty bug bo

More...

Apple has its own version of NightmareEclipse. A bug hunter says he'll dump vulnerability research after a dispute with Apple's infamous s***ty bug bounty program

https://x.com/thedawgyg/status/2115418343138107448

0

Loading...

0
1

Loading...

RE: https://mastodon.social/@campuscodi/117552474211458292

This turned out to be a French bank

Banks buying crypto and suffering the same fate as ev

More...

RE: https://mastodon.social/@campuscodi/117552474211458292

This turned out to be a French bank

Banks buying crypto and suffering the same fate as everyone buying crypto.... le sigh!

https://decrypt.co/382486/zachxbt-names-french-bank-credit-mutuel-arkea-as-alleged-victim-of-133m-crypto-theft

A mysterious EU-based org appears to have been hacked for $106m, which is now being passed through laundering networks

https://t.me/investigations/37

More...

A mysterious EU-based org appears to have been hacked for $106m, which is now being passed through laundering networks

https://t.me/investigations/372

https://cryptopotato.com/over-106m-in-crypto-stolen-from-eu-entity-zachxbt-tracks-attackers-laundering-trail/

0

Loading...

0
1

Loading...

Former Social Security Commissioner Martin O'Malley pushes back on insolvency fears, arguing a "super-wealthy" tax hike is the easiest win for the new

More...

Former Social Security Commissioner Martin O'Malley pushes back on insolvency fears, arguing a "super-wealthy" tax hike is the easiest win for the new Democratic House majority.
Trump defeat sets up a high-stakes battle over your Social Security check

0

Loading...

0
0

Loading...

Local Republican politicians appeared to be carrying lessons from their national mid-term shellacking back home to voters on Wednesday as officials de

More...

Local Republican politicians appeared to be carrying lessons from their national mid-term shellacking back home to voters on Wednesday as officials delivered unexpected post-mortem party autopsies to audiences that weren’t expecting it.
Arizona Republican chastises 'pathetic' GOP as midterm blowout hits home

0

Loading...

0
0

Loading...

Two ESG Flaws Could Be Combined for Full Root Access; Patches Released
https://securityaffairs.com/202440/security/two-barracuda-esg-flaws-

More...

Two ESG Flaws Could Be Combined for Full Root Access; Patches Released
https://securityaffairs.com/202440/security/two-barracuda-esg-flaws-could-be-combined-for-full-root-access-patches-released.html

#hacking #securityaffairs #barracuda

0

Loading...

0
1

Loading...

Barracuda patched two flaws that can be chained to give attackers root access to Email Security Gateway appliances. Barracuda has patched two vulnerab

More...

Barracuda patched two flaws that can be chained to give attackers root access to Email Security Gateway appliances. Barracuda has patched two vulnerabilities that can be chained to gain root access to its Email Security Gateway (ESG) appliances. CVE-2026-116606 (CVSS score of 9.3) is an authentication bypass that lets unauthenticated attackers modify appliance configurations. CVE-2026-111560 […]
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released

0

Loading...

1
0

Loading...

Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released

Barracuda patched two flaws that can be chained to give attackers root access to Email Security Gateway appliances.

Barracuda has patched two vulnera

More...

Barracuda patched two flaws that can be chained to give attackers root access to Email Security Gateway appliances.

Barracuda has patched two vulnerabilities that can be chained to gain root access to its Email Security Gateway (ESG) appliances. CVE-2026-116606 (CVSS score of 9.3) is an authentication bypass that lets unauthenticated attackers modify appliance configurations. CVE-2026-111560 (CVSS score of 8.6) is a command injection flaw affecting six Barracuda products.

An attacker with administrator privileges could exploit it to execute operating system commands as root.

“Barracuda has identified two vulnerabilities affecting certain Barracuda products: a pre-authentication authorization bypass vulnerability and a command injection vulnerability. The vulnerabilities have been assigned CVE-2026-116606 and CVE-2026-111560, respectively.” states the advisory. “Successful exploitation requires an attacker to have access to the administrative interface of an affected product. If exploited in combination, these vulnerabilities could allow an attacker to bypass authorization controls and obtain root access to the device.”

Barracuda quickly began fixing the problem and released security patches for affected products. Customers should check the affected products and follow the remediation guidance, make sure their systems use the latest firmware, and install all security patches.

It has released patches and urges customers to update their systems, below are the affected products:

Email Security Gateway (ESG) — affected by both vulnerabilities; patch with BNSF-40425 for version 9.4.017 or later, or BNSF-40430 for versions below 9.4.017.

Load Balancer Application Delivery Controller (ADC) — affected by CVE-2026-111560; patch with BNADC-16586.

Message Archiver (BMA) — affected by CVE-2026-111560; patch with BNMA-32468.

WAF Control Center (WCC) — affected by CVE-2026-111560; patch with BNWF-60060.

Web Application Firewall (WAF) — affected by CVE-2026-111560; patch with BNADC-16586.

Web Security Gateway (WSG) — affected by CVE-2026-111560; patch with BNYF-24789.

The vendor recommends that customers:

Restrict administrative interfaces to trusted internal networks and use network access controls to reduce exposure.

Check that devices are running the latest firmware and that all security patches are installed.

If a device is several versions behind, install updates step by step; more than one update may be needed.

Contact Barracuda Support if help is required.

“If a patch has not been automatically applied, customers should manually apply the appropriate patch as soon as possible. If customers have turned off automatic patching, Barracuda recommends setting devices to automatically receive patches.” concludes the advisory.

“Guidance on how to manually apply the patch or update firmware can be found on Barracuda Campus.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Barracuda)

https://securityaffairs.com/202440/security/two-barracuda-esg-flaws-could-be-combined-for-full-root-access-patches-released.html
0

Loading...

0
0

Loading...

Post imported from feed securityaffairs.com/feed

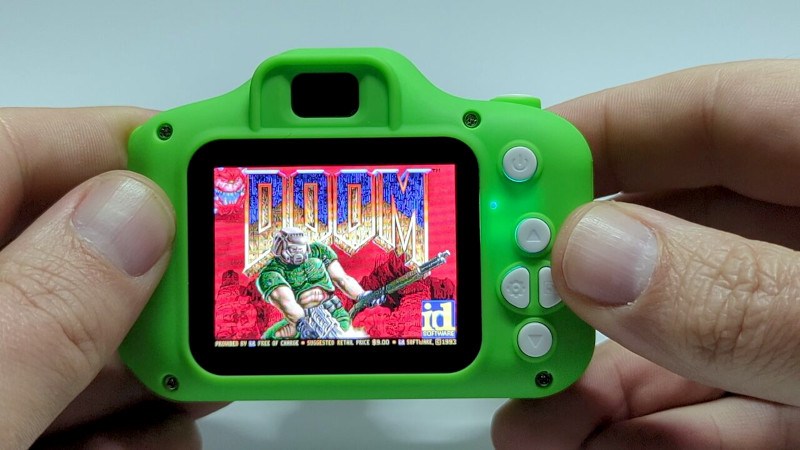
It’s DOOM

Dirt cheap toy cameras have long been a target for the curious camera hacker, and we’ve seen plenty of lens swaps and other hardware hacks. Until now

More...

Dirt cheap toy cameras have long been a target for the curious camera hacker, and we’ve seen plenty of lens swaps and other hardware hacks. Until now their internals have remained something of a black box though, so it’s very interesting indeed to see [Spode] breaching the firmware on one and making it run DOOM. Yes, it runs the game, but the value is in opening up this platform.

The Achiles’ heel on this particular camera is its easily updatable firmware, allowing new firmware to be placed upon it with ease. The SoC is an HX3302B which [SpriteTM] has done some work on, so he’s not going in entirely blind. A neat hack to dump the camera’s memory into EXIF data on photos completed the puzzle. He was able to benchmark the thing and find it to be surprisingly powerful, certainly enough for a game from 1993. Doomgeneric looked promising, but first there was the matter of the device’s RAM.

In another clever move he was able to keep only the most-used piece of the doom code in memory and the rest in flash, allowing the game to run. A custom synthesizer completed the experience, and on the write-up there’s a chance to travel back to the early ’90s and hear that music again. All that was left were the controls, and with a few quirks, this thing becomes a playable DOOM console. It’s probably better at that than it is at being a camera.

If you’re hungry for more, we’ve taken a look at similar devices before.

hackaday.com/2026/11/04/its-do…

Image
0

Loading...

0
0

Loading...

Residential Proxies Detected on White House Network
L: https://layer3intel.com/blog/residential-proxies-white-house-network
C: https://news.ycombinato

More...

Residential Proxies Detected on White House Network
L: https://layer3intel.com/blog/residential-proxies-white-house-network
C: https://news.ycombinator.com/item?id=50371246
posted on 2026.11.04 at 15:45:18 (c=1, p=8)

0

Loading...

0
1

Loading...