
Oct 16, 2026
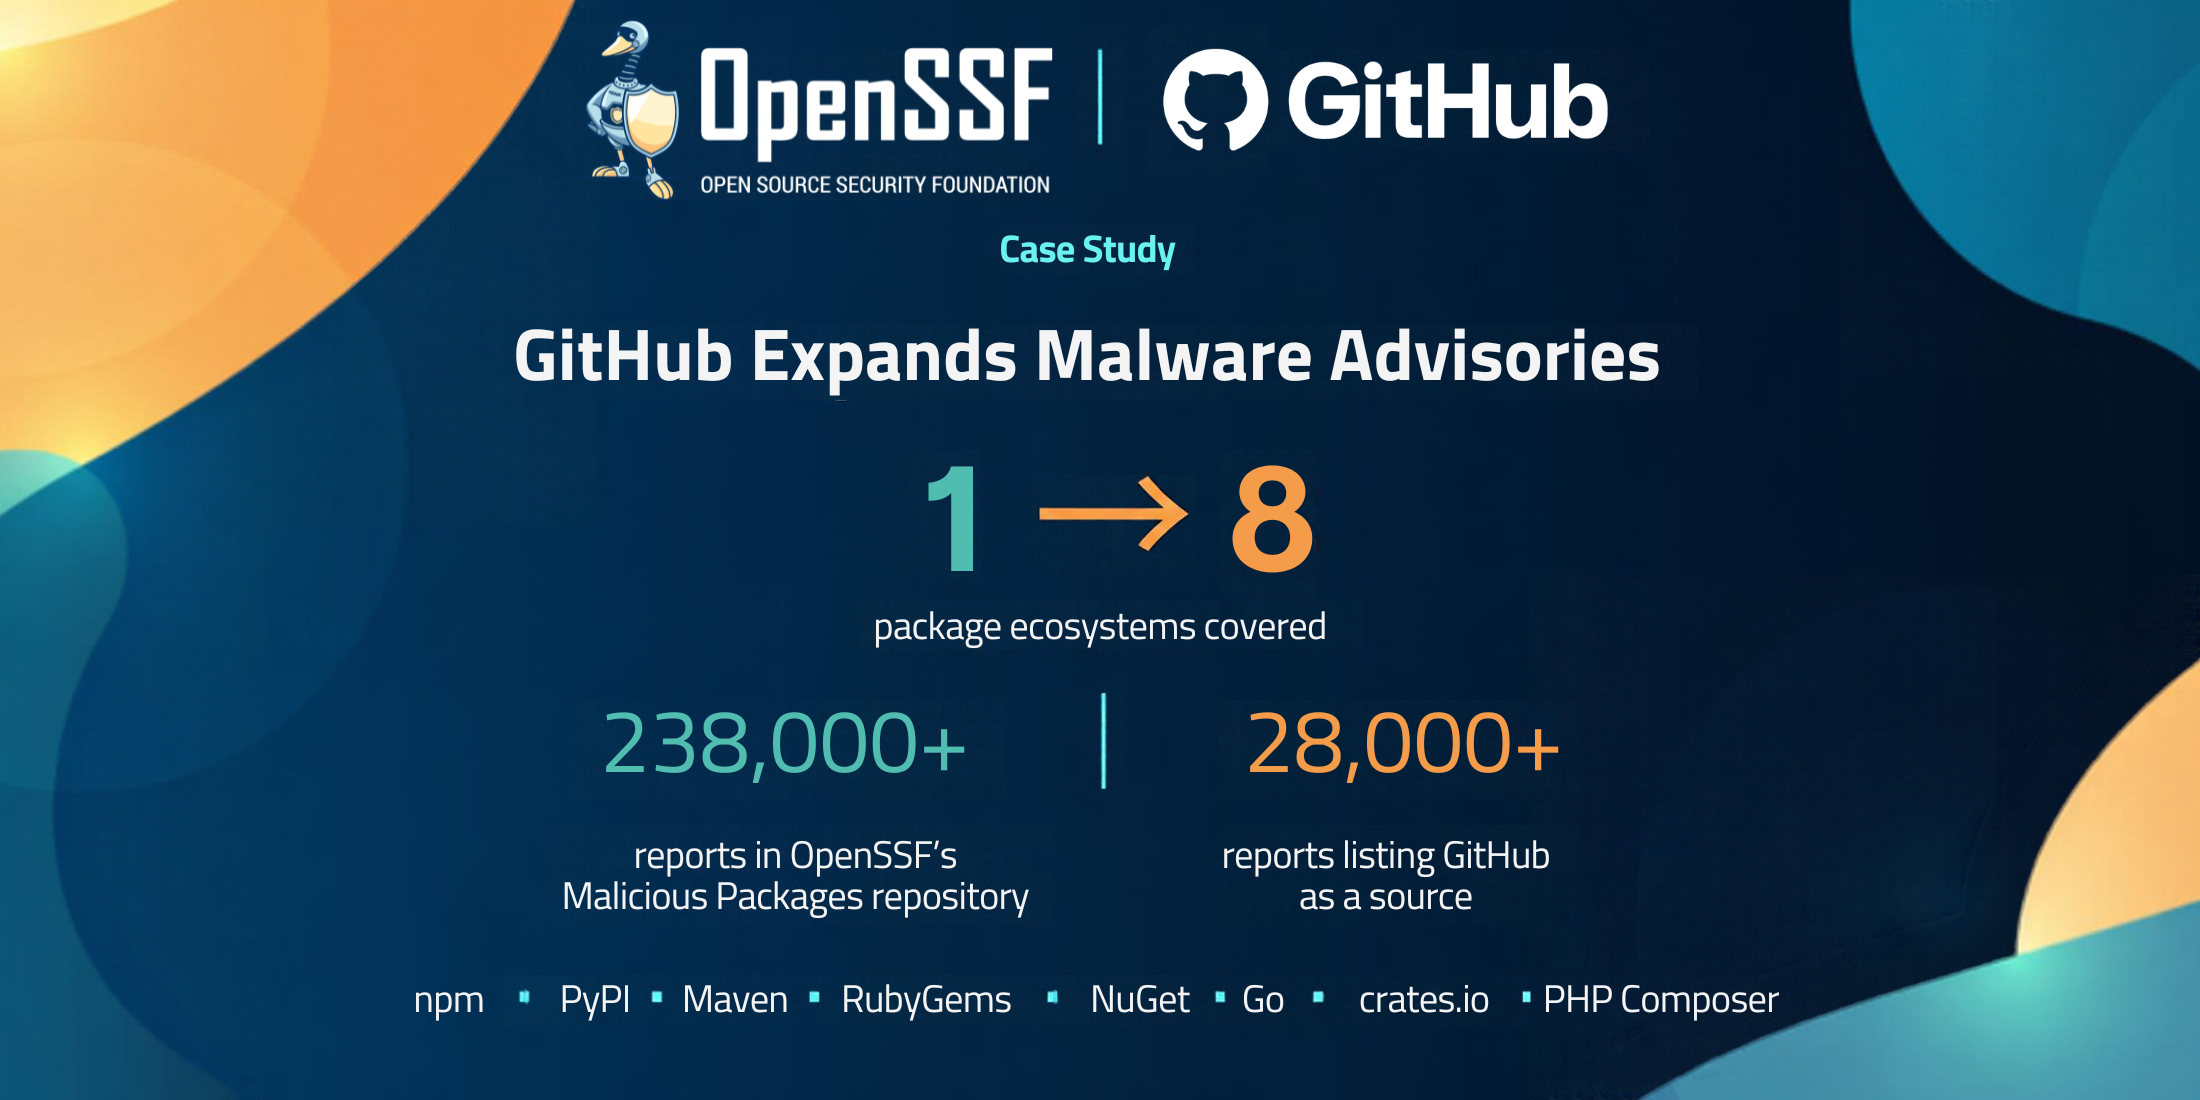
Case Study: GitHub Expands Malware Advisories Across Eight Ecosystems with OpenSSF
Learn how GitHub integrated OpenSSF's malicious-package data into its Advisory Database to expand Dependabot malware alerts across eight ecosystems. Read more.

Sep 25, 2026
Case Study: How Does IBM Turn Open Source Participation Into Enterprise and Career Value?
IBM’s Jamie Thomas explains how intentional participation in open source communities and OpenSSF drives business strategy, improves software supply chain security, and creates career growth opportunities. Read more.
Aug 26, 2026
Case Study: Conquering the EU Cyber Resilience Act (CRA) with 1,400 Upstream Security Fixes
Ericsson Software Technology successfully met the stringent obligations of the EU Cyber Resilience Act (CRA) by fundamentally shifting to upstream collaboration. Guided by OpenSSF principles, they eliminated private forks and contributed over 1,400 dependency updates and security fixes directly to open source communities. Read more.
Mar 2, 2026
Case Study: Defending the Open Source Supply Chain in a New Regulatory Era
How Red Hat and OpenSSF are translating regulatory mandates into scalable open source community practices Challenge The European Union Cyber Resilience Act (CRA) introduces legally binding cybersecurity requirements for products with digital elements (including software) placed on the EU market. While designed to bolster digital safety, these requirements relied on… Read more.
Aug 14, 2025
Case Study: How LFX Insights and OSPS Baseline Validated GUAC’s Security in Under an Hour
Tools: GUAC, OSPS Baseline, LFX Insights Challenge: Demonstrating strong security posture quickly and credibly to stakeholders Solution: Leveraging Linux Foundation Insights (LFX Insights) and the Open Source Security Foundation (OpenSSF) Open Source Project Security Baseline (OSPS Baseline) for instant, standards-aligned validation Result: Saved significant time in verifying security practices, completing… Read more.
Jul 23, 2025
Case Study: Google Secures Machine Learning Models with sigstore
As machine learning (ML) evolves at lightning speed, so do the threats. The rise of large models like LLMs has accelerated innovation—but also introduced serious vulnerabilities. Data poisoning, model tampering, and unverifiable origins are not theoretical—they’re real risks that impact the entire ML supply chain. Read more.
Jun 13, 2025
Case Study: OSTIF Improves Security Posture of Critical Open Source Projects Through OpenSSF Membership
Organization: Open Source Technology Improvement Fund, Inc. (OSTIF) Contributor: Amir Montazery, Managing Director Website: ostif.org Problem Critical open source software (OSS) projects—especially those that are long-standing and widely adopted—often lack the resources and systematic support needed to regularly review and improve their security posture. Many of these projects are maintained… Read more.
May 15, 2025
Case Study: Ericsson’s C/C++ Compiler Options Hardening Guide and OpenSSF Collaboration
Ericsson, a global leader in telecommunications and networking, has been deeply engaged in open source and software security for over a decade. Through its Open Source Program Office (OSPO), Ericsson coordinates its participation across multiple foundations and initiatives, including the Open Source Security Foundation (OpenSSF). This case study highlights Ericsson's… Read more.
Oct 24, 2024
Case Study: Kusari’s Implementation of OpenSSF Tools and Services
Challenge For many years, the software supply chain has suffered from a lack of transparency and inefficient, unsustainable security management methods such as spreadsheets, emails, and word of mouth. The severity of these challenges was highlighted during incidents like Log4Shell, where the limitations of these approaches became evident — organizations… Read more.
Aug 27, 2024
Innovative Supply Chain Security for Enterprise Cloud Platform Service
This blog explores how Guidewire Cloud Platform is using and collaborating with GUAC. Read more.
