Governance, Risk & Compliance (GRC) Management

WHAT’S NEW
We specialize in helping organizations navigate the complexities of AI integration with our comprehensive AI Framework Implementation Services. Our expert team is dedicated to ensuring your AI systems are not only cutting-edge but also compliant with the latest standards and regulations.
Read more
- NIST AI Risk Management Framework Implementation: We guide you through the adoption of NIST’s guidelines, ensuring your AI systems are transparent, fair, and accountable.
- ISO 42001 Compliance: Our team assists in implementing the ISO 42001 standard, focusing on data privacy, security, and ethical considerations to ensure responsible AI management.
- FTC Compliance: We help you adhere to the Federal Trade Commission’s guidelines on the ethical use of AI, ensuring your systems protect consumer rights and prevent deceptive practices.
Hide What’s New
- Pass industry mandated security and privacy assessments
- Align employee activities to corporate goals – optimize business success
- Identify business risks early to enable early course correction
Advisors evaluate GRC readiness, implement best-of-breed solutions, and manage tools and processes to help clients achieve continuous compliance.
We offer both managed and professional cybersecurity services. Our managed services provide continuous, proactive protection, while our professional services deliver expert, project-based solutions for specific needs.
Our Solutions
Training

Our specialized training programs are designed to elevate your organization’s understanding and execution of Governance, Risk, and Compliance (GRC) principles, ensuring that every role is equipped to manage risk effectively.
Awareness Training
Fundamental Concepts: Deliver sessions that cover the basic principles of GRC, emphasizing regulatory mandates and best practices.
Empowering employees with GRC knowledge reduces operational risks and promotes a proactive compliance culture.
Policy and Controls Training
Targeted Skill Development: Provide specialized training for your GRC team on developing, implementing, and managing robust compliance frameworks.
In-depth training equips your team to manage policies and controls that safeguard against regulatory breaches and internal risks.
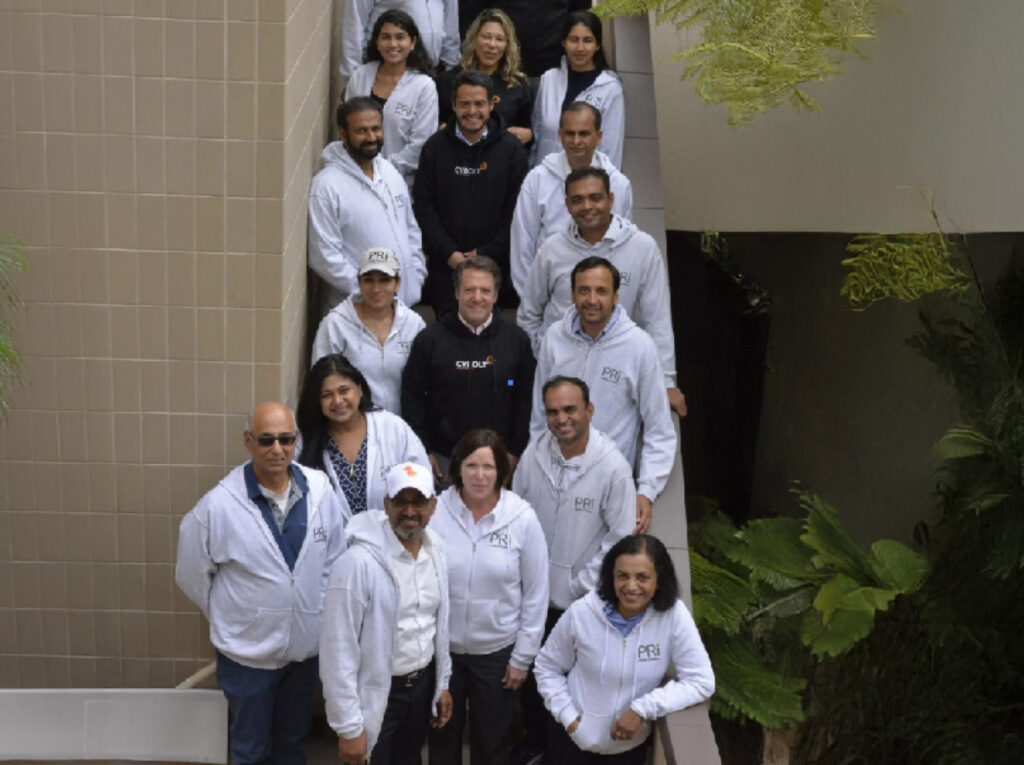
Cybolt + Pontis Research Inc.
Partnership brings Pontis Research’s three decades of Identity Access Management (IAM) expertise to Cybolt
May 23, 2024
Cybolt a leading provider of cybersecurity services in Latin America , announced the integration of Pontis Research Inc., a U.S.-based company specializing in Identity and Access Management(IAM) and risk management for three decades. Cybolt is set for dynamic expansion into North America, with an eye on going public in the next five years.