Image

One-stop Tool Shows Apple Intelligence The Door

Don’t want AI features on your Mac? Tough luck, unless one wants to imperfectly do it by hunting down settings in about a dozen different places. Even then, the multi-gigabyte models stay on disk. Unsatisfied by this state of affairs, [omlahore] created RemoveMacAI, a one-stop-shop debloater that shows Apple Intelligence the door, reclaiming its disk space on the way out.

ImageWith RemoveMacAI one has a single location from which to turn individual AI features off, delete the models behind them, and block MacOS from downloading them again by redirecting attempts to a closed local port.

What’s refreshingly nice about the tool is how transparent it is about what each setting or preset will change, and communicates clearly what exactly one loses access to by disabling it. Want it all gone? Easy. Use one or two features, but don’t want the rest? No problem. All changes are shown up-front before the tool changes anything, and all alterations are reversible.

Released only a couple weeks ago, to say the tool is popular would be an understatement. Windows 11 also got a “remove AI features” tool, and it requires constant updating to stay functional. Will a future MacOS update interfere similarly with RemoveMacAI? Probably, but one thing that is clear is that a tool like this resonates deeply with a nontrivial number of users.

Image

Testing Oneself For AI Slop

The feed of a Hackaday writer brings many surprises, some rubbish, and the occasional diamond which of course we bring to you. Sometimes a page catches the eye that’s not a Hackaday piece per se, but makes for interesting reading. Today there was an example which provides a catalyst for a story if not being one itself.

It’s an AI skill intended to make a slop-writing operation look less sloppy, and since it contains a list of slop behaviours, of course it’s irresistible to turn it on yourself. To delve into the archives, if you will. So here goes, how slop-like is your scribe?

It kicks off with the old favourite, “Delve“. Oh dear, that one’s in the List Hackaday corpus quite a bit. Earliest appearance: 2016. Then landscape terms, in which it’s easy to recognise “Sphere” again. Oops. 2016 again. How about “Testament“? Well, that one’s a 2017 word. “Pivotal“? Four years of the Raspberry Pi, back in 2016. How about “Showcase“? Yup, it’s there, in 2019. Meanwhile “Foster“, goes back to 2017.

Next up are “Leverage” and “Utilise“. Safe ground here. Editors have what are referred to a “Pet Peeves”, language tics that annoy them on sight, and those two regrettable pieces of business-speak never evade this red pencil. The word you are looking for is “Use”.

The page goes on to name a load more words as tells, and we could continue to dissect them for your amusement, but we think you get the message from long-pre-LLM Hackaday. It gets more interesting when it talks about paragraph structure, and there are the things we’d recognise as tells. Staccato paragraphs, one-line stacks for impact, and repeated sentence start words. Whether AI slop is sounding like a business influencer’s Linkedin posts, or the other way round, is anybody’s guess. And yes, Hackaday does use em-dashes — get over it.

It’s amusing to poke mild fun at your past writing style, but if there’s a serious point in there it’s that spotting slop is never as easy as having a check-box list of tells when in fact you’re just looking at professional-grade command of the language. After all, given that Hackaday is in its corpus, the LLM can even make a passable effort at writing like one of us. Perhaps the key lies in that article, when the fake Hackaday piece became obvious because it lacked the inference of the real one.

Image

This Week In Security: New Spectre Attacks, Crushing Quantity Of Linux Vulns, Google Gets Too Much AI, And Hacking Lawnmowers

Just-in-time, or JIT, compilation could be considered a fundamental backbone of modern computing.  JIT compilation turns scripting languages like JavaScript or intermediary binary forms like Web Assembly into native code on the fly, giving web apps, and things that are web apps under the covers like Electron-based tools, near native speed.  A new paper explores leveraging JIT systems to revive Spectre-v2 attacks against processors.

Most modern processors gain performance by using a trick called “speculative execution”.  The processor guesses the likely result of a compare, and begins executing some of the next instructions before the results are actually known.  If the processor guessed right, things continue and there is a speed gain because it can jump ahead, but if the processor guessed wrong, any instructions that were run and any side effects of running them are discarded and execution resumes on the actual path.  In theory, anyhow.

In practice, the Spectre class of attacks targets branch prediction. It was discovered that when the wrong branch was chosen, not all of the results were truly hidden; Patterns of failures in guessing branches can be used to leak behavior processing encryption keys and other activities. The attacks evolved with the research dubbed Spectre-V2, which showed that non-privileged contexts, like non-root users and virtual machines, could poison the instruction prediction and use it to read arbitrary memory.  Fixes to the Linux kernel and other platforms were required to mitigate the worst of the effects.

The paper shows that by using self-modifying code in the JIT, the processor can be tricked into loading cached versions of the instructions.  The fixes to the kernel to prevent Spectre attacks include identifying malicious code patterns that attack the branch prediction, and stopping or changing them:  By causing the CPU to execute the cached copy of instructions instead of the live copy, the attack ignores the fixed instructions entirely and can attack the branch prediction algorithm.

To prove the attack is feasible in the real world, the researchers targeted several JIT compilers, including the SpiderMonkey JavaScript engine used by Firefox, the eBPF JIT found in the Linux kernel, and GraalVM, the JIT used in Python.  They found success with each, demonstrating that the attack is at least plausible.

Research like this is unlikely to be an instant world-melter, and will help find possible mitigations in the future to prevent these sorts of attacks.  Operating systems that support a high-security “lock-down” mode, like macOS and iOS, often disable JIT entirely, out of concern about these sorts of attacks.  There’s probably no need to start disabling JIT on every system, but attacks like these have a tendency to evolve.

Continue reading “This Week In Security: New Spectre Attacks, Crushing Quantity Of Linux Vulns, Google Gets Too Much AI, And Hacking Lawnmowers” →

Image

A New Type Of LLM On The Block: Decision-Making Models

Large language models (LLMs) output language, but they are commonly tasked with making a decision or classification of some kind instead of writing an essay or chat reply. An LLM will be provided with input, and asked to classify that content in some way: with a rating, yes/no answer, a best-fit categorization, and so forth. A recent new type of model by the name of Jev was released only weeks ago and it is extremely fast, ultra-cheap, and laser-focused on that decision-making role. It can’t write even a single sentence, but it can classify and categorize very, very quickly.

Jev works like this: it still accepts text input, but it outputs only floating-point numbers. Those numbers are the “answers” to user-specified yes/no type questions, lists of choices, and scoring-type requests. [Simon Willison] provides a concise summary of what Jev does, and what makes this new category of model so interesting.

To say that the idea has caught on would be a wild understatement. Folks are making their own decision-type models and experiments in a flurry. Kev and Nimble are two examples (Nimble was added as a supported model in Ollama just recently, and is small enough to run locally with relative ease.)

If this type of local AI model was the missing link you needed to get an idea working, don’t keep it to yourself! Tell us all about it on the tips line.

Image

How To Talk To A Machine Without Anthropomorphising It

LLMs remain a divisive topic in these times. Perhaps we all know someone who’s become over-infatuated with their new robotic friend, or who believes it has made them a genius. [Emily M. Bender] and [Nanna Inie] have written about how people anthropomorphise the LLMs they interact with, and suggested some language tips to avoid that. It’s a couple of months old, but we think Hackaday readers will find it interesting.

Their analysis is interesting, because it looks at the way people talk about LLMs and highlights the unconscious anthropomorphism. The LLM is a piece of software not a person, so why does it “recognise” when it does “speech recognition”, for example. They suggest “automatic transcription” instead. Even “hallucination” implies cognisance that evidently isn’t there. They admit that their suggestion of “undesirable output” isn’t entirely appropriate. They’re on safer ground with “input” and “output” instead of “prompt” and “response”.

Whatever your views on them, it’s evident that LLM usage will be a feature of the world for the forseeable future. The language surrounding them is however capable of evolving, and maybe some of the suggestions here are worth taking note of.

Grappling with our new electronic overlords? Have a look at our AI for Skeptics series.

Image

This Week In Security: Baked-in Malware, Freezers Not Freezing, Zoom Snoops Clipboards, And AI Makes Things Worse, Faster

The AI platform ServiceNow which offers both hosted and on-premises versions just patched a trifecta of CVSS-10 vulnerabilities.

CVSS rankings are determined by the severity of a flaw, the ease of exploiting the bug, if authentication is required for exploitation, if the vulnerability exposes confidential data, and other criteria. A CVSS of 10 is as bad as it gets, and having three of them at once is certainly attention-getting. Of the three vulnerabilities fixed, one allowed unauthenticated modification of data in the hosted instance, a second allowed arbitrary code execution via the GraphQL interface, and the third allowed arbitrary SQL commands that could modify the database.

ServiceNow claims Adobe, Lenovo, Fedex, and Fujitsu among their high-profile customers. With luck, the vulnerabilities were patched before significant public exploitation could happen.

Router Malware

Previously in 2026 the US Government warned against embedded malware found in consumer routers, which may be linked to the FCC enacting bans against certification and import of foreign-made consumer devices. This week, the NVD (National Vulnerability Database) reported specific embedded malware in the Zbtlink and MoreQuick brands of devices.

Multiple versions of the firmware, for multiple lines of products, contain a backdoor service that uses unencrypted UDP to connect to a command and control (C2) service. The service, or anyone able to intercept the network traffic, since it’s unencrypted, can execute commands as root, allowing them to change configurations, open tunnels, or steal ISP credentials.

The malware is baked into the firmware, so removing it is impossible for most users: a factory reset wouldn’t do. In theory if third-party firmware like OpenWRT supports these devices, the hardware could be made safer with a custom install.

Given how commonly the same device is marketed under dozens of names, likely the same devices and firmware have yet to be identified under other brands. Continue reading “This Week In Security: Baked-in Malware, Freezers Not Freezing, Zoom Snoops Clipboards, And AI Makes Things Worse, Faster” →

Image

The Birds Outside, Drawn For You Automatically

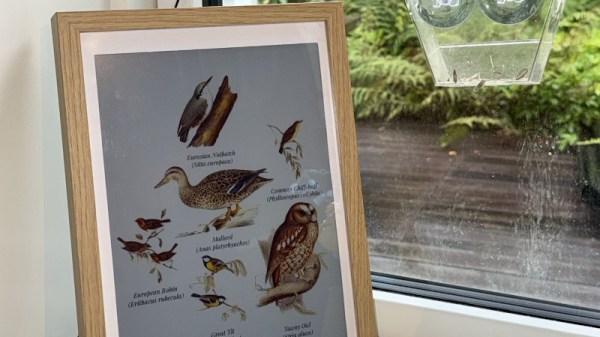
With artificial intelligence being the bête noir of the moment, there are some projects using it which maybe don’t bring much to the table. So it’s nice to see one that uses it in a creative way, and delivers something new. [arnegiacomo]’s e-paper screen is a great example, as it draws a picture in real time of whatever birds are outside.

Behind the quite large screen sits a Raspberry Pi 5, and on that is BirdNet-Go, an AI-powered birdsong classifier. A USB microphone catches the birdsong, and Birdnet comes up with the species. The birds on the display are then those species as pictures from 19th century bird spotters guides, assembled into a collage. You can even see what the current set of birds it hears are, live, and they are a representative cross section of the European birds you’d find in Norway where it’s located.

We like this project, both for the bird book vibe it gives, and the creative use of machine classification. Surprisingly this isn’t the first project in this field we have seen over the years.