
Image

This Week In Security: More Linux Bugs, Biggest Crypto Theft Ever, Prusa Printers, Residential Proxies

Linux kernel bugs which can be triggered remotely, without any login, are rare. Most kernel vulnerabilities need an attacker to already be running code on the machine. CVE-2026-98432 is one of those: a use-after-free in the IPv4 TCP handshake code, rated CVSS 9.8, which Atlas has written up in detail. It goes all the way back to Linux 4.4.

A use-after-free is exactly what it sounds like: the program releases a chunk of memory, but some other code keeps using it. If an attacker can get their own data placed into that freed memory before it’s used again, they can influence what the kernel does next. In this case, when a server accepts a connection whose SYN packet carries IPv4 header options (a rarely used feature of IPv4), the kernel hands those options from the half-open connection to the full connection without copying them, then frees them while another CPU core may still be reading them. The fix is a four-line change, from “kfree()” to “kfree_rcu()”, which waits until every reader is done before freeing the memory. A lost race simply fails the handshake, so an attacker can keep trying.

The bug was reported by Xinyang Ge at Anthropic, and Anthropic says its Claude model wrote a working proof-of-concept that gets root on “Linux servers with a multipath TCP listener.” Multipath TCP (MPTCP) lets a single connection use several network paths at once, like WiFi and cellular, and you might assume almost nobody runs it on servers. Unfortunately, as Marcus Hutchins points out, Debian kernels enable MPTCP by default, and Go 1.24 and newer open MPTCP listening sockets by default when the kernel allows it, so anything built in Go (including the Caddy web server) is potentially exposed. Hutchins’ scans found about 2.1 million servers reachable over MPTCP on port 443, and he’s already seeing scanning from residential proxies and Russian VPNs which looks like it’s specifically hunting for this bug.

Upstream stable kernels were fixed in mid October, but as of October 31, Ubuntu and Red Hat were both still listed as vulnerable, with fixes in progress. If you can’t patch yet, you can check for MPTCP listeners with “ss -Mlnp”, and disable MPTCP with “sysctl net.mptcp.enabled=0”, but note that this doesn’t affect sockets which are already open, so you’ll need to restart any services using them. Red Hat and AlmaLinux have also published firewall rules which drop TCP packets carrying IPv4 options, which basically no legitimate traffic uses.

We haven’t seen bulk exploitation of this vulnerability yet, which might hint that it’s less trivial to trigger than the severity might indicate, but it’s a great time to get servers up to date. “Not exploited yet” has a nasty habit of turning into “every vulnerable server exploited in a day”.

Meanwhile, on the local side, OpenAI has published the results of pointing an automated pipeline, built on an unreleased “cyber-focused” model, at the kernel. In a run in mid October, it found 2,300 candidate bugs, reproduced 1,700 of them, and produced 948 working local privilege escalation exploits against a stock desktop Linux distribution, for about $1.2 million in API credits, or roughly $1,279 per root exploit. That’s not cheap, but for comparison, Pwn2Own has historically paid $20,000 for a single Linux kernel privilege escalation. Local privilege escalation is the step after an attacker gets a foothold: turning an ordinary user account, a compromised web app, or a sandboxed process into full control of the machine. Coupled with even a basic vulnerability in other code, it can allow an attacker to take full control of the system and hide the compromise much more effectively.

OpenAI says it’s working with the kernel community to report the bugs and submit patches, starting with the most critical, and that during the ten days the scan was running, more than 100 other kernel privilege escalation bugs were patched by other contributors, with about 300 more being discussed publicly. The most sobering line in the report is that, for now, a low-privileged account on an unpatched system “should be considered functionally equivalent to root access for a well-resourced threat actor.” It’s been quite a week for kernel developers, and it’s not going to slow down any time soon.

The flood of AI discovered vulnerabilities seems to continue unabated, and it’s easy to feel under attack from them. Consider, however, how often the open source community has called for companies using open source tools and libraries as core elements of their business to help support those tools and community. There’s still a significant burden placed on the community maintainers when almost 2000 bug reports land in a week, but over $1 million investment in securing Linux isn’t nothing, and the patches at least appear to be reasonably scoped and accurate. I’m pretty sure we’d see an article covering Linus’s response if they weren’t.

Continue reading “This Week In Security: More Linux Bugs, Biggest Crypto Theft Ever, Prusa Printers, Residential Proxies” →

Image

ToothPaste Goes Where Your Password Manager Doesn’t

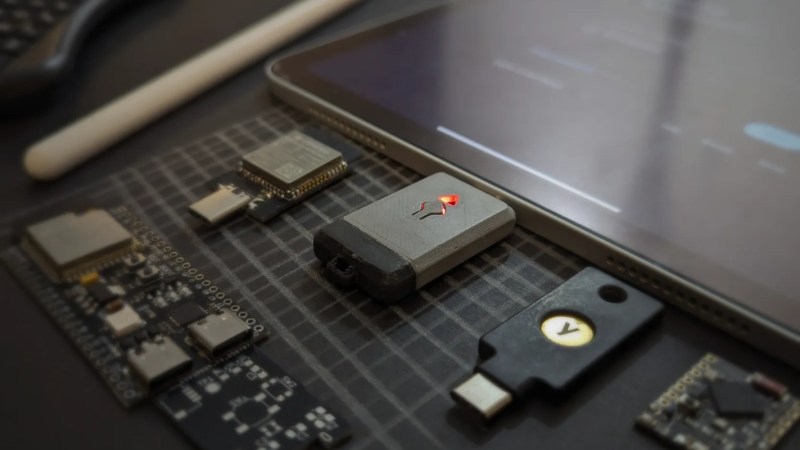
One of the easiest ways of improving security and privacy when using the Internet, and computers in general, is to use strong passwords unique to each site or service. A password manager makes this easy on your phone or computer, but what if you’re in a situation where you can’t install any software on the device you’re logging into? In that case, maybe it’s time to get out the Toothpaste.

The way this creation from [brisk4t] works is that an ESP32-S3 is programmed to act as a keyboard and mouse for any computer it’s plugged into. From there, it connects over an encrypted WEB-BLE connection to another device like a laptop or smartphone. This second device can send text to the ESP32 acting using an extension for Chromium-based browsers, and the ESP32 sends it over the USB connection as if it were nothing more than a standard keyboard. This is all done without having to install any apps or drivers on the target machine, since any machine in the last two or three decades can recognize a USB keyboard and mouse with no problem.

Not only does this allow for easy password input for awkward situations, this can also be used for BIOS where an app couldn’t be installed anyway, for air-gapped systems with no networking, or insecure systems the user doesn’t trust. If you don’t need quite as many bells and whistles, we’ve seen a similar technique pulled off with an ATtiny85.

Image

This Week In Security: Broken Embargoes, UEFI Overflow, Wormable Tailscale, Starlink Ad Snooping, And A DHS Directory Dump

Last week brought us at least two broken embargoes: php2shell leaked onto Hacker News a day early, and a batch of Linux kernel bugs landed on the public kernel mailing list instead of the private security list. This week has been slightly less exciting overall, fortunately, but Akamai’s security team published a pointed essay titled “TLP Is Not a Suggestion”, and it’s hard to argue with the timing.

When a researcher finds a serious bug, the usual process is “coordinated disclosure”. The developers get time to build a fix, and downstream vendors get advance notice under embargo so patches and protections are ready the moment details go public. The Traffic Light Protocol (TLP) is the vocabulary everyone uses to say who may know what: TLP:RED for named recipients only, TLP:AMBER for an organization and its clients on a need-to-know basis, TLP:GREEN for a trusted community, and TLP:CLEAR for anyone. It has no legal teeth whatsoever. It’s not classified data in a legal sense. It works because everyone involved agrees to make it work.

Akamai’s complaint isn’t really about the original php2shell leak, but about what came after: vendors and researchers racing to confirm, reproduce, and publish first. According to Akamai, a researcher published a reconstruction of the bug before the patch existed, and exploitation attempts started before most admins knew there was anything to patch. They draw parallels to Heartbleed in 2014, where a handful of companies got early notice and then advertised that they were already safe while Linux distributions were caught flat-footed, and to Meltdown and Spectre in 2018, where a six-month embargo collapsed six days early.

In the rush to publish, it’s also become less clear what the actual severity of the bug is in the real world. It clearly exists, and is of concern, but groups are still struggling to prove a complete exploit path, with several challenges showing results but nothing definitive so far.

Their advice boils down to “protect first, publish second”: push the detection rules and virtual patches, tell your customers privately, and save the blog post for after the official advisory. With AI tooling shrinking the time between “details exist” and “working exploit” to hours, the cost of a broken embargo is going up, not down.

Continue reading “This Week In Security: Broken Embargoes, UEFI Overflow, Wormable Tailscale, Starlink Ad Snooping, And A DHS Directory Dump” →

Image

This Week In Security: Record Patch Tuesday, PHP’s Bad Time, The Oldest Vuln, AI Armies, And More

It’s no longer a proper month without Microsoft breaking its own record for security fixes, and October’s Patch Tuesday was no exception. Brian Krebs brings the roundup: more than 1,400 vulnerabilities fixed in a single batch, dwarfing September’s record of nearly 1,000, which itself was about ten times the normal monthly load. According to Tenable, Microsoft has now passed 4,000 CVEs for the year with two months still to go.

Only one of the fixes is for a vulnerability already being exploited in the wild: CVE-2026-96951, a security feature bypass in the Windows Shell affecting Windows 10, 11, and some Server versions. A .NET Framework bypass, CVE-2026-108398, was publicly disclosed before the patch, giving attackers a head start, and with modern AI tooling, it seems like not much of a head start is needed. At least 78 of the bugs are rated critical, and most of those allow remote code execution with little or no user interaction. Windows 10 holdouts can relax a little: Microsoft quietly extended free updates through October 2027.  Given the pace of exploitation, this is probably the only way to prevent an Internet-scale meltdown.

Microsoft credits LLM-driven bug hunting for the volume, which leaves the poor admins who have to test and deploy all of this in an unenviable spot. Fortra’s analysis shows that only 26 Microsoft vulnerabilities have landed in the CISA KEV catalog of actively exploited bugs so far this year, so start there. For the rest, the SANS Internet Storm Center and Cisco Talos have the usual breakdowns by severity. Or, you know, just patch everything and hope for the best, which is roughly what everyone does anyhow.

Continue reading “This Week In Security: Record Patch Tuesday, PHP’s Bad Time, The Oldest Vuln, AI Armies, And More” →

Image

This Week In Security: Critical DNS Keys Rotated, Hacking Freezers Isn’t Cool, OpenAI Spies On Itself, And Advanced Hardware Wallet Hacks

Critical Internet keys changed this week. Did you notice?  The keys behind DNSSEC, the system for cryptographically validating DNS responses, rolled over on October 11 2026. This is the second time the DNSSEC keys have rotated since the system was implemented, and the first time in 2018 didn’t exactly go entirely smoothly.

DNS is what resolves a host name and turns it into an IP address. It underpins web browsing, email, and just about every other connection. It’s also a very early Internet protocol, written in both a simpler, less paranoid era, and an era where encryption was computationally expensive and legally problematic. DNS offers little protection against malicious actors spoofing responses, and the impacts range from phishing to redirecting email to just about any other manipulation of connections you can image.

DNSSEC addresses this by creating a chain of trust between DNS resolvers — the servers that forward the DNS query into the DNS infrastructure and return the results — and the global DNS servers. Part of this chain of trust is the root key that each resolver must have and trust, and this key is what changed this week.  DNSSEC resolvers automatically watch for a new root of trust key, but the key must be signed by the previous root of trust, and is checked for at least 30 days before it is trusted.  If someone were able to issue a bogus certificate, they would have to maintain control of the infrastructure for over a month before DNS resolvers would trust it.

The process of distributing the new key actually began more than a year ago, on January 11, 2025, to give DNSSEC resolvers time to get the new key. DNSSEC services should have had plenty of time to obtain and trust the new key, and unless DNS stopped working for you this week, they did their job.

The next major change for DNSSEC will require more profound changes to deploy a new signing algorithm that will be post-quantum secure.

Continue reading “This Week In Security: Critical DNS Keys Rotated, Hacking Freezers Isn’t Cool, OpenAI Spies On Itself, And Advanced Hardware Wallet Hacks” →

Image

This Week In Security: New Spectre Attacks, Crushing Quantity Of Linux Vulns, Google Gets Too Much AI, And Hacking Lawnmowers

Just-in-time, or JIT, compilation could be considered a fundamental backbone of modern computing.  JIT compilation turns scripting languages like JavaScript or intermediary binary forms like Web Assembly into native code on the fly, giving web apps, and things that are web apps under the covers like Electron-based tools, near native speed.  A new paper explores leveraging JIT systems to revive Spectre-v2 attacks against processors.

Most modern processors gain performance by using a trick called “speculative execution”.  The processor guesses the likely result of a compare, and begins executing some of the next instructions before the results are actually known.  If the processor guessed right, things continue and there is a speed gain because it can jump ahead, but if the processor guessed wrong, any instructions that were run and any side effects of running them are discarded and execution resumes on the actual path.  In theory, anyhow.

In practice, the Spectre class of attacks targets branch prediction. It was discovered that when the wrong branch was chosen, not all of the results were truly hidden; Patterns of failures in guessing branches can be used to leak behavior processing encryption keys and other activities. The attacks evolved with the research dubbed Spectre-V2, which showed that non-privileged contexts, like non-root users and virtual machines, could poison the instruction prediction and use it to read arbitrary memory.  Fixes to the Linux kernel and other platforms were required to mitigate the worst of the effects.

The paper shows that by using self-modifying code in the JIT, the processor can be tricked into loading cached versions of the instructions.  The fixes to the kernel to prevent Spectre attacks include identifying malicious code patterns that attack the branch prediction, and stopping or changing them:  By causing the CPU to execute the cached copy of instructions instead of the live copy, the attack ignores the fixed instructions entirely and can attack the branch prediction algorithm.

To prove the attack is feasible in the real world, the researchers targeted several JIT compilers, including the SpiderMonkey JavaScript engine used by Firefox, the eBPF JIT found in the Linux kernel, and GraalVM, the JIT used in Python.  They found success with each, demonstrating that the attack is at least plausible.

Research like this is unlikely to be an instant world-melter, and will help find possible mitigations in the future to prevent these sorts of attacks.  Operating systems that support a high-security “lock-down” mode, like macOS and iOS, often disable JIT entirely, out of concern about these sorts of attacks.  There’s probably no need to start disabling JIT on every system, but attacks like these have a tendency to evolve.

Continue reading “This Week In Security: New Spectre Attacks, Crushing Quantity Of Linux Vulns, Google Gets Too Much AI, And Hacking Lawnmowers” →

Image

This Week In Security: ShinyHunters Won’t Dox The FBI, Pentagon Data Stolen, And OBS Vulnerable

404 Media reports that the ShinyHunters group who stole multiple terabytes of FBI employee data say they do not plan to release the data.

Known for ransomware and extortion of innumerable companies and government agencies, ShinyHunters used a zero-day vulnerability in Oracle PeopleSoft to compromise the employment site of the FBI and pivot into scraping the content of FBI AWS instances, claiming to have the full employment and health data of all FBI agents, employees, and spouses.

The hacker group took exception to an FBI press release that claimed that the group over-stated stolen data and that they directly harass victims and victim’s families.  The group publicized the FBI data breach, demanding a retraction of the statements, and it was generally assumed that the group would follow their typical methods of releasing the data publicly if the demands were not met.

The group has told 404 media that they had always agreed internally to not release the stolen data, saying “This was all a marketing campaign to protect our business and actively combat disinformation”.  Meanwhile the FBI continues the investigation, and Shiny Hunters may be hoping to defer some of the ire.

Continue reading “This Week In Security: ShinyHunters Won’t Dox The FBI, Pentagon Data Stolen, And OBS Vulnerable” →








