Image

This Week In Security: More Linux Bugs, Biggest Crypto Theft Ever, Prusa Printers, Residential Proxies

Linux kernel bugs which can be triggered remotely, without any login, are rare. Most kernel vulnerabilities need an attacker to already be running code on the machine. CVE-2026-98432 is one of those: a use-after-free in the IPv4 TCP handshake code, rated CVSS 9.8, which Atlas has written up in detail. It goes all the way back to Linux 4.4.

A use-after-free is exactly what it sounds like: the program releases a chunk of memory, but some other code keeps using it. If an attacker can get their own data placed into that freed memory before it’s used again, they can influence what the kernel does next. In this case, when a server accepts a connection whose SYN packet carries IPv4 header options (a rarely used feature of IPv4), the kernel hands those options from the half-open connection to the full connection without copying them, then frees them while another CPU core may still be reading them. The fix is a four-line change, from “kfree()” to “kfree_rcu()”, which waits until every reader is done before freeing the memory. A lost race simply fails the handshake, so an attacker can keep trying.

The bug was reported by Xinyang Ge at Anthropic, and Anthropic says its Claude model wrote a working proof-of-concept that gets root on “Linux servers with a multipath TCP listener.” Multipath TCP (MPTCP) lets a single connection use several network paths at once, like WiFi and cellular, and you might assume almost nobody runs it on servers. Unfortunately, as Marcus Hutchins points out, Debian kernels enable MPTCP by default, and Go 1.24 and newer open MPTCP listening sockets by default when the kernel allows it, so anything built in Go (including the Caddy web server) is potentially exposed. Hutchins’ scans found about 2.1 million servers reachable over MPTCP on port 443, and he’s already seeing scanning from residential proxies and Russian VPNs which looks like it’s specifically hunting for this bug.

Upstream stable kernels were fixed in mid October, but as of October 31, Ubuntu and Red Hat were both still listed as vulnerable, with fixes in progress. If you can’t patch yet, you can check for MPTCP listeners with “ss -Mlnp”, and disable MPTCP with “sysctl net.mptcp.enabled=0”, but note that this doesn’t affect sockets which are already open, so you’ll need to restart any services using them. Red Hat and AlmaLinux have also published firewall rules which drop TCP packets carrying IPv4 options, which basically no legitimate traffic uses.

We haven’t seen bulk exploitation of this vulnerability yet, which might hint that it’s less trivial to trigger than the severity might indicate, but it’s a great time to get servers up to date. “Not exploited yet” has a nasty habit of turning into “every vulnerable server exploited in a day”.

Meanwhile, on the local side, OpenAI has published the results of pointing an automated pipeline, built on an unreleased “cyber-focused” model, at the kernel. In a run in mid October, it found 2,300 candidate bugs, reproduced 1,700 of them, and produced 948 working local privilege escalation exploits against a stock desktop Linux distribution, for about $1.2 million in API credits, or roughly $1,279 per root exploit. That’s not cheap, but for comparison, Pwn2Own has historically paid $20,000 for a single Linux kernel privilege escalation. Local privilege escalation is the step after an attacker gets a foothold: turning an ordinary user account, a compromised web app, or a sandboxed process into full control of the machine. Coupled with even a basic vulnerability in other code, it can allow an attacker to take full control of the system and hide the compromise much more effectively.

OpenAI says it’s working with the kernel community to report the bugs and submit patches, starting with the most critical, and that during the ten days the scan was running, more than 100 other kernel privilege escalation bugs were patched by other contributors, with about 300 more being discussed publicly. The most sobering line in the report is that, for now, a low-privileged account on an unpatched system “should be considered functionally equivalent to root access for a well-resourced threat actor.” It’s been quite a week for kernel developers, and it’s not going to slow down any time soon.

The flood of AI discovered vulnerabilities seems to continue unabated, and it’s easy to feel under attack from them. Consider, however, how often the open source community has called for companies using open source tools and libraries as core elements of their business to help support those tools and community. There’s still a significant burden placed on the community maintainers when almost 2000 bug reports land in a week, but over $1 million investment in securing Linux isn’t nothing, and the patches at least appear to be reasonably scoped and accurate. I’m pretty sure we’d see an article covering Linus’s response if they weren’t.
Continue reading “This Week In Security: More Linux Bugs, Biggest Crypto Theft Ever, Prusa Printers, Residential Proxies” →

Image

Reviving Google Cardboard, Without Google Or Cardboard

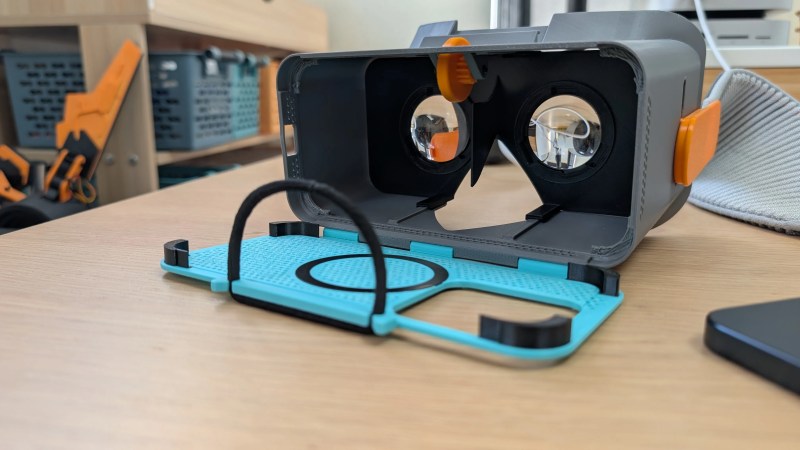
Remember Google Cardboard? The late, unlamented practice of strapping a phone to your face so you could get motion sickness in a virtual environment? [brenpoly] wants you to reconsider, because in the years since Google pulled the plug on mobile VR, phones have gotten really, really good and he’s got a project called CardboardXR on GitHub that the project video enbedded below bills as “A 5$ Apple Vision Pro”

Well, it’s 5$ if you already happen to have a flagship phone like the Pixel 9 Pro or iPhone 15 Pro he’s using for testing– otherwise you’d be out a rather larger chunk of change in order to pick up such a pocket supercomputer. In any case, he’s able to get 6 Degree of Freedom (DOF) tracking from these units, along with using the cameras for passthrough and object detection, hand tracking, and gesture control– everything the big boys net you, in other words. That’s pretty impressive compared to the 3DOF, and zero tracking or pass-through mobile VR used to get you.

He’s also built adjustable optics into his 3D-printed replacement for Google’s old face-hugging cardboard, which you can get on Makerworld.  On the other hand, presumably you could just cut a hole for the camera bumps in one of those if you’re the kind of person who throws nothing out. Either way you’d be using the same lenses; it turns out they’re still available online, so that’s what [brenpoly] spec’d.

All these fancy features aren’t entirely [brenpoly]’s own work: his software is based on Unity which has some slick VR/AR tools and the ability to build in all the relevant machine learning models for things like hand tracking. He’s also taking some major inspiration from the Google Cardboard SDK, which Google open-sourced back around the time they gave up on it. It’s still a very impressive project regardless of the toolchain involved, though there’s a certain irony that [brenpoly] is now strapping a phone to his face after his last project we featured  was all about getting him to put it down.

Continue reading “Reviving Google Cardboard, Without Google Or Cardboard” →

Image

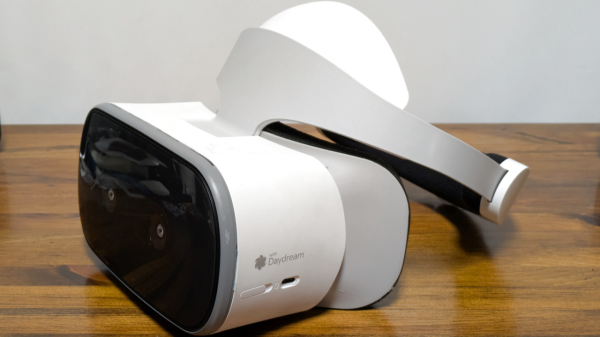
Exploring What’s Left Of Google’s VR Dreams

You’re likely familiar with Google’s Cardboard, and the legions of cheap virtual reality headsets it spawned. By sticking a smartphone to the wearer’s head, all these headsets needed were some basic optics to provide a surprisingly effective VR experience. You may even know about Google Daydream initiative that came a few years later, which not only improved the basic Cardboard design but brought with it new software features such as VR-specific improvements to the Android operating system and a version of the Play Store dedicated to 3D games and applications.

ImageBut unless you’re a true Google devotee, what you may not know is that the search giant partnered with Lenovo to produce a stand-alone Daydream headset called the Mirage Solo in 2018. A full year before the Oculus Quest hit the market, the $399 device combined the guts of a smartphone with a 2560×1440 display running at 75 Hz, a pair of cameras in the front that let it see the world around the user in three dimensions, and a gyroscopic handheld controller to provide an immersive VR experience without having to be tethered to a computer. In addition to the standard consumer version, there was even a “Business Edition” of the headset specifically marketed to schools, offices, and hospitals as a way to deliver VR content without having to invest in any additional infrastructure.

So why isn’t the Mirage Solo better known? Because in classic fashion, just a few years after it was released, Google decided they were no longer interested in virtual reality and shuttered the entire Daydream program. The software components it introduced were stripped out of Android, the 3D Play Store was taken down, and the back-end mechanisms necessary to register new headsets were turned off. Almost overnight, the Mirage Solo became a stereoscopic paperweight.

Or at least that was the official story, anyway. I recently came across a Lenovo Mirage Solo at a thrift store for $25, and despite my initial Internet searches strongly indicating that it would probably be worthless, it seemed worth the gamble to find out for myself.

Continue reading “Exploring What’s Left Of Google’s VR Dreams” →

Image

This Week In Security: Flock Cameras Are Old, Microsoft Patches Patches, And Researchers Attack SSH

Leak site Distributed Denial of Secrets has released a dump of the filesystems of a Flock camera, and Micah Lee has published a dive into the contents.  Apparently the Flock security model did not include “angry citizens with a hacksaw in the middle of the night” in the physical security category.

The first thing Micah notes is that the Flock hardware runs Android 8.1 (for those not keeping track, the current Android release is Android 17 released in June 2026).  The version of Android running on the Flock camera was last patched in June of 2018, and the Linux kernel (3.18.71) is over nine years out of date, and the 3.18 series went end-of-life in 2019.

You might assume “wouldn’t an operating system this old have known vulnerabilities?”, and you’d be completely right.  Micah calls out two in particular, one in the Qualcomm GPU which allows any program to manipulate kernel memory and gain root (similar, yet simpler, than the spate of kernel vulnerabilities this year that allowed manipulating memory via the disk IO cache), and the “WrongZone” vulnerability which allows a process to escalate to root via socket handling errors.  You might also guess both of these have been patched, and again, you’d be right, in 2021 and 2018 respectively.

Digging deeper, Micah discovers that API keys with access into the Flock infrastructure appear to be hard-coded into the binaries.  Each camera appears to request credentials from an authentication server, using the MAC address of the camera.  After obtaining the credentials from an Okta Auth0 sign-in service, the Flock stores them, in plain text.

Also stored on the camera unencrypted are logs and position data:  The camera dumped to Distributed Denial of Secrets came from a suburb of Milwaukee. Continue reading “This Week In Security: Flock Cameras Are Old, Microsoft Patches Patches, And Researchers Attack SSH” →

Image

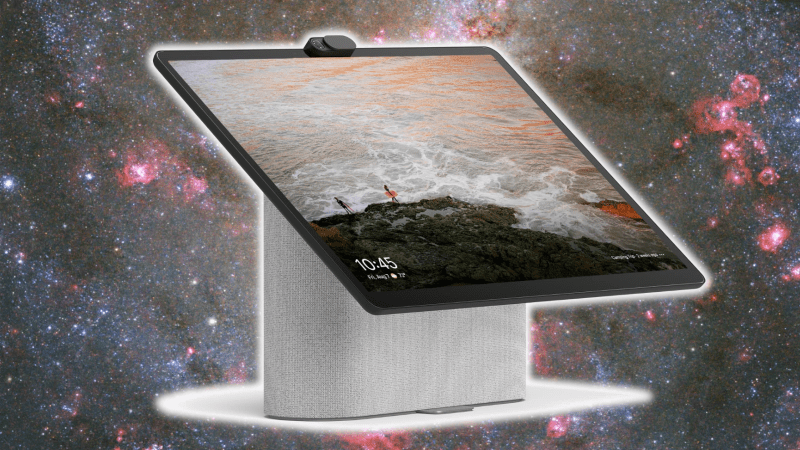
Meta Portal Given New Life As Extended Display

The Meta Portal and associated devices are effectively defunct, having been abandoned by the company in 2022. If you’ve still got one at home, you might be wondering what to do with it. That’s where Wormhole Display from [pgodlews] comes in handy.

The thing about the Meta Portal, and much of the rest of the related lineup, is that they were effectively just heavily branded Android tablets. The screens and speakers were good, and the basic functionality was all there — albeit locked down somewhat to prevent users from easily repurposing them at will. However, it’s possible to enable Android Debug Bridge (ADB) and turn the device to doing your own bidding.

To that end, [pgodlews] built Wormhole Display as an APK that can be dropped on to the Meta Portal to make it an extendable display for Apple devices. It shows up via AirPlay, letting you use it as a wireless display for your Mac, iPhone, or iPad. You can do screen mirroring or use it as an extended display, as desired, including use of the Portal’s speakers if needed. Under the hood, it’s an Android port of UxPlay, a Unix AirPlay server which uses Android’s MediaCodec and AudioTrack in place of GStreamer to take advantage of the Meta Portal’s onboard H.264 decoder.

Extended displays can be incredibly useful, so if you’ve got an old Meta Portal laying around, consider putting it back to work. We’ve seen it done with e-readers, too. If you’ve got your own hacks to repurpose old, forgotten hardware, don’t hesitate to let us know on the tipsline!

Image

This Week In Security: What’s In A Name, The AI Bugpocalypse Hits Everyone, OpenWRT Flaws, And Duress Passwords

The great thing about standards is there’s so many to pick from, right?. (Insert obligatory XKCD #927 here.) Several companies have developed naming schemes to refer to groups of attacks, and now Google has too.

Sometimes, malware, ransomware, or exploit groups name themselves: “Shinyhunters”, “LapSus$”, “Cl0p”, “Lockbit”, and so on. For the groups that don’t advertise their presence, identification and naming can be more difficult. Mostly state-run affairs that didn’t want to draw attention to themselves, these Advanced Persistent Threats (APT) groups were originally simply given numbers. APT28 refers to the Russian GRU Intelligence Directorate suspected of hacking the Democratic Party email servers, APT38 is a North Korean governmental agency involved in financial and crypto currency theft.

Multiple companies and agencies have developed naming schemes to make referring to threat groups easier, typically including a regional identifier as well. CrowdStrike naming uses name groups like “Bear” group for suspected Russian actors, “Panda” for China, “Spider” for unattributed crime groups, while Microsoft uses “Blizzard”, “Typhoon”, and “Tempest”.

Google, deciding there weren’t enough classifications already, now introduces “RELIC”, “CASTLE”, and “COMET”. Of course, each naming organization has dozens of other classification groups as well, but now the next time you hear about an attack being attributed to “Scattered Spider” you know it’s the CrowdStrike name for a crime group.

Critical OpenWRT DHCP Flaw Fixed

The Hacker News reports on a major release of OpenWRT which includes fixes to the odhcpd server, the embedded DHCPv4 and DHCPv6 server written by OpenWRT.

The bug is a straight-forward stack style attack where a buffer is allocated, but not length-checked against the data required to reply to a malformed request. OpenWRT runs on a wide range of devices, but one of the most popular legacy platforms still in use, the MIPS processor architecture, lacks most modern security protections against stack-based attacks, making this attack sting more than it might on other architectures.

The latest OpenWRT releases also fix issues in the uhttpd embedded web server, multiple issues in the LUCI web configuration interface that allowed attackers to inject cross-site scripting content and Linux kernel security fixes. If you run a direct OpenWRT build on your equipment, update! These bugs will have an extremely long tail however, with tens of thousands, or likely more, OpenWRT-based devices that will never see updates.

The company behind several of the findings, Hacker House, say they used multiple AI tools and both open and frontier models to discover the bugs, then manual review and testing to confirm before reporting.

Cisco to Stop Assigning (some) CVEs

Cisco has announced it is moving to a twice-monthly patch cycle. Additionally, Cisco will no longer assign CVEs to each bug in the release.

Cisco says this is in reaction to the rapid increase in bugs found by AI tools, and that “Assessing security risk CVE-by-CVE and applying point mitigations is no longer fit for purpose.” Cisco will still assign a CVE to a bug that “requires compensating controls” or is known to be exploited.

It seems like it will be business as usual for the most severe bugs, but it will be interesting to see what happens when exploits are found for bugs which did not get a CVE in a prior release.

Microsoft Suggests Three-Day Patch Race

Microsoft is now recommending a 3 day patch window for new patches. This is, to say the least, an “aggressive” schedule for applying new patches, given the recent track record of issues introduced by patches.

A update that crashes is inconvenient on a home computer — even more so if it’s your parent’s computer — but could be catastrophic when it brings down an entire corporate fleet. Most large organizations have their own internal patch schedules and internal testing requirements before patches are deployed, delaying the patch process further.

Systems like the CISA KEV database, a list of vulnerabilities known to be actively exploited, are in place to help identify the most important issues. With repeated record-breaking numbers of vulnerabilities pushed in Patch Tuesday and the decreasing support of the KEV and related vulnerability indexing systems, the load on IT departments and administrators is becoming impossible.

The AI “bugpocalypse” is finding record numbers of vulnerabilities, while also closing the timeline between bug to exploit to hours in some cases. The time between bug and exploit then drives the patch cycle, which means less testing. With less testing, the patches are less stable, leading to less trust in rapidly installing them.

Oracle Patches Almost 1500 CVEs

Moving directly from the impacts of the flood of Microsoft security issues, the July 2026 patch set from Oracle included fixes for 1499 security issues and 1434 CVEs over 334 Oracle products.

Oracle is also pressuring administrators to move to a monthly patch cycle, but acknowledges “transitioning to a monthly security patching cadence may require updates to existing operational processes”. Not to worry – there is a Oracle consulting service you can hire to help you patch your Oracle problems.

Linux Patches 323 CVEs in Two Days

After announcing over 400 CVEs in the Linux kernel last week, Linux mainters have announced an additional 323 in the last three days alone. The vulnerabilities cover Bluetooth, Ethernet, USB gadget mode, WiFi drivers, virtualization systems, SMB file sharing, and of course more.

One benefit to the architecture of the Linux kernel is that typically all the fixes will arrive in a single kernel update, but when almost every week brings critical updates and a new kernel, patch fatigue is a real thing. Either users stop applying every update, or the uptime and testing requirements of a company prohibits constantly updating and changing servers.

Duress Passwords Aren’t Necessarily a Good Thing

The security-hardened Android variant Graphene, is in the news this week for the use of duress passwords.

A duress password is a mechanism where a second PIN or password can be used to initiate a device wipe. The hope is that in a situation where you are compelled to unlock a device, providing a password which then wipes the device is a preferable option.

The legality of a duress password depends on the environment it is used in. The United States Customs and Border Patrol claims that by wiping a device during an inspection at the US border, Samuel Tunick destroyed evidence and property in violation of federal laws. The issue is compounded because the stop happened at a border, where many US laws against search, seizure, and the availability of a lawyer are suspended, even for US citizens.

The inclusion of duress passwords, and their cousin hidden encrypted volumes, can sound like a good idea, but can place users in serious danger when in situations with less strict rules of law. Having the ability to wipe data sounds great in isolation, but protestors, human rights workers, and other targeted groups have faced direct and physical threats under some regimes. Facing retaliation for wiping a device, or facing physical violence before providing an unlock code out of fear that it might wipe a device, can be a real risk for some.

FreeBSD Fixes a WireGuard Bug

FreeBSD has issued a security update pertaining to the WireGuard VPN implementation.

WireGuard is a modern VPN with excellent performance even on low-end systems, and which has implementations on basically every platform. The FreeBSD implementation, however, didn’t fully validate VPN packets, accepting packets without checking one of the cryptographic validation measures.

Attackers are able to inject data to a FreeBSD WireGuard implementation if they are able to guess some attributes of the connection, and able to fully modify the data in the VPN if they are able to intercept the packets.

The bug impacts any FreeBSD user of WireGuard. FreeBSD has released updated kernels.

Hackaday Links Column Banner

Hackaday Links: July 26, 2026

At a time when so-called “artificial intelligence” seems inescapable, we were encouraged to see news that Amazon will be cracking down on third-party sellers that use AI-generated images for their product listings. They won’t be prevented from using the images, but they will need to clearly indicate that they don’t represent reality and were produced via artificial means. This comes in response to a recently enacted New York law that requires the disclosure of AI in advertisements.

Image
Will this be the end of the cat sleeping bag?

But it’s not quite a clear cut as it might seem on the surface, as the New York law is actually about AI-generated people rather than products. Specifically, it’s designed to make it clear when a “synthetic performer” has been used in place of a human actor. As such, it would appear that the easiest way for Amazon sellers to dodge the new rule is to simply not include any humans in their AI slop images and videos. In other words, they can continue to post fake pictures of products without having to inform the consumer so long as they don’t show a fake person holding it.

Under normal circumstances we’d leave something like this next one for our weekly security column, but the utter lack of security in the Pope’s official “Click To Pray” mobile application revealed by researcher BobDaHacker on Friday is just too good a story to pass up. For one thing, who knew that there was an “official” prayer app? We don’t dabble in theology around these parts, but we’re fairly sure the good book didn’t mention anything about requiring a smartphone to give praise.

Continue reading “Hackaday Links: July 26, 2026” →